Ready for your TISAX assessment in the automotive industry

TISAX is the assessment German car manufacturers ask of their suppliers. Tidal Control sets up the VDA ISA control questions, tracks the maturity level per question and has the evidence ready for your audit provider.

  • 45 VDA ISA control questions
  • Maturity per question
  • Together with ISO 27001
  • Built in the EU
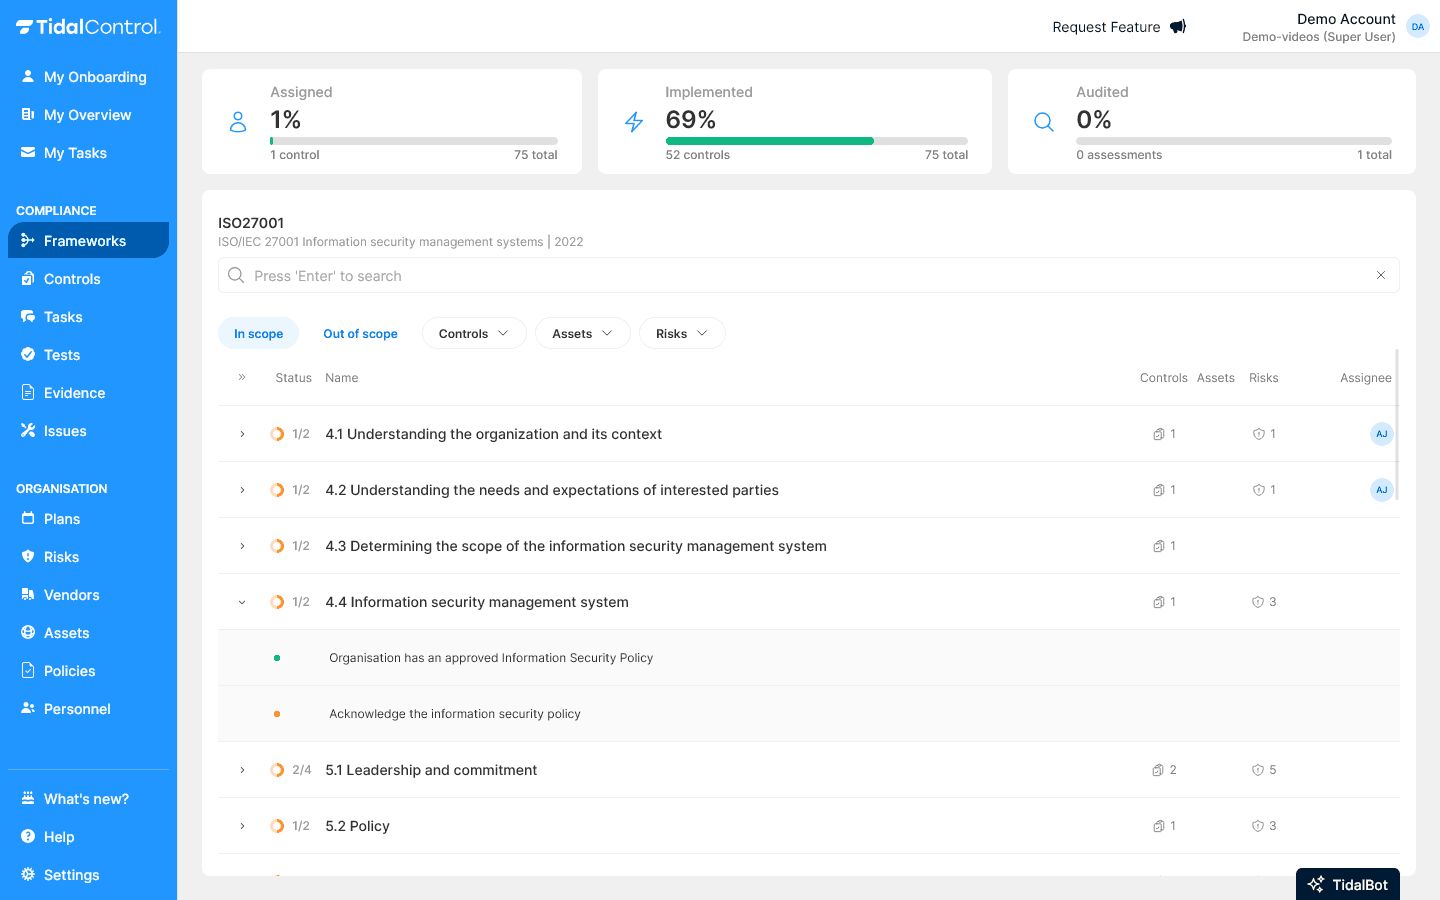
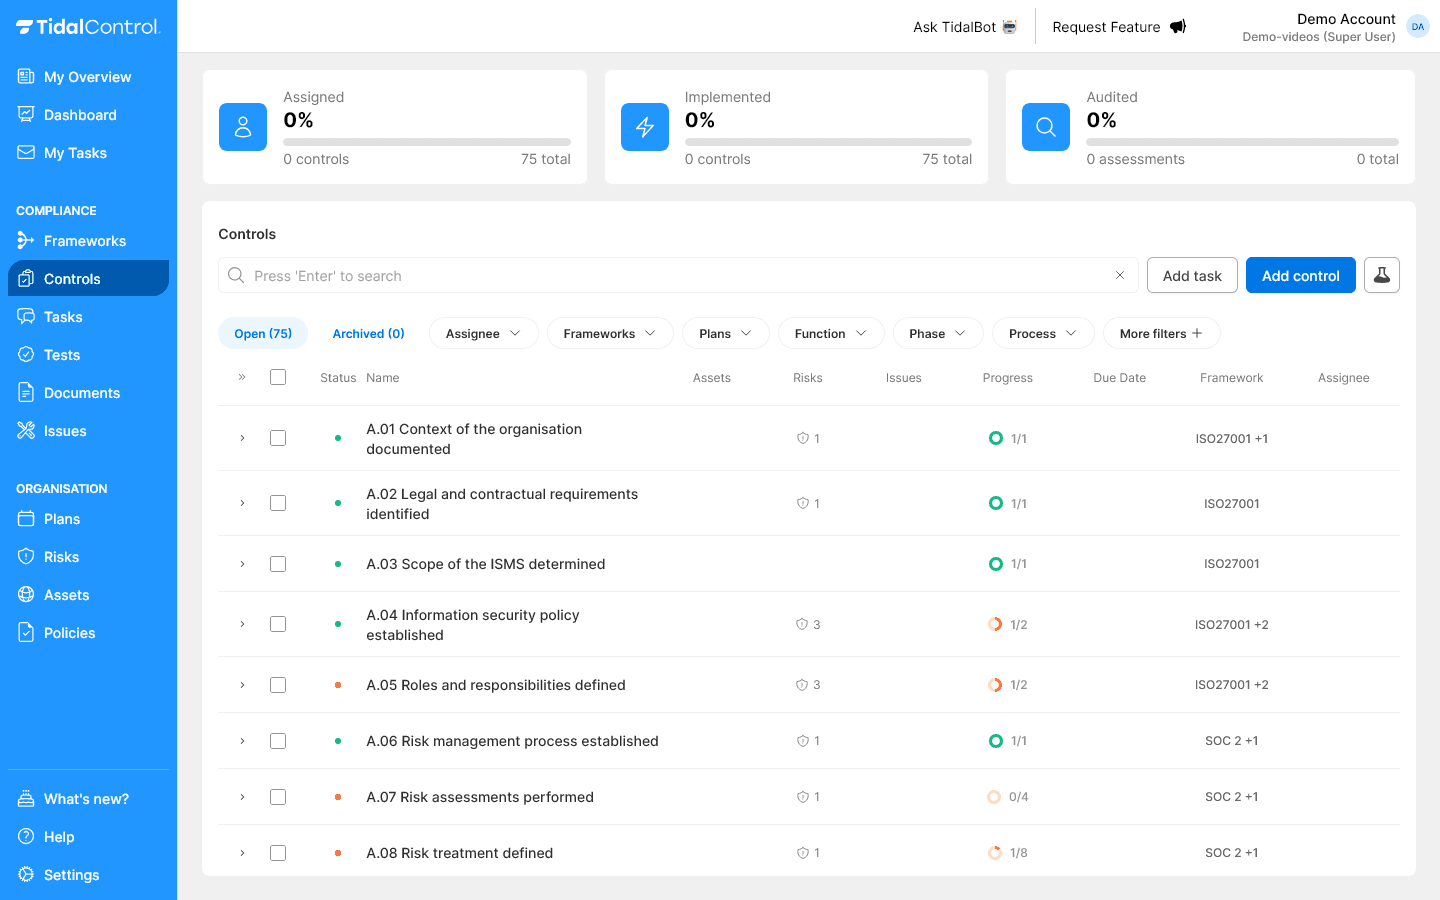
The TISAX overview in Tidal Control with the maturity level per control question

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From self-assessment to TISAX label

How long it takes depends on your assessment level and what is already in place. Tidal shows what is expected of your team at each step.

  1. Step 1

    Scope and objectives

    Which sites and assessment objectives your customer asks for.

  2. Step 2

    Self-assessment

    Recording the current maturity level per control question.

  3. Step 3

    Towards level 3

    Putting measures in place until every question reaches the target.

  4. Step 4

    Assessment

    Your audit provider checks your answers and evidence.

  5. Step 5

    TISAX label

    The label, shared with your customers through the ENX portal.

  6. After that

    Three years of upkeep

    Level and evidence kept current until the next assessment.

How Tidal helps with the VDA ISA

The Information Security module of the VDA ISA has 45 control questions, split into chapters from policy to suppliers. Tidal sets them up for you, with the level, an owner and evidence for each question.

control questions
45control questions
years valid
3years valid

VDA ISA, Information Security

  • 1

    Policy and organisation

    Policy, roles, risk management and review of information security.

  • 2

    Human resources

    Agreements, awareness and confidentiality.

  • 3

    Physical security

    Access to sites, buildings and rooms.

  • 4

    Identity and access

    Accounts, rights and authentication.

  • 5

    IT security

    Encryption, logging, vulnerabilities and networks.

  • 6, 7

    Suppliers and compliance

    Suppliers and legal requirements, including privacy.

TISAX in brief

TISAX (Trusted Information Security Assessment Exchange) is the information security assessment of the automotive industry. It is run by the ENX Association on behalf of the German VDA. An accredited audit provider assesses you against the VDA ISA, and you share the result with your customers. A TISAX label is valid for three years.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • Access to German car manufacturers and their chain
  • One assessment for many customers
  • Insight into maturity per subject
  • Fewer one-off security questionnaires
  • Work that also counts towards ISO 27001

How you work on TISAX in Tidal

From risks to suppliers: your TISAX preparation in one place.

Controls management

Control management that works your way

Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

Controls management in Tidal ControlControl management that works your way
Risk assessment

Risk assessments that work

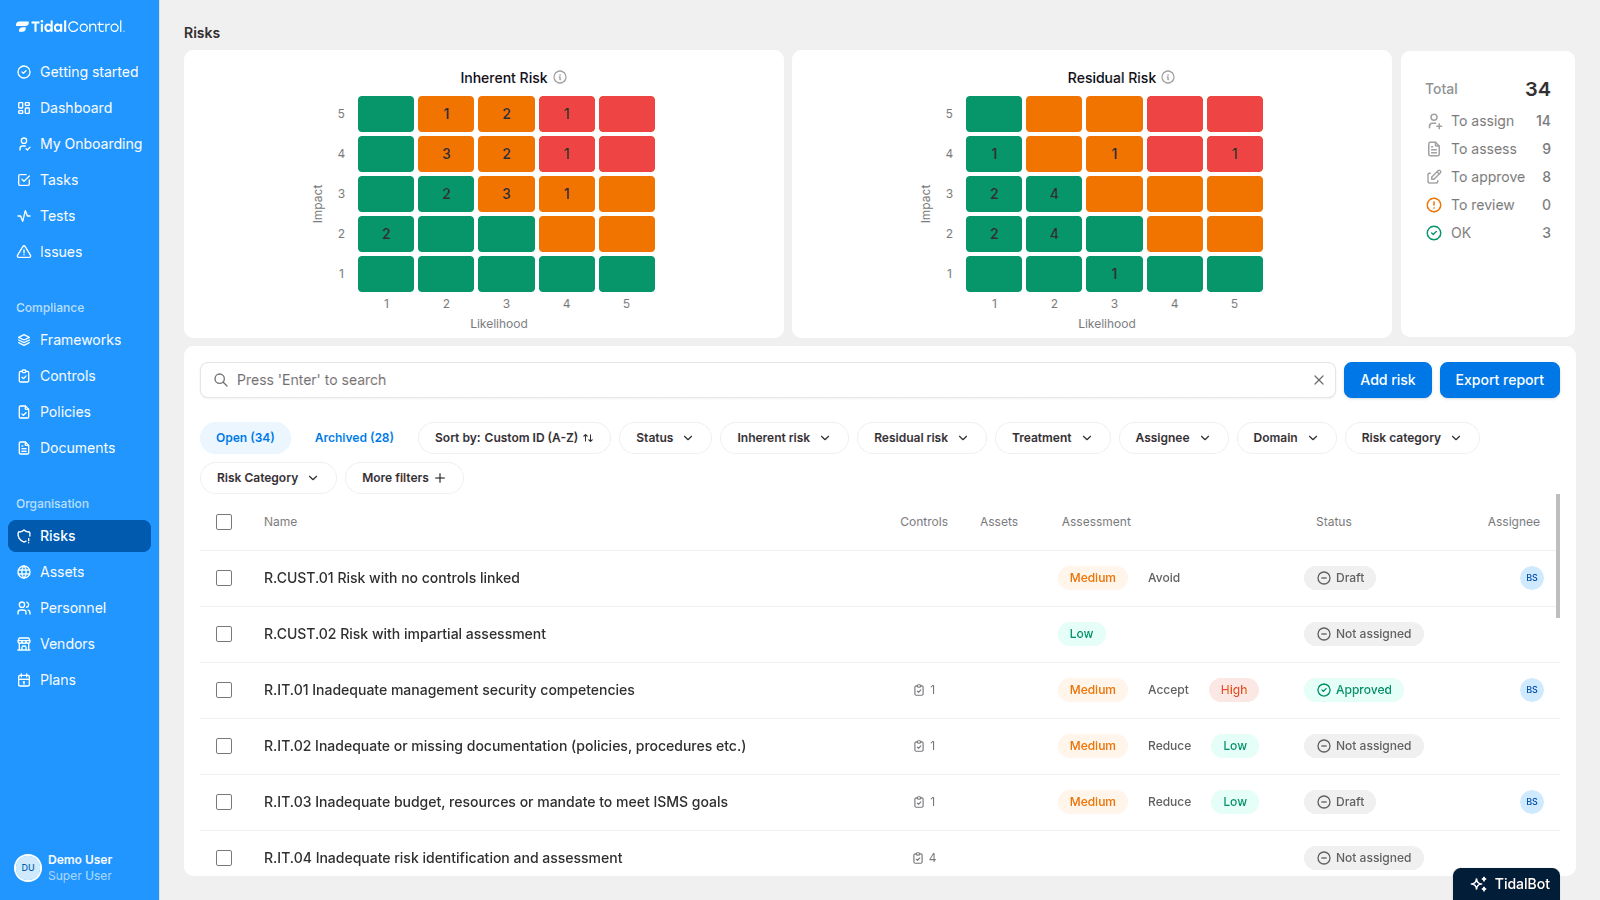
Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

Risk assessment in Tidal ControlRisk assessments that work

Policy center

Policies without the hassle

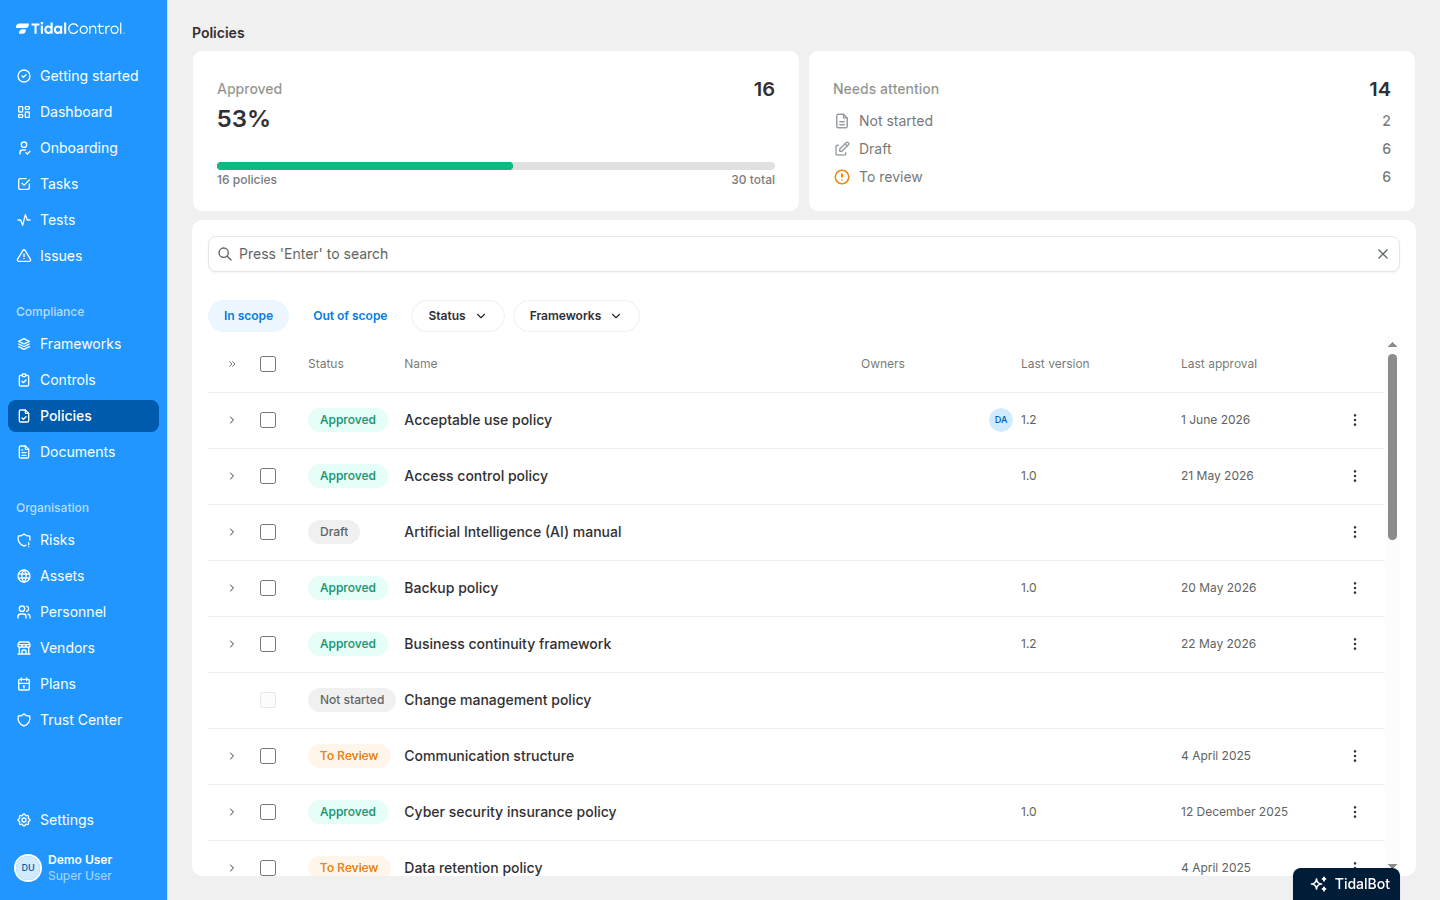
Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

Vendor management

Supplier risk assessment that actually works

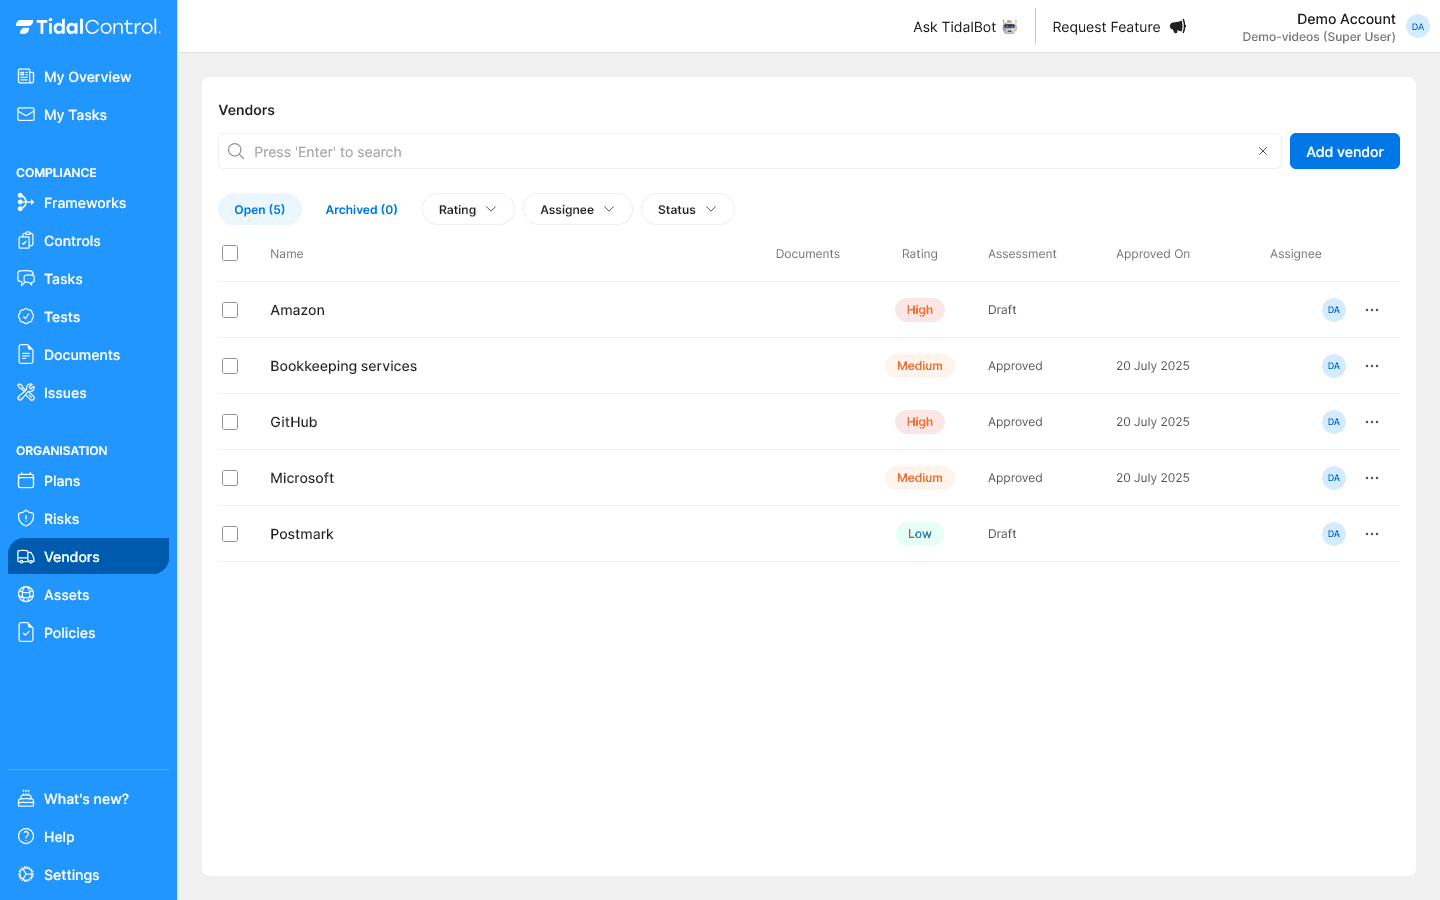
Transform supplier risk assessment from a time-consuming task into an automated process that helps your business grow. Add vendors in seconds with our vendor database that automatically fills in all important details, from privacy policies to SOC2 reports. Our intelligent system then automatically assesses risks and helps you make the right decisions.

Vendor management in Tidal ControlSupplier risk assessment that actually works

Personnel & onboarding

Employee compliance without the spreadsheet

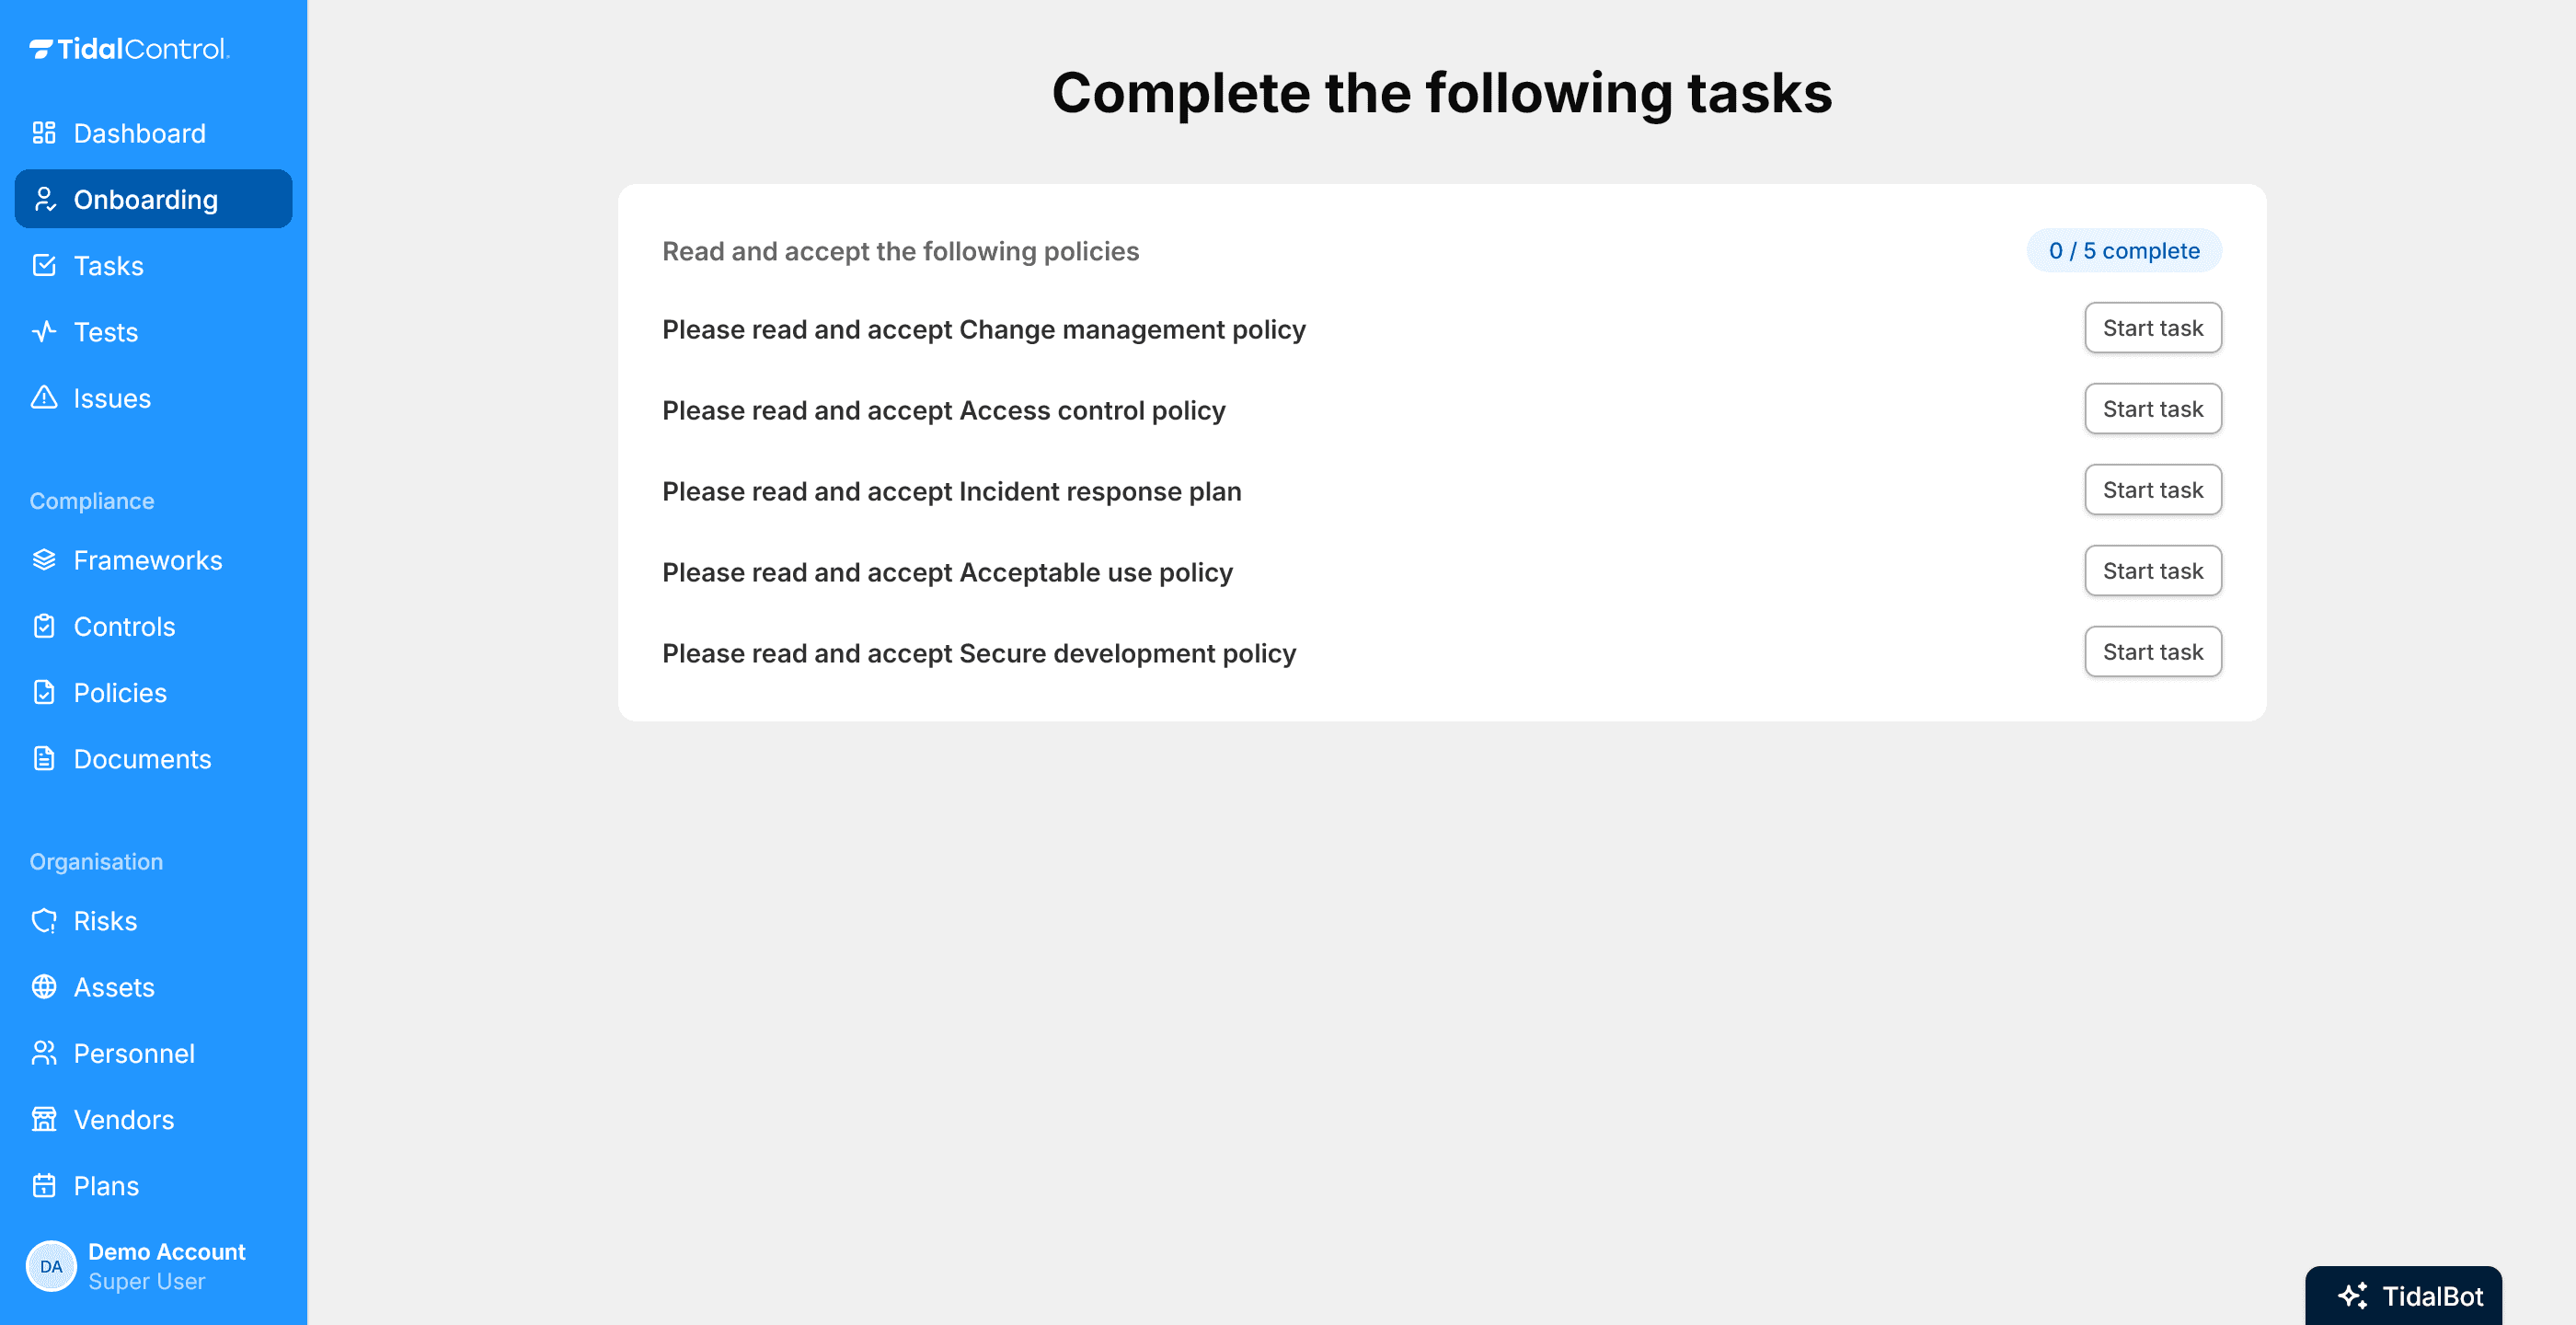
The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

Issues management

Track and resolve issues - all in one place

Simplify issue management with a centralised system that handles everything from audit findings to improvement opportunities. Keep your team aligned and ensure nothing gets missed with clear ownership, priorities, and automated tracking.

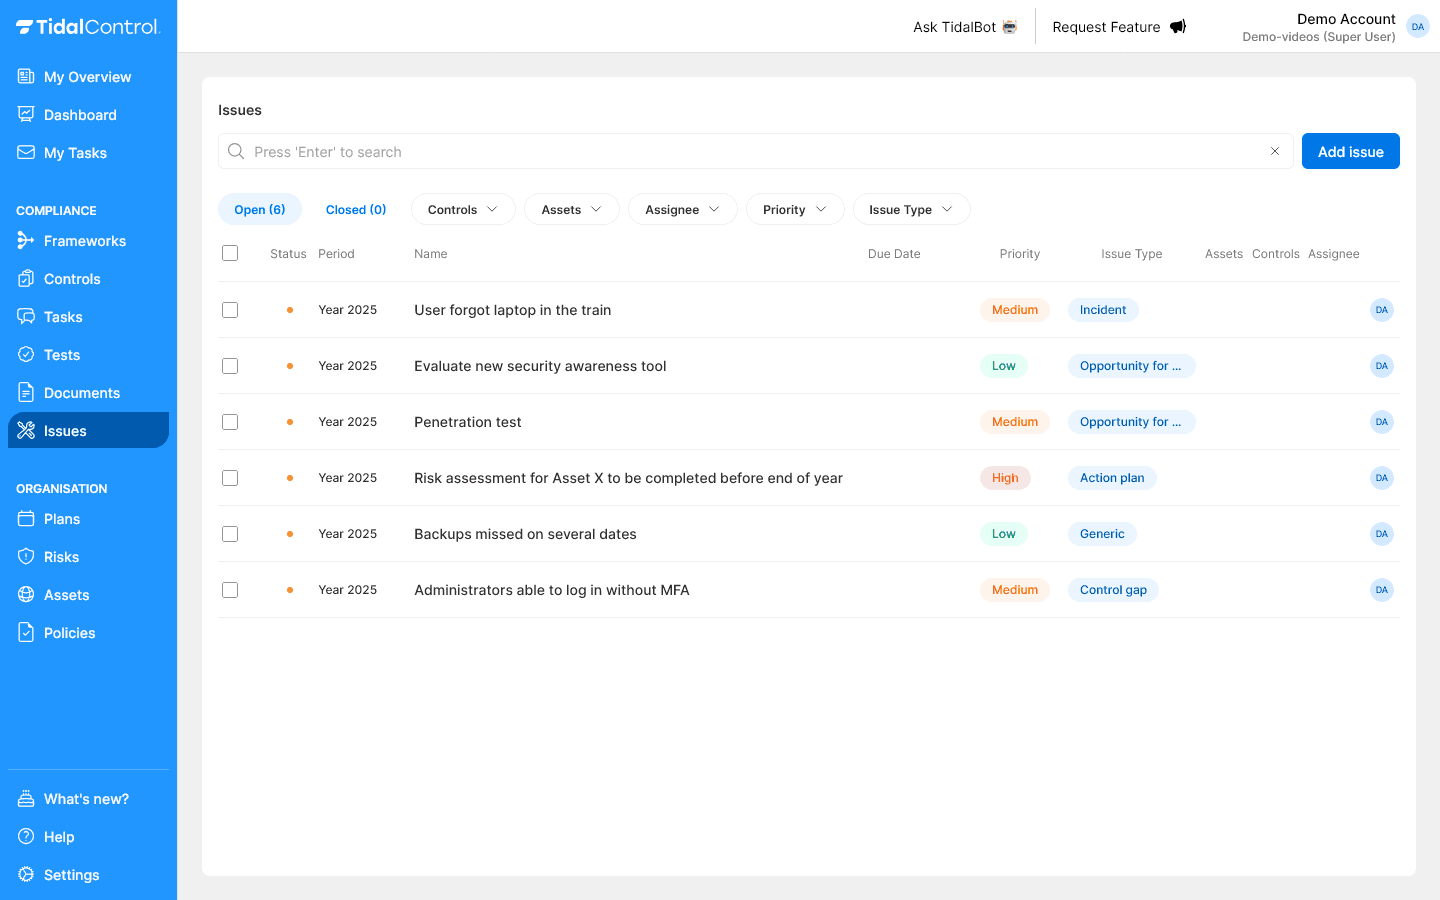
Issues management in Tidal ControlTrack and resolve issues - all in one place

Integrations

Automation makes life more fun!

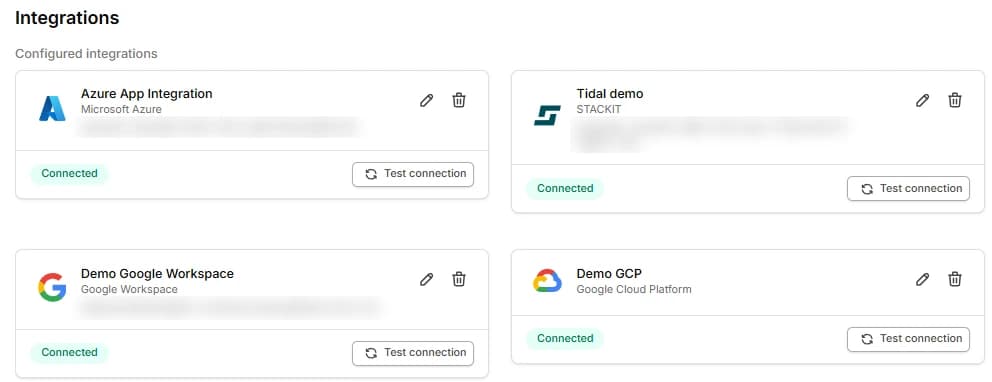
Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • Control questions
    Manual

    The VDA ISA in Excel

    With Tidal

    All 45 questions with level and owner

  • Maturity

    Manual

    An estimate each time

    With Tidal

    Tracked per question

  • Evidence

    Manual

    Collected just before the assessment

    With Tidal

    Ready per question

  • TISAX and ISO 27001

    Manual

    Two projects side by side

    With Tidal

    One set of controls, evidence once

  • After the label

    Manual

    Three years idle, then start again

    With Tidal

    Continuously current

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

See all success stories

Integrate with your existing tools

TISAX software and the assessment

TISAX preparation often happens in the Excel version of the VDA ISA. That works for a self-assessment, but the evidence, owners and follow-up then sit somewhere else.

TISAX software sets up the 45 control questions, tracks the level per question and links each question to measures and evidence.
You see which questions are still below target before the audit provider does.

Frequently asked questions

TISAX (Trusted Information Security Assessment Exchange) is the assessment and exchange mechanism the German automotive industry uses for information security at suppliers and service providers. It is run by the ENX Association on behalf of the German Association of the Automotive Industry (VDA). Assessments are made against the VDA Information Security Assessment (VDA ISA) catalogue, and the results are shared with your customers through the ENX portal.

Tidal holds the Information Security module of the VDA ISA 6.0.3: 45 control questions, each with its objective and its must, should, high and very high requirements. Prototype protection and data protection are separate TISAX assessment objectives and are not included.
TISAX uses assessment levels that decide how thoroughly an audit provider checks your answers. Assessment level 1 is a self-assessment that customers rarely accept. Assessment level 2 is a plausibility check of your self-assessment with evidence and an interview, usually remote. Assessment level 3 is a thorough check, usually on site. Your customer decides which level you need, based on the protection need of the information you handle.

Each control question is rated on a maturity scale from 0 to 5. The target is level 3, established: the process is documented, applied and its effectiveness is checked. Tidal tracks the maturity per control question, so you can see which questions are still below target before the audit provider does.
A TISAX label is valid for three years. During that time your information security has to stay at the assessed level, and a customer can ask for a new assessment when the scope changes. Tidal keeps the controls, tasks and evidence current, so the next assessment starts from records instead of a new project.

The VDA ISA is based on ISO/IEC 27001 and 27002, so a supplier with an ISO 27001 certificate already meets much of it. TISAX adds automotive-specific requirements and the maturity rating, and the two are assessed separately. In Tidal you link the VDA ISA control questions to your ISO 27001 controls, so evidence counts for both.