Tidal blog
Written by Tidal's compliance experts: guides, success stories and product updates on ISO 27001, NIS2, NEN 7510 and more.
Latest articles
The most recent posts, on every topic.
What's New | July 2026
August's Tidal update brings the public Trust Center, seven new integrations, expanded Azure tests, ISO 42001 AI governance support, and vendor history.

From first compliance step to audit with 0 findings: how Aivory achieved ISO 27001 and NEN 7510 in three months
Aivory earned ISO 27001 and NEN 7510 in three months with zero audit findings. See how this dental AI start-up moved fast without cutting corners.
Controls: what are they and how do you use them?
What are controls, what types exist and how do they work within ISO 27001? Learn how to set up effective controls management in your organisation.
ISO 27001
From first step to certificate.
Performing a risk assessment: methods, models and tools
Learn what a risk assessment is, which methods exist, how to work through it step by step, and which mistakes organisations make most often.
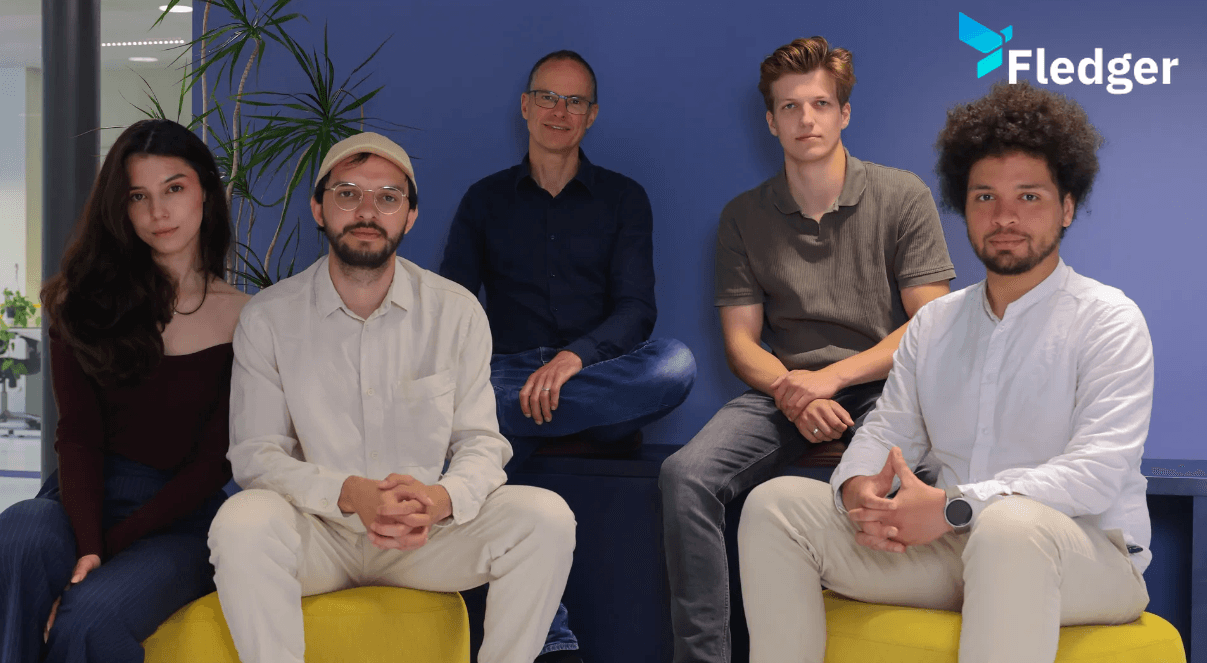
From compliance roadbumps to ISO 27001 with confidence: The story of Fledger.ai
Fledger got stuck with an American platform, and achieved ISO 27001 with Tidal Control and Riskwork as partners who built on their existing foundation.
What is GRC and why do modern businesses need a GRC platform?
GRC stands for Governance, Risk and Compliance. What it means, why silos break down, and when a GRC platform makes sense for your organisation.
NIS2
What the new rules mean for your organisation.
NIS2 for SaaS: what do you need to arrange now?
Does your SaaS company fall under NIS2? Read about direct and indirect scope, DORA overlap for fintech, four core obligations and five concrete steps.
SOC 2 for startups: becoming compliant without losing speed
Discover how startups implement SOC 2 without losing their development speed. Practical tips on change management, Type I vs Type II and smart first steps.
NIS2 checklist: what you need to have in order to be compliant
The Dutch Cybersecurity Act has applied since 15 August 2026. These are the six pillars you need to be NIS2 compliant, and what commonly goes wrong.
Subscribe now for monthly updates: what's new at Tidal, framework news, and compliance resources.
By submitting your email you agree to our Privacy Policy.
Success stories
How customers reached their certificate with Tidal Control.
Triagen explains: how much AI can really speed up your compliance journey
AI doesn't replace compliance, but it does speed up the execution work. Discover how Triagen.ai and Fendix use the MCP integration of Tidal Control.

From trust to demonstrability: How CBYTE uses digital compliance as foundation for scalable growth
Discover how CBYTE transformed compliance from paperwork into a strategic foundation for growth, with automation as the key to scalability.

From standstill to sales: How Dembrane turned compliance into their competitive advantage
Dembrane was losing deals due to missing ISO 27001 certification. Read how they got certified with Tidal Control and got their compliance in order.
New in Tidal Control
What is new in the platform.
What's New | May 2026
Tidal Control adds 8 new integrations, three frameworks including BIO2 and BSI C5:2026, a DORA Register of Information export, and critical issue priority.
What's New | April 2026
Tidal Control's latest update brings MCP AI integration, DORA Register of Information support, Datadog integration, vendor-asset linking, and more.
What's New | March 2026
Tidal adds automated Google Workspace and GCP tests, asset categories, a structured risk approval workflow, and an interactive evidence viewer in this release.
More from Tidal
All articles
What's New | July 2026
August's Tidal update brings the public Trust Center, seven new integrations, expanded Azure tests, ISO 42001 AI governance support, and vendor history.
From first compliance step to audit with 0 findings: how Aivory achieved ISO 27001 and NEN 7510 in three months
Aivory earned ISO 27001 and NEN 7510 in three months with zero audit findings. See how this dental AI start-up moved fast without cutting corners.
Controls: what are they and how do you use them?
What are controls, what types exist and how do they work within ISO 27001? Learn how to set up effective controls management in your organisation.
Performing a risk assessment: methods, models and tools
Learn what a risk assessment is, which methods exist, how to work through it step by step, and which mistakes organisations make most often.
From compliance roadbumps to ISO 27001 with confidence: The story of Fledger.ai
Fledger got stuck with an American platform, and achieved ISO 27001 with Tidal Control and Riskwork as partners who built on their existing foundation.
What is GRC and why do modern businesses need a GRC platform?
GRC stands for Governance, Risk and Compliance. What it means, why silos break down, and when a GRC platform makes sense for your organisation.

ISO 9001 certification costs: what does it really cost?
What does ISO 9001 certification cost for an SME? Real figures for year 1, year 2 and 3, plus the factors that push the price up or down.
What is ISO 9001 and when should you start certification?
ISO 9001 explained: what the standard requires, what certification costs, how long it takes, and what changes with ISO 9001:2026, published 16 September.
Triagen explains: how much AI can really speed up your compliance journey
AI doesn't replace compliance, but it does speed up the execution work. Discover how Triagen.ai and Fendix use the MCP integration of Tidal Control.
DORA explained: what does the regulation mean for your organisation?
What is DORA, who does it apply to, and what are the five pillars? This article clearly explains the Digital Operational Resilience Act for financial organisations.
NIS2 for SaaS: what do you need to arrange now?
Does your SaaS company fall under NIS2? Read about direct and indirect scope, DORA overlap for fintech, four core obligations and five concrete steps.
What's New | May 2026
Tidal Control adds 8 new integrations, three frameworks including BIO2 and BSI C5:2026, a DORA Register of Information export, and critical issue priority.