GDPR compliance you can demonstrate

The GDPR asks not only that you protect personal data well, but also that you can show it. Tidal Control keeps your record of processing, DPIAs, processing agreements and security measures in one place, with evidence for every measure.

  • Record of processing and DPIAs
  • Breaches reported within 72 hours
  • Together with ISO 27001
  • Built in the EU
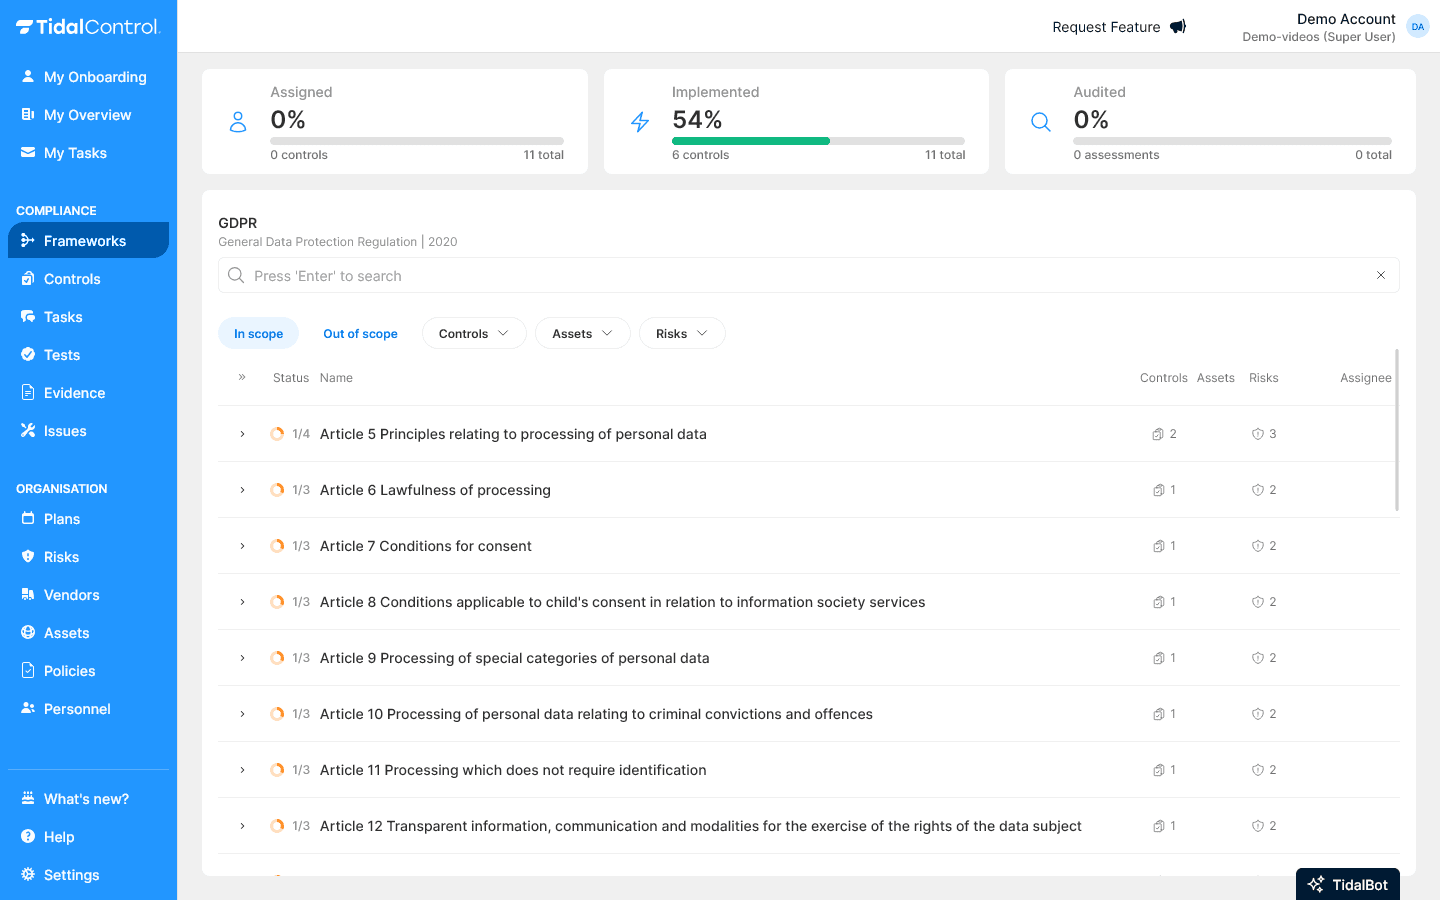
The GDPR overview in Tidal Control with the status of measures and evidence

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From inventory to demonstrable compliance

The GDPR has no certificate. You have to be able to show that you comply and that you keep it up. Tidal shows what is expected of your team at each step.

  1. Step 1

    Inventory

    Which personal data you process, why and with which parties.

  2. Step 2

    Record of processing

    Each processing activity recorded with purpose, lawful basis and retention.

  3. Step 3

    Risk and DPIA

    Risks assessed and a DPIA carried out where the processing calls for it.

  4. Step 4

    Measures and agreements

    Security, processing agreements and privacy notice in order.

  5. Step 5

    Procedures

    Ready for data subject requests and for reporting a breach within 72 hours.

  6. After that

    Maintain and review

    Record, DPIAs and agreements kept current, and a sparring partner for new processing.

How Tidal helps with the GDPR duties

Accountability means you not only comply with the GDPR but can also demonstrate it. Tidal sets up the duties for you, with an owner, policy and evidence for each part.

hours to report a data breach
72hours to report a data breach
policy templates
30+policy templates

GDPR duties

  • Art. 30

    Record of processing

    Each processing activity with purpose, lawful basis, recipients and retention.

  • Art. 35

    DPIA

    A data protection impact assessment for high-risk processing.

  • Art. 15-22

    Data subject rights

    Requests for access, rectification or erasure handled on time.

  • Art. 28

    Processors

    A processing agreement with every party that processes data for you.

  • Art. 32

    Security

    Appropriate technical and organisational measures.

  • Art. 33-34

    Data breaches

    Reported to the supervisory authority within 72 hours, and to data subjects where needed.

The GDPR in brief

The General Data Protection Regulation (GDPR) applies to every organisation that processes personal data of people in the EU. Its core is accountability: you have to be able to demonstrate that you comply. Each member state has a supervisory authority; in the Netherlands that is the Autoriteit Persoonsgegevens.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • Demonstrable compliance for the supervisory authority
  • Trust from customers and data subjects
  • Quick answers to customers' privacy questions
  • Less chance of data breaches and fines
  • Work that also counts towards ISO 27001 and ISO 27701

How you work on the GDPR in Tidal

From record of processing to breach reporting: your privacy programme in one place.

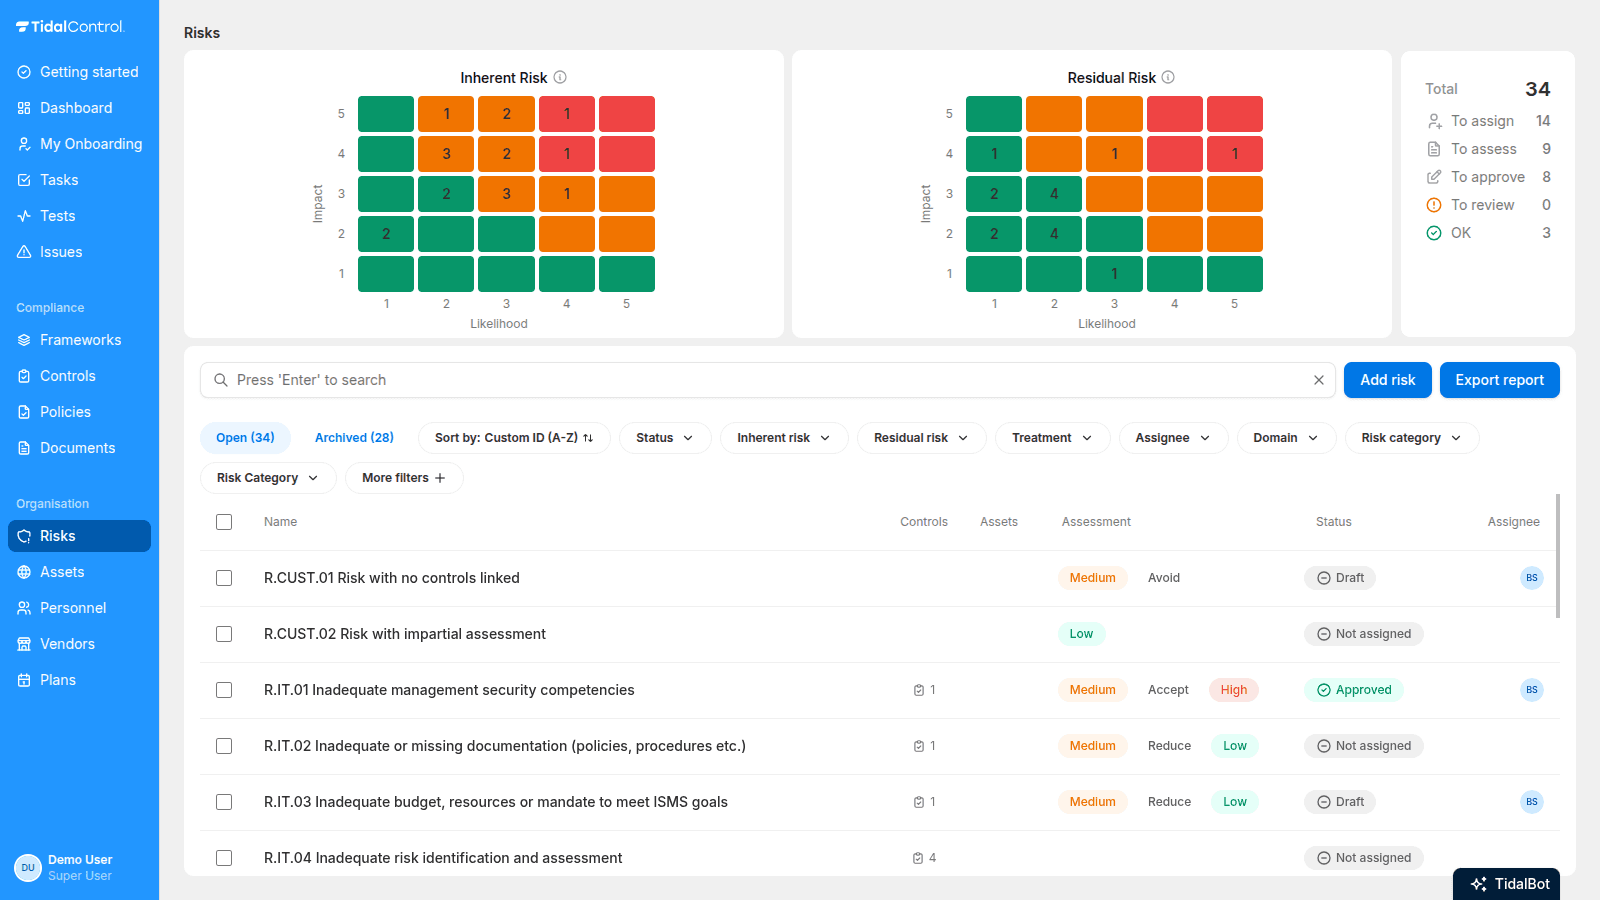
Risk assessment

Risk assessments that work

Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

Risk assessment in Tidal ControlRisk assessments that work
Policy center

Policies without the hassle

Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

Vendor management

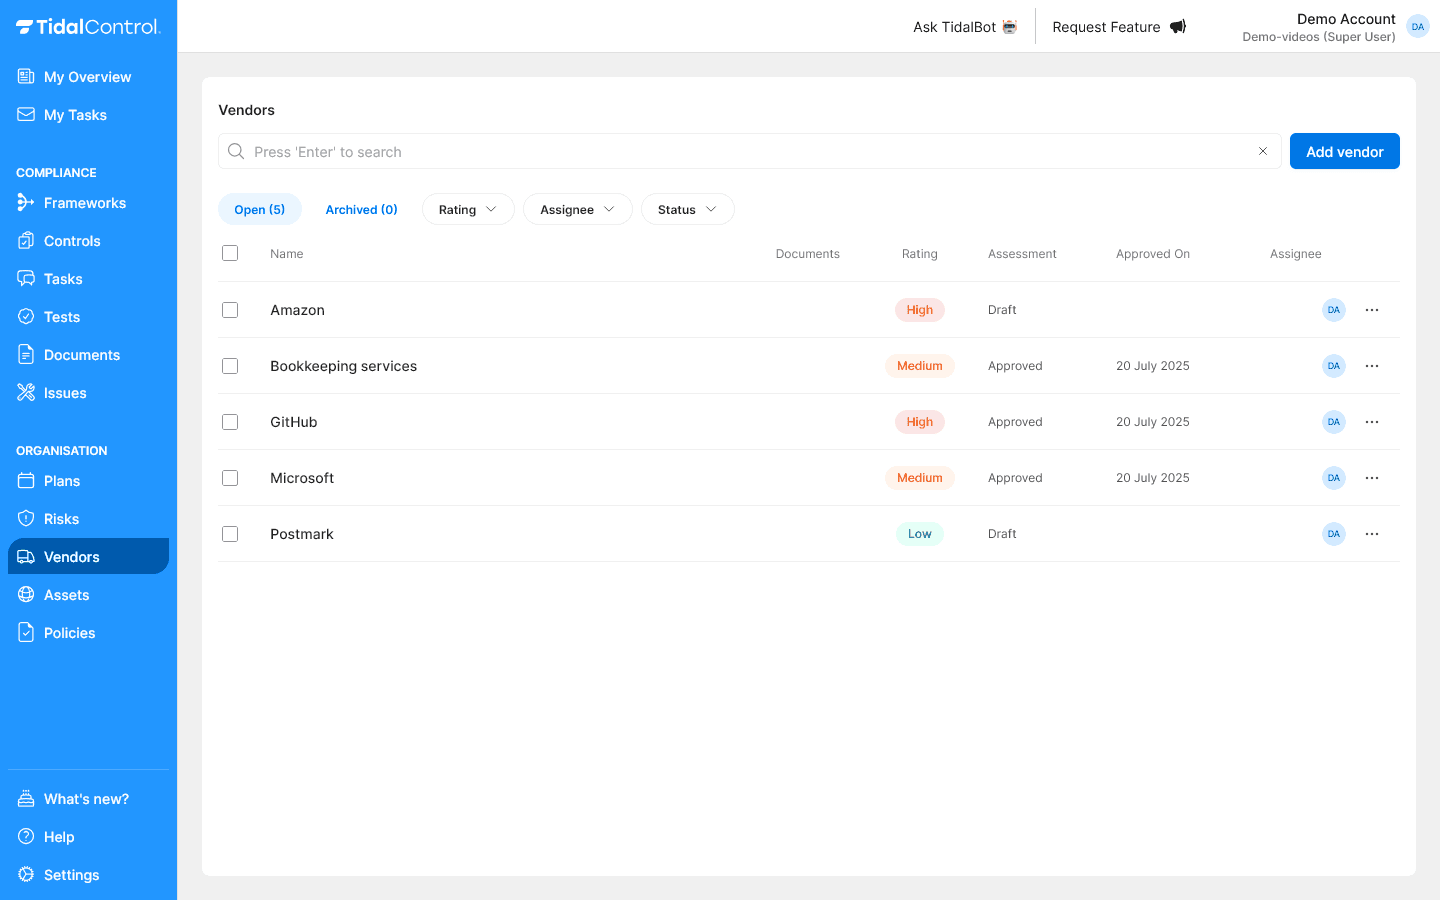
Processors and processing agreements in view

Record for each supplier which personal data it processes, whether there is a processing agreement and when you review it again.

Vendor management in Tidal ControlProcessors and processing agreements in view

Issues management

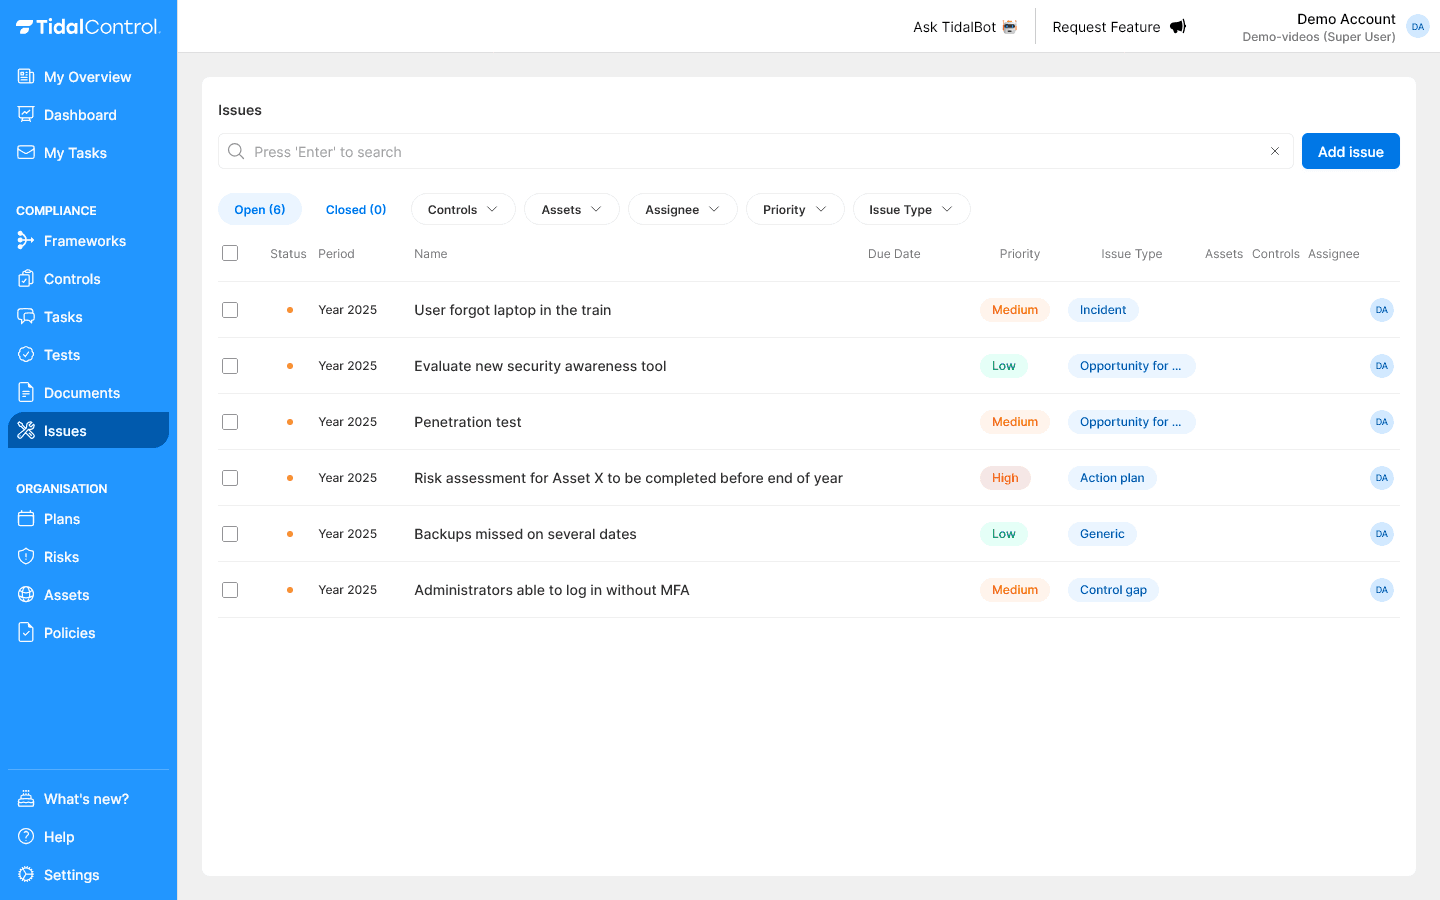
Data breaches recorded, ready to report

Record a data breach with timeline, impact and handling, so you can decide within 72 hours whether and how to report it.

Issues management in Tidal ControlData breaches recorded, ready to report

Controls management

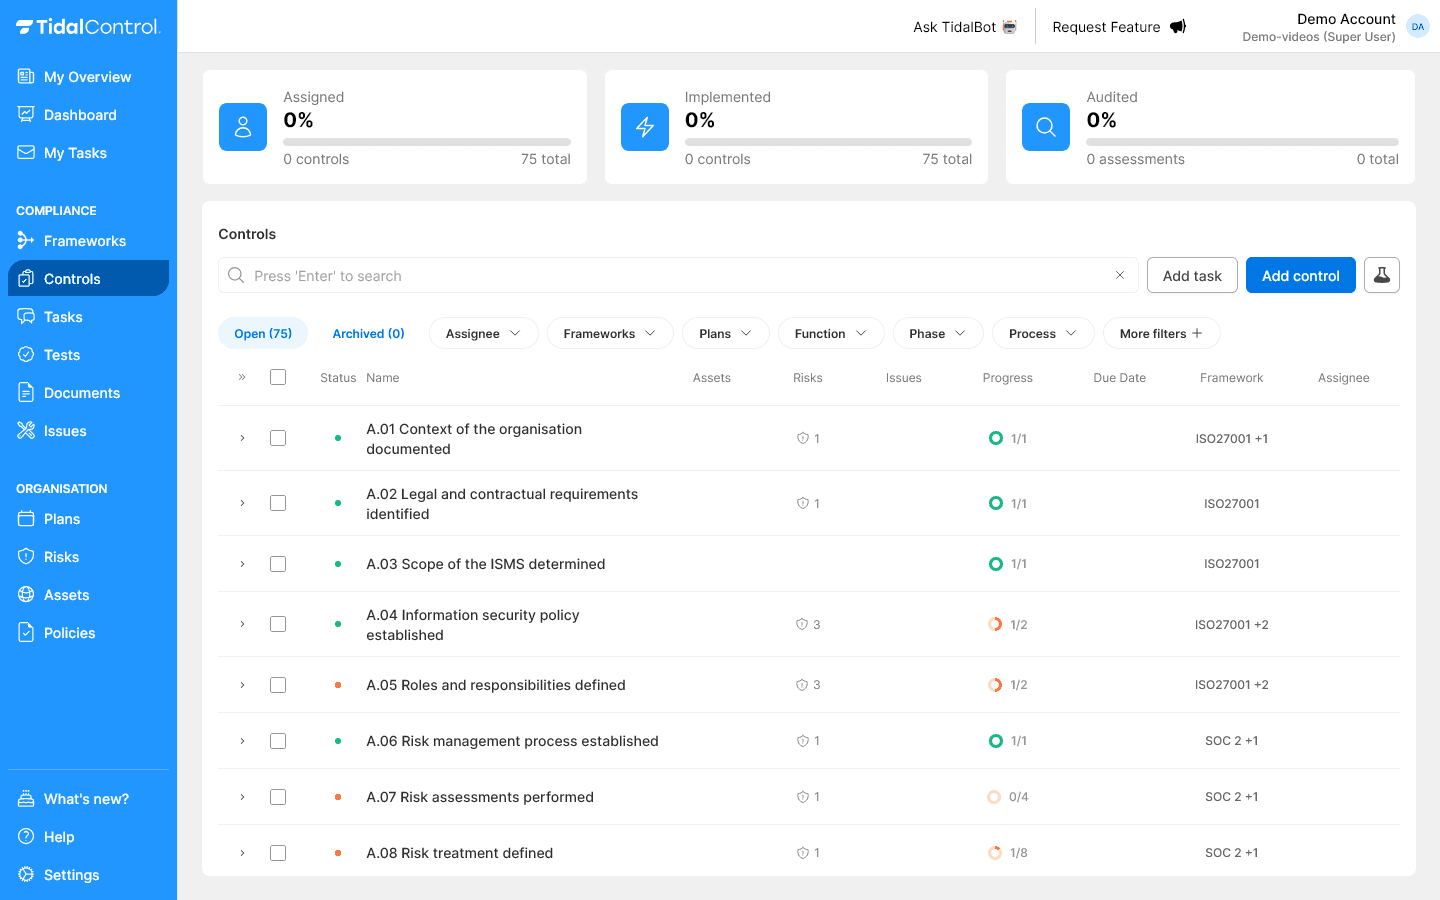
Control management that works your way

Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

Controls management in Tidal ControlControl management that works your way

Personnel & onboarding

Employee compliance without the spreadsheet

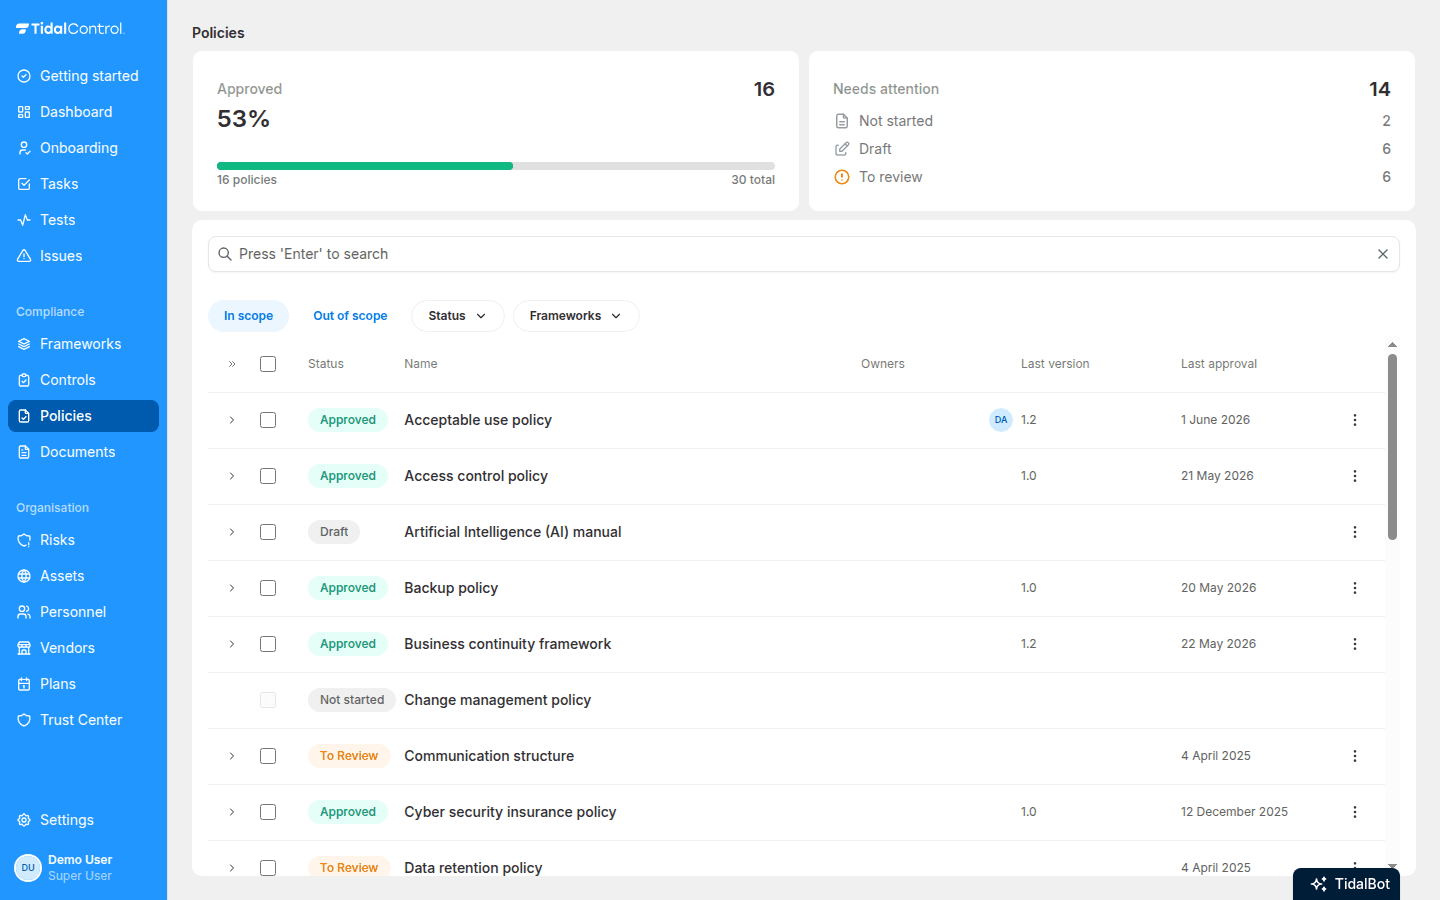
The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

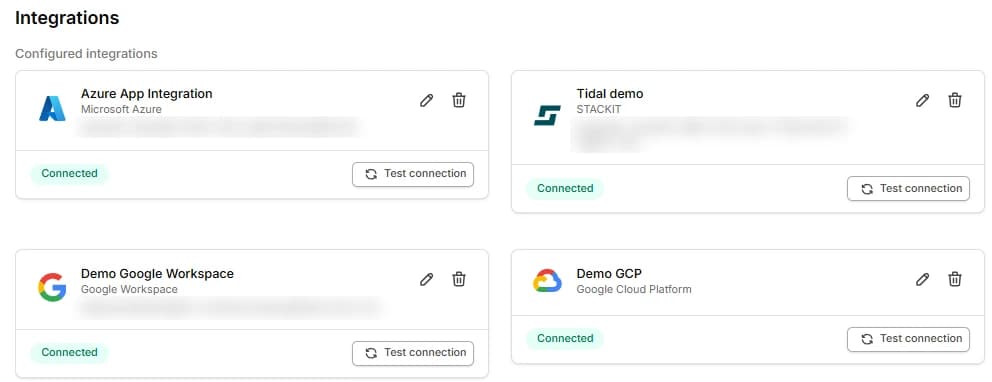
Integrations

Automation makes life more fun!

Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • Record of processing

    Manual

    A spreadsheet that goes stale

    With Tidal

    A record with owners and review dates

  • DPIAs

    Manual

    Separate documents

    With Tidal

    Template linked to risks and measures

  • Processing agreements

    Manual

    Spread across folders and email

    With Tidal

    Recorded per supplier

  • Data breaches

    Manual

    Looking for information when it goes wrong

    With Tidal

    Recorded with a timeline, ready to report

  • GDPR and ISO 27001

    Manual

    Two projects side by side

    With Tidal

    One set of measures, evidence once

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

See all success stories

Integrate with your existing tools

GDPR compliance software and accountability

The GDPR asks for more than compliance: you have to be able to demonstrate it. That means a current record of processing, DPIAs where needed, processing agreements, procedures for requests and breaches, and evidence that your security works.

In documents and spreadsheets that goes stale quickly. A new supplier or a new processing activity does not get added by itself, and when the supervisory authority asks, the search begins.

GDPR compliance software keeps those parts together, with owners and review dates. You know at any moment what is in place and what is missing.

Frequently asked questions

The GDPR has no mark that declares you compliant. You show it with evidence: a current record of processing, DPIAs where they are needed, processing agreements, a working procedure for data subject requests and security measures that demonstrably run. In Tidal that evidence hangs off the matching controls, with an owner and a date.

Report a personal data breach without undue delay and, where feasible, within 72 hours to the supervisory authority, unless it is unlikely to pose a risk to the people involved. If the risk is high, inform the data subjects themselves as well. Record every breach, even when you do not report it. In Tidal you do that in the Issues module.

Only for processing that is likely to result in a high risk, such as large-scale processing of health data, systematic monitoring or profiling with significant effects. Supervisory authorities publish lists of processing for which a DPIA is required. In Tidal you record the DPIA with a template and link it to your risks.

Yes, our platform includes tools for tracking and managing data subject requests, maintaining response timeframes, and documenting your processes. This helps demonstrate compliance with GDPR requirements while building evidence for BC5701 certification.