NIS2 compliance you can demonstrate

NIS2 applies to organisations in critical and important sectors across the EU. Tidal Control helps you work out whether it applies to you, sets up the measures the duty of care asks for and records evidence and incidents, so you can show it to your board and your supervisor.

  • Duty of care from Article 21
  • Reporting process within 24 hours
  • Reuse your ISO 27001 work
  • Built in the EU
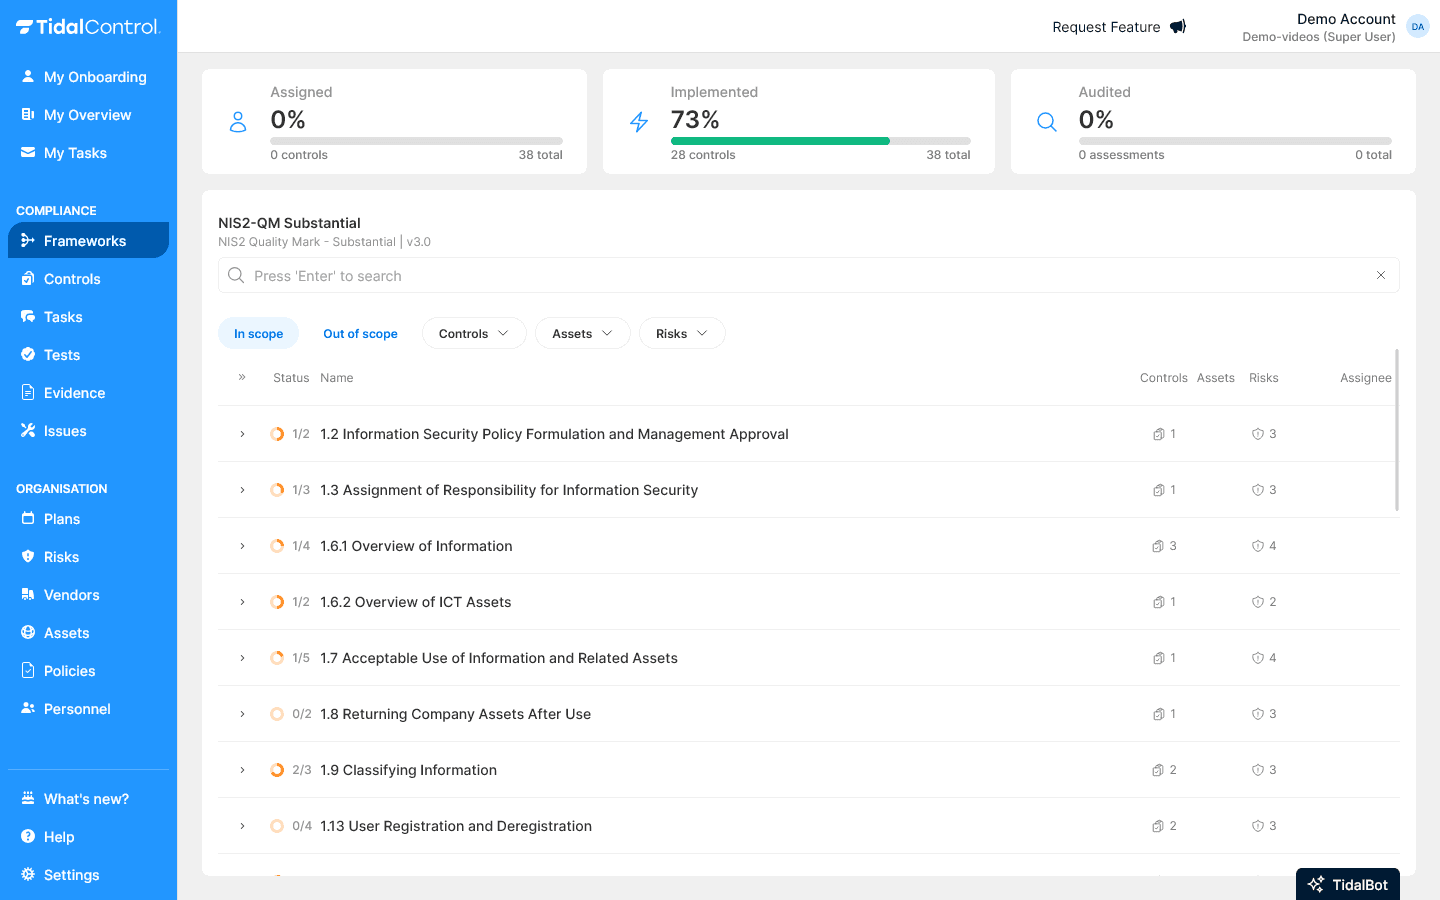
The NIS2 overview in Tidal Control with the status of measures and evidence

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From scope to demonstrable compliance

NIS2 has no certificate. You have to be able to show that your measures are appropriate and that you keep them up to date. Tidal shows what is expected of your team at each step.

  1. Step 1

    Does it apply?

    Sector and size decide whether you are an essential or important entity.

  2. Step 2

    Registration

    Register with your country's national authority.

  3. Step 3

    Risk analysis

    Network and information systems, threats and suppliers mapped.

  4. Step 4

    Measures

    The duty of care filled in with policies, controls and evidence.

  5. Step 5

    Reporting process

    Ready to report a significant incident within 24 hours.

  6. After that

    Supervision and review

    Measures reviewed every year, the board informed, and a sparring partner for new threats.

How Tidal helps with the duty of care

Article 21 of NIS2 lists ten subjects that need appropriate measures. Tidal groups them into six and sets them up for you, with an owner, policy and evidence for each measure.

subjects from Article 21
10subjects from Article 21
NIS2 Keurmerk clauses mapped to ISO 27001
67NIS2 Keurmerk clauses mapped to ISO 27001

Duty of care, Article 21(2)

  • a, f

    Risk analysis and policy

    A risk analysis that backs up your policy, and checks that your measures work.

  • b, c

    Incidents and continuity

    Handling incidents, backups, recovery and crisis management, tested and recorded.

  • d

    Supply chain

    For each supplier the risk, the agreements and a reassessment.

  • e

    Acquisition and development

    Security for new systems, including vulnerability handling.

  • g, i

    People and access

    Training and cyber hygiene, who has access to which systems, and your assets.

  • h, j

    Encryption and MFA

    Encryption of data, multi-factor authentication and secured communication.

NIS2 in brief

NIS2 is the European directive on cybersecurity for organisations in critical and important sectors. Each member state implements it in its own law; in the Netherlands that is the Cyberbeveiligingswet (Cbw), in force since 15 August 2026. The law sets three duties: registration, a duty of care with appropriate measures, and a duty to report significant incidents. The board is ultimately responsible.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • Demonstrable compliance for your supervisor
  • A board that knows what it signs off
  • Answers for customers who fall under NIS2 themselves
  • Less chance of incidents and outages
  • Work that also counts towards ISO 27001

How you work on NIS2 in Tidal

From risk analysis to incident reporting: every NIS2 duty in one place.

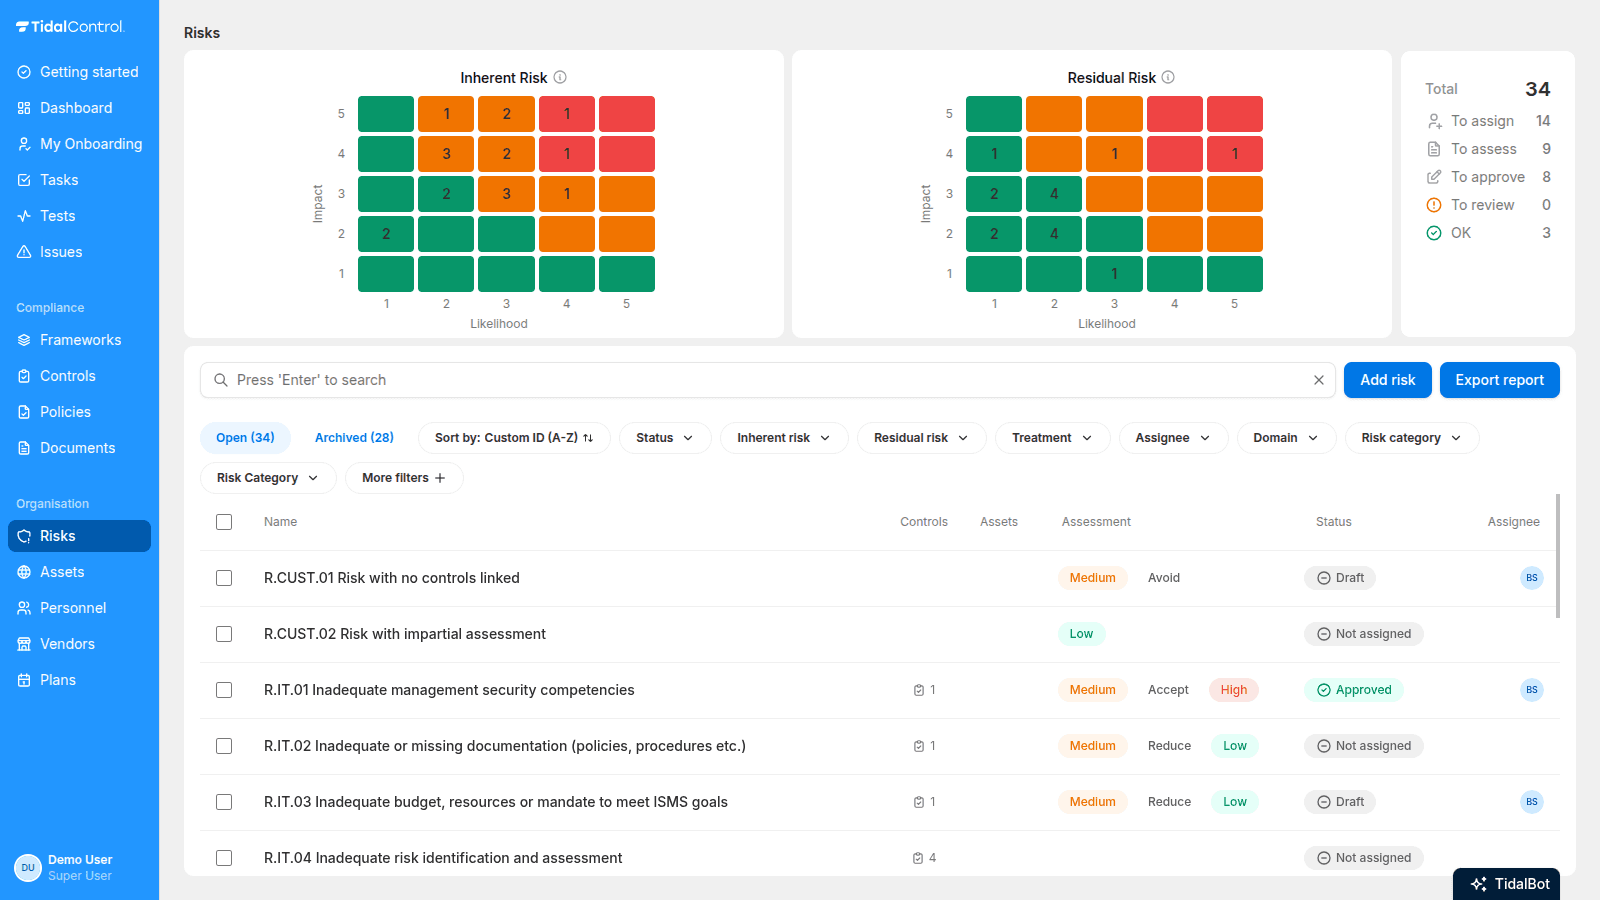
Risk assessment

Risk assessments that work

Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

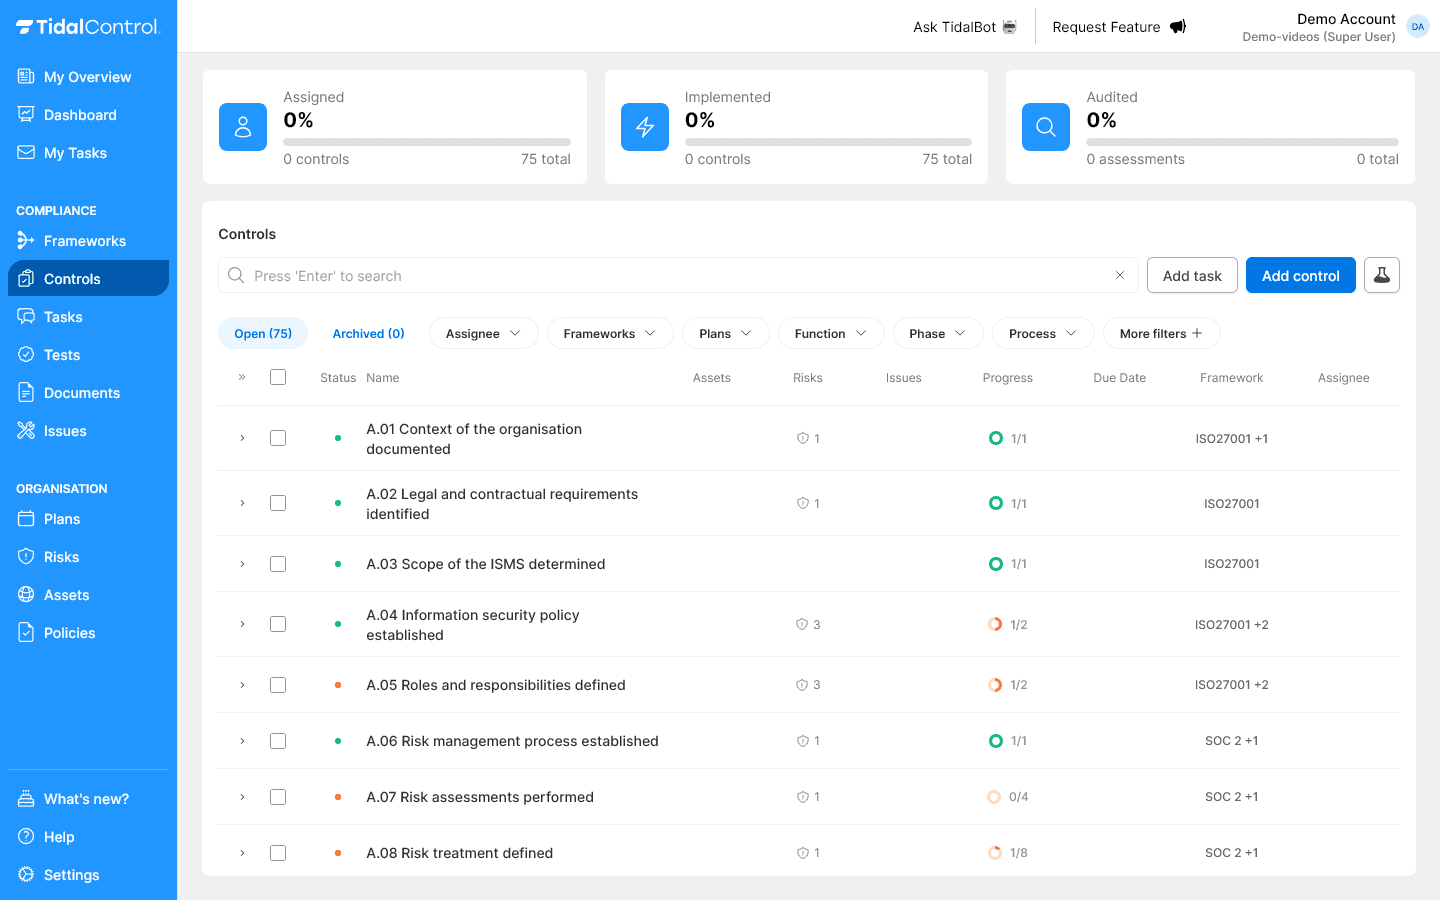
Risk assessment in Tidal ControlRisk assessments that work
Controls management

Control management that works your way

Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

Controls management in Tidal ControlControl management that works your way

Issues management

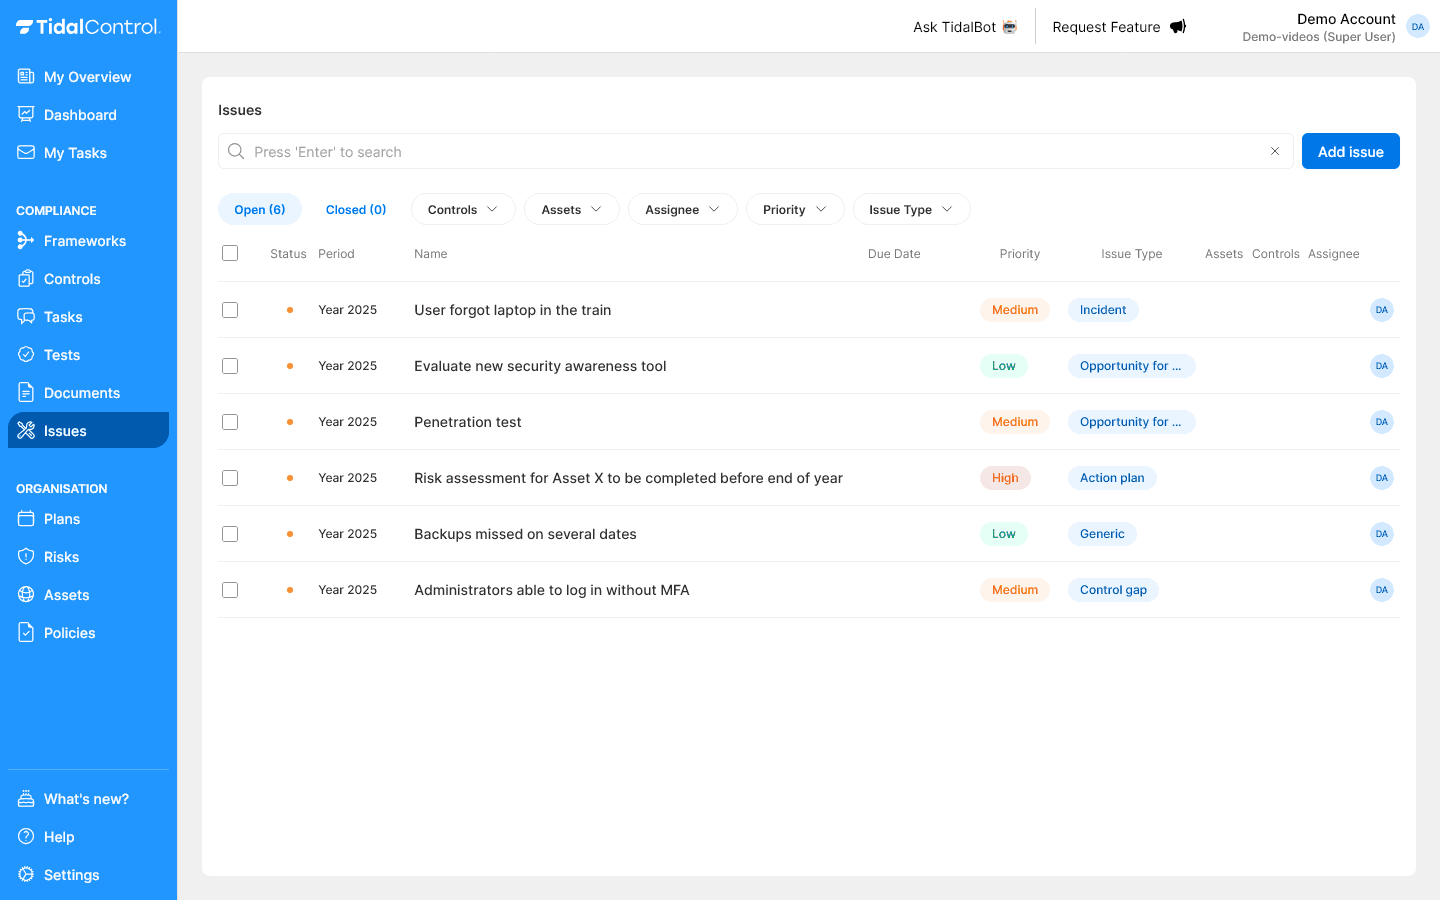
Incidents recorded, ready to report

Record incidents with a timeline, impact and handling. You then have the information to hand when a significant incident has to be reported to the CSIRT and your supervisor within 24 hours.

Issues management in Tidal ControlIncidents recorded, ready to report

Vendor management

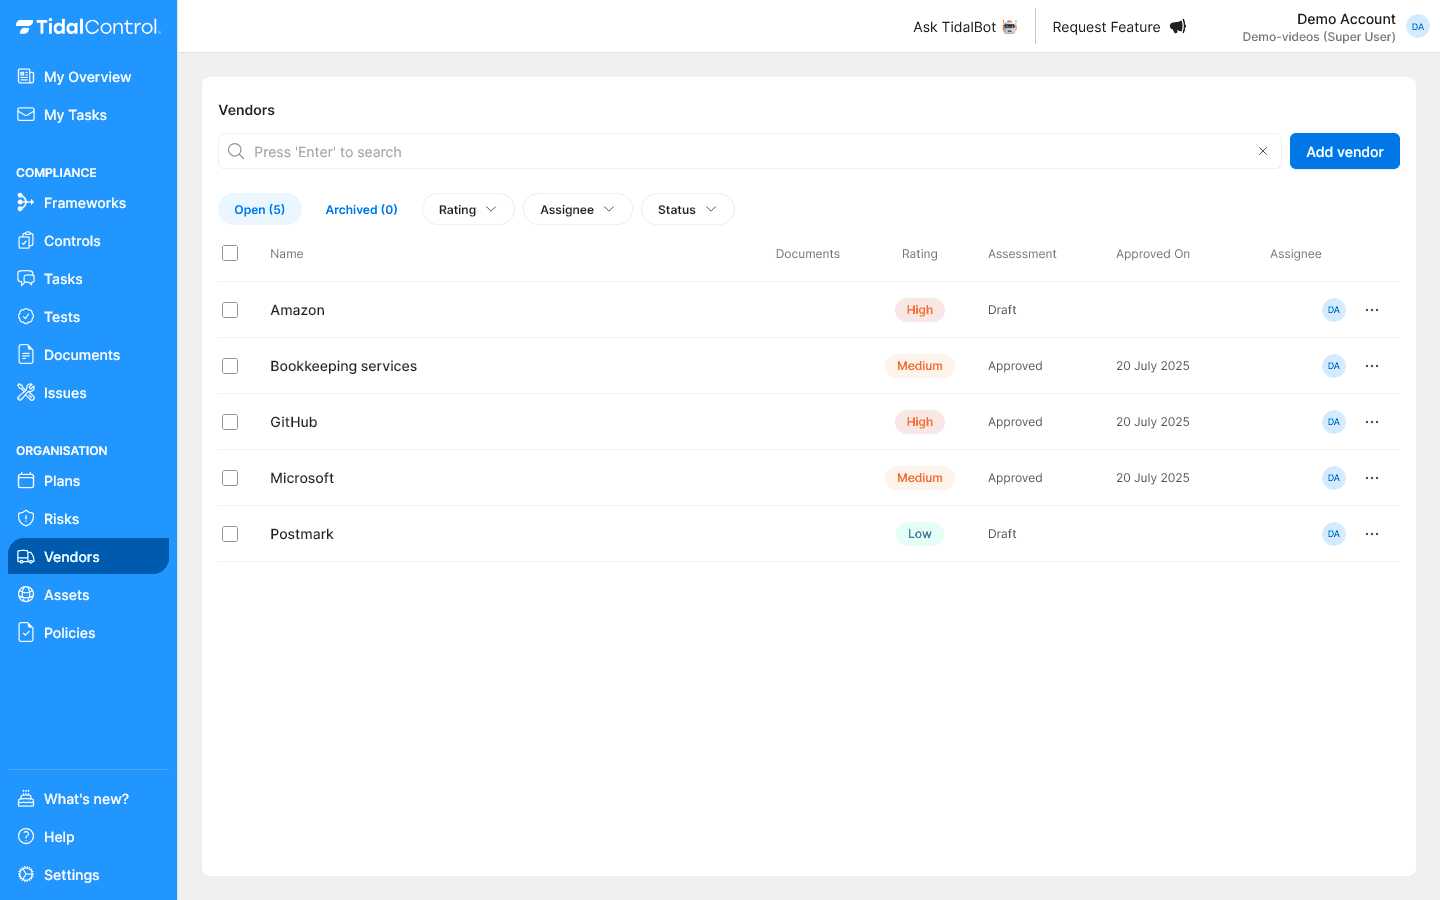
Your supply chain in view

NIS2 makes you responsible for the security of your suppliers. Assess the risk of each supplier, record the agreements and schedule a reassessment.

Vendor management in Tidal ControlYour supply chain in view

Policy center

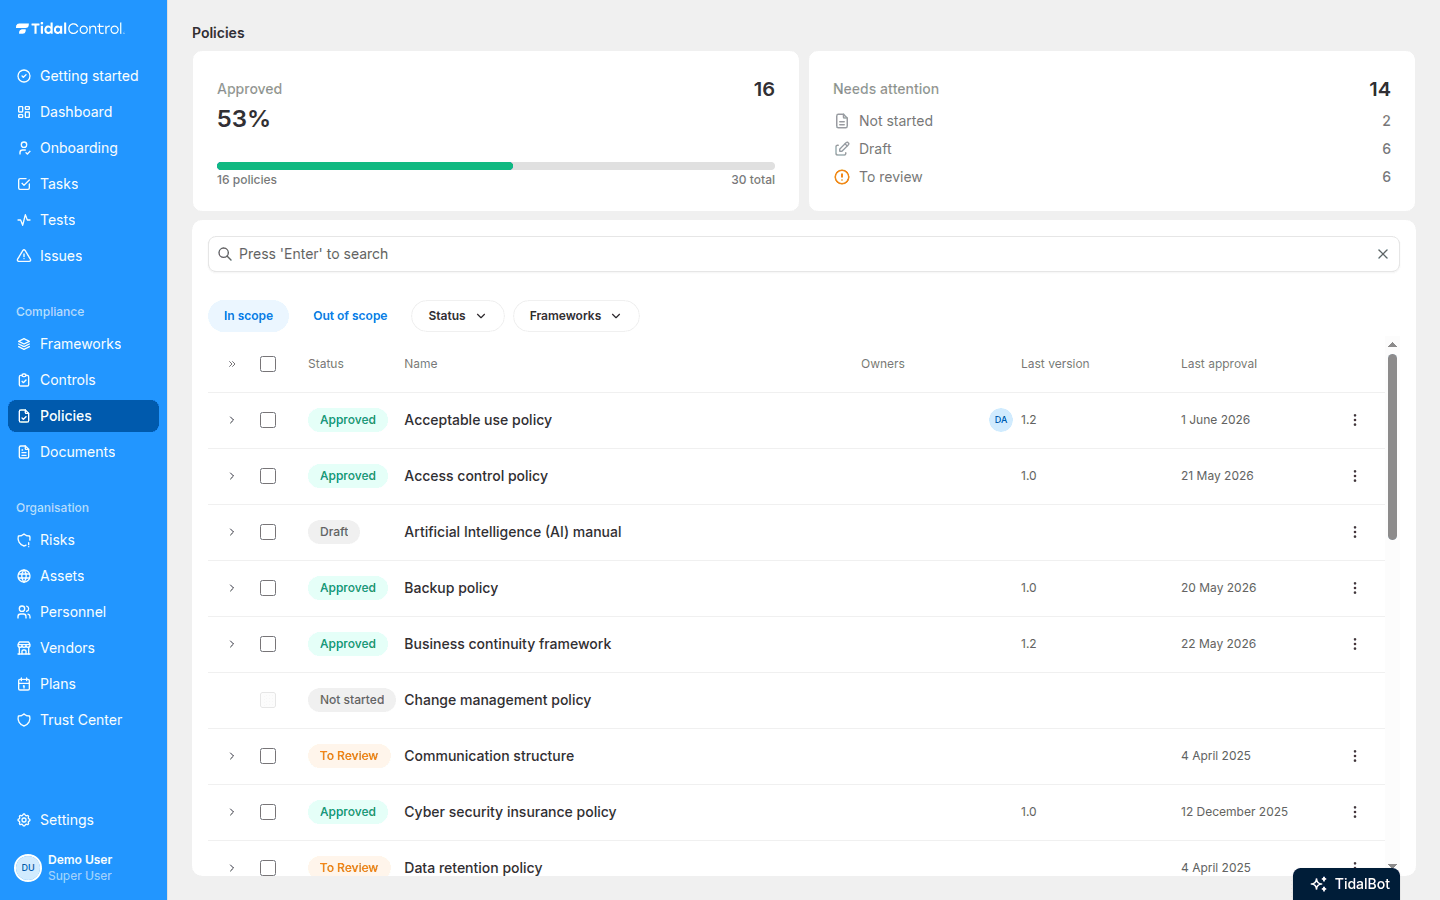
Policies without the hassle

Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

Personnel & onboarding

Employee compliance without the spreadsheet

The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

Integrations

Automation makes life more fun!

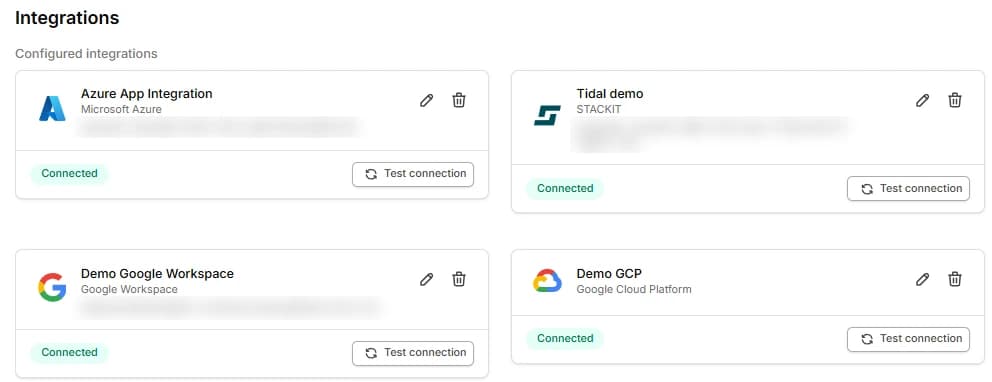
Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • Duty of care measures

    Manual

    Your own reading in a spreadsheet

    With Tidal

    Pre-mapped with owners

  • Collecting evidence

    Manual

    Only when the supervisor asks

    With Tidal

    Automatically from your tools

  • Incident reporting

    Manual

    Looking for information when it goes wrong

    With Tidal

    Incidents recorded with a timeline

  • Suppliers

    Manual

    Separate questionnaires by email

    With Tidal

    Risk per supplier with reassessment

  • Overlap with ISO 27001

    Manual

    Two projects side by side

    With Tidal

    One set of measures, evidence once

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

See all success stories

Integrate with your existing tools

NIS2 compliance software

The NIS2 duty of care asks for appropriate and proportionate measures on ten subjects, from risk analysis to MFA. What is appropriate is your call, based on your risks. That is what makes it hard: there is no list to tick off.

NIS2 compliance software gives those choices structure. You link risks to measures, record an owner and evidence for each measure and see which subjects are still open. If you choose a reference framework such as the NIS2 Keurmerk or CyberFundamentals, the requirements are already set up.

That way you can show at any moment why your measures are appropriate, to the board, to customers and to the supervisor.

Frequently asked questions

Through the Cyberbeveiligingswet (Cbw), the Dutch law that implements NIS2, in force since 15 August 2026 together with the Cyberbeveiligingsbesluit. It sets the duty of care, the board obligations, incident reporting and registration for essential and important entities in the Netherlands. Our Cbw page sets out each obligation and how Tidal covers it.

Report a significant incident as soon as possible and within 24 hours to the CSIRT and your supervisor, as an early warning. A notification with a first assessment follows within 72 hours, and a final report within a month. In Tidal you record incidents and their handling in the Issues module, so you can back up those reports.

No. NIS2 does not prescribe a certificate or a mandatory NIS2 audit. You do have to be able to show that your measures are appropriate and proportionate. A voluntary mark such as the NIS2 Keurmerk, or an ISO 27001 certificate, helps you provide that evidence, but does not replace the duties in the law.

The board has to approve the duty of care measures, oversee their implementation and take a training course itself. Board members can be held accountable if the organisation does not meet its duties. In Tidal you see the status of each subject, so you can inform the board with evidence.

Tidal supports the NIS2 CyberFundamentals framework and the NIS2 Quality Mark. Both offer 3 implementation levels, in line with the NIS2 qualifications. Our platform helps you implement and maintain compliance with either framework, providing specific guidance and controls for each.

We can help you determine whether your organisation (and/or your customers) qualifies as an essential or important entity under NIS2. We guide you through the sector-specific requirements and size thresholds to understand your obligations.

In the vendor module you assess the risk of each supplier, record agreements and evidence and schedule a reassessment. That way you can show how you monitor security in your supply chain, as Article 21 asks.

Subscriptions start at €249/month for Essential, €499/month for Professional and €1,699/month for Scale (billed annually), all with unlimited user accounts. Which plan fits depends on the NIS2 level you need and how many frameworks you run alongside it: NIS2 QM10 is an Essential framework, NIS2 QM30 a Professional one. Full details are on our pricing page.

Tidal is built and hosted in the EU, so your compliance data stays there. NIS2 also sits in the same platform as 30+ other frameworks, so work for ISO 27001 or GDPR reuses the same controls and evidence instead of running as a separate project.

Yes. Smaller organisations can start on Essential with NIS2 QM10, the lightest of the three implementation levels, and move up as their obligations grow. Adding a level or a framework does not mean switching platforms or re-entering evidence.