DORA compliance you can demonstrate to your supervisor

DORA has applied to financial entities in the EU since 17 January 2025. Tidal Control sets up the five pillars, keeps your Register of Information and ICT third parties current and records incidents and tests, so you can show it to your supervisor.

  • All five DORA pillars
  • Register of Information
  • NOREA DORA framework
  • Built in the EU
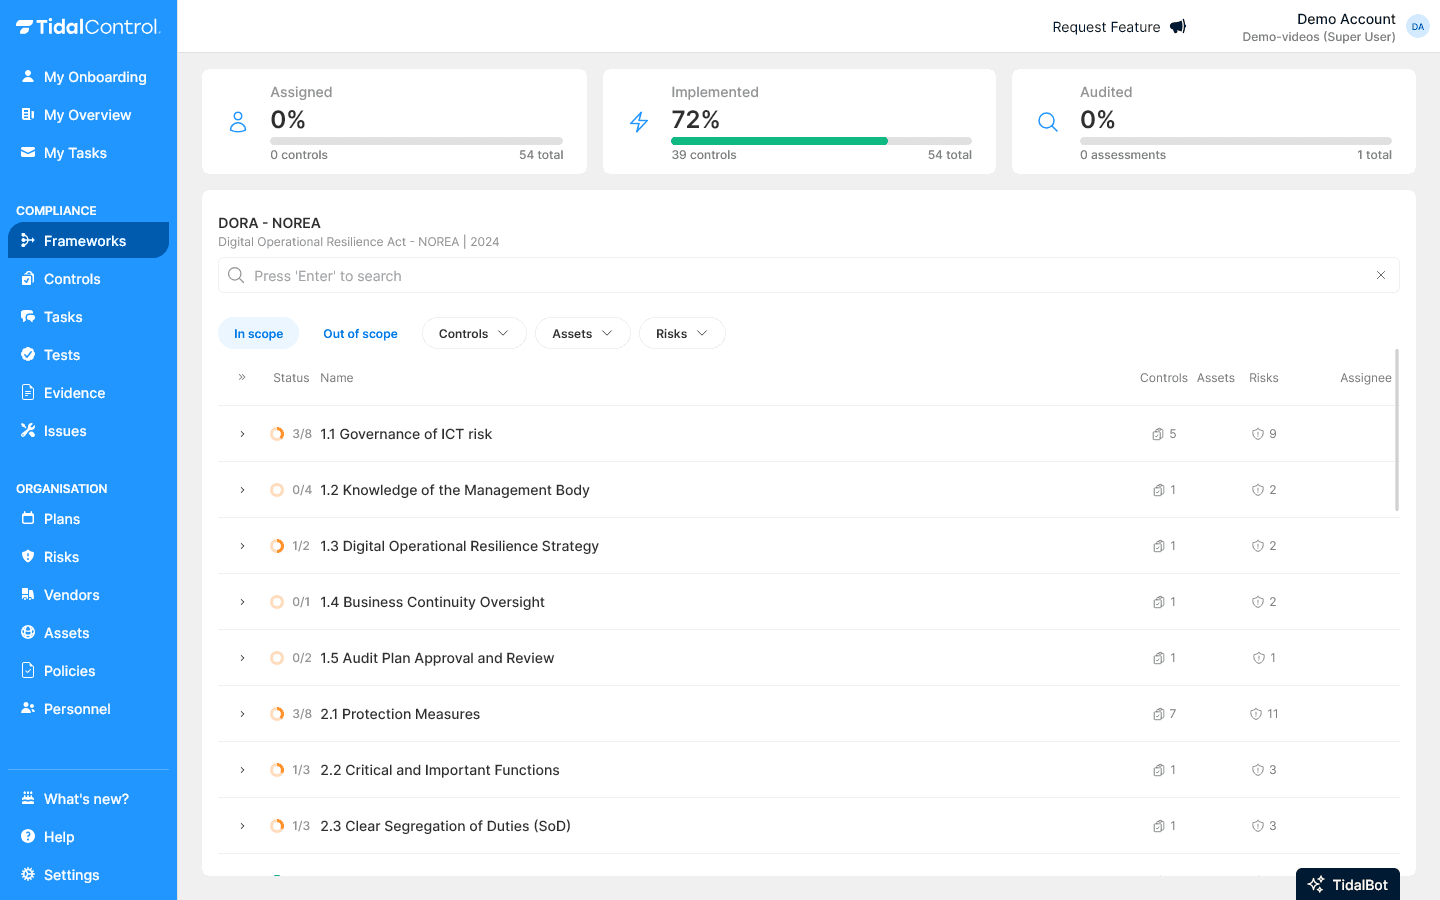
The DORA overview in Tidal Control with the status of measures and evidence

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From gap analysis to demonstrable compliance

DORA has no certificate. Your supervisor wants to see that you manage ICT risk and keep it up. Tidal shows what is expected of your team at each step.

  1. Step 1

    Scope and proportionality

    Which requirements apply to your entity, by size and risk.

  2. Step 2

    Gap analysis

    For each pillar, what is in place and what is missing.

  3. Step 3

    ICT risk framework

    Policies, measures and owners for ICT risk management.

  4. Step 4

    Incidents and testing

    Ready to classify and report incidents, and a testing programme.

  5. Step 5

    Third parties and register

    ICT providers assessed and the Register of Information filled in.

  6. After that

    Supervision and review

    Reviewed every year, the board informed, and a sparring partner for supervisor questions.

How Tidal helps with the DORA pillars

DORA rests on five pillars, with the Register of Information as a fixed report. Tidal sets them up for you, with an owner, policy and evidence for each measure. If you want a Dutch reference framework, the NOREA DORA framework is included.

pillars
5pillars
controls in the NOREA framework
95controls in the NOREA framework

DORA in six blocks

  • Pillar 1

    ICT risk management

    A framework for ICT risk with policies, measures and an accountable board.

  • Pillar 2

    Incident management and reporting

    Classifying and handling incidents, and reporting major ones on time.

  • Pillar 3

    Resilience testing

    A testing programme, and TLPT for the largest entities.

  • Pillar 4

    ICT third parties

    Risks of ICT providers assessed and set out in contracts.

  • Pillar 5

    Information sharing

    Voluntarily sharing threat intelligence with other entities.

  • Register

    Register of Information

    All arrangements with ICT providers in the fixed reporting format.

DORA in brief

The Digital Operational Resilience Act (DORA) is an EU regulation on the digital resilience of financial entities, from banks and insurers to payment institutions and pension funds. It has applied since 17 January 2025, directly in every member state. National supervisors oversee it; in the Netherlands that is DNB and the AFM. For financial entities DORA takes precedence over NIS2.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • Demonstrable compliance for your supervisor
  • A board that knows what it signs off
  • Control over the ICT providers you depend on
  • Less chance of outages and incidents
  • Work that also counts towards ISO 27001

How you work on DORA in Tidal

From ICT risks to the Register of Information: every DORA pillar in one place.

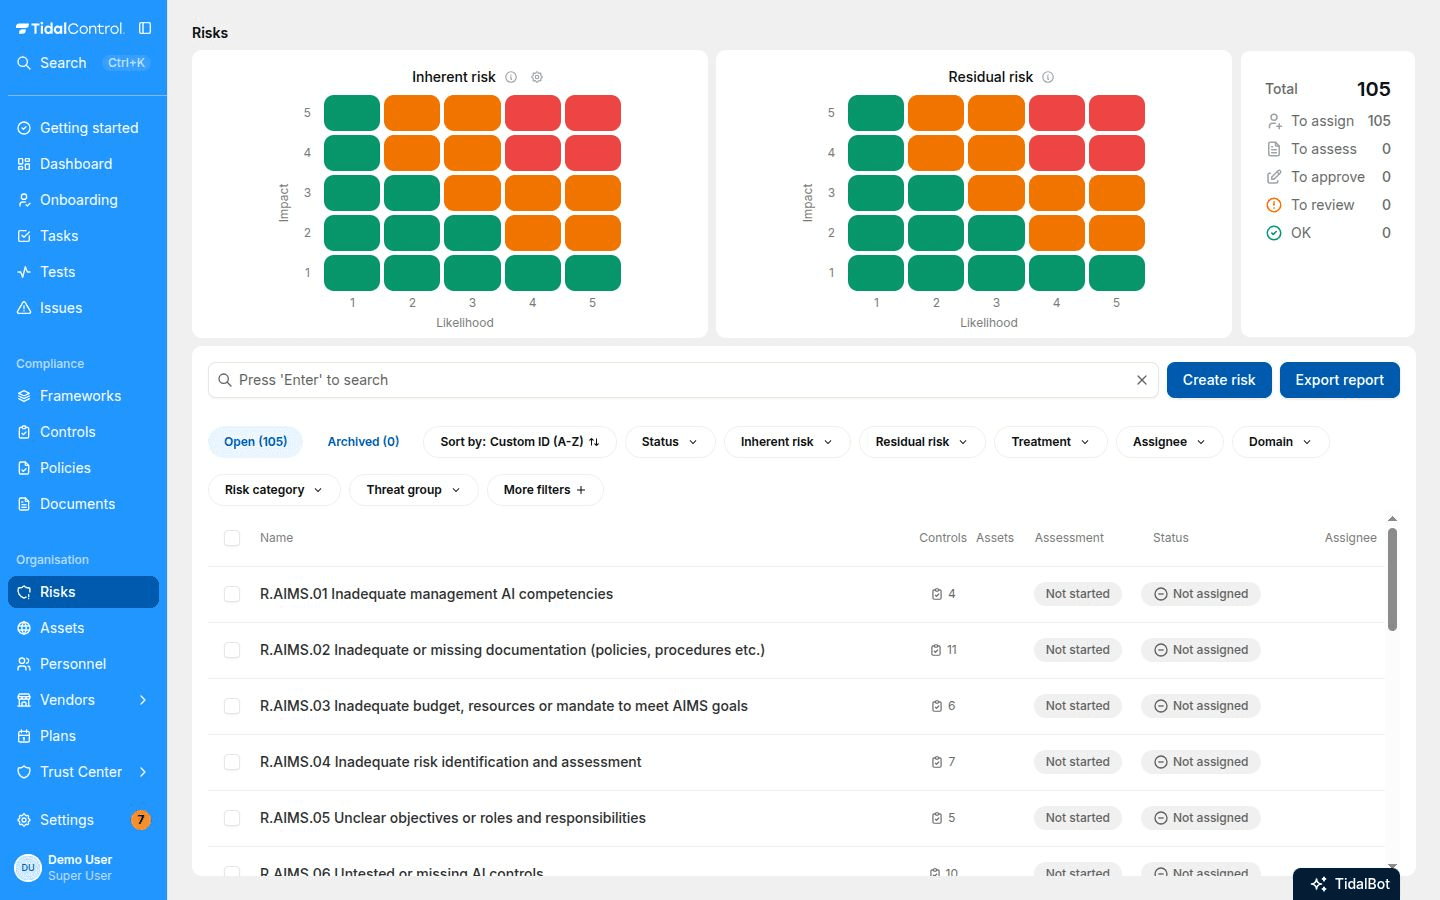
Risk assessment

Risk assessments that work

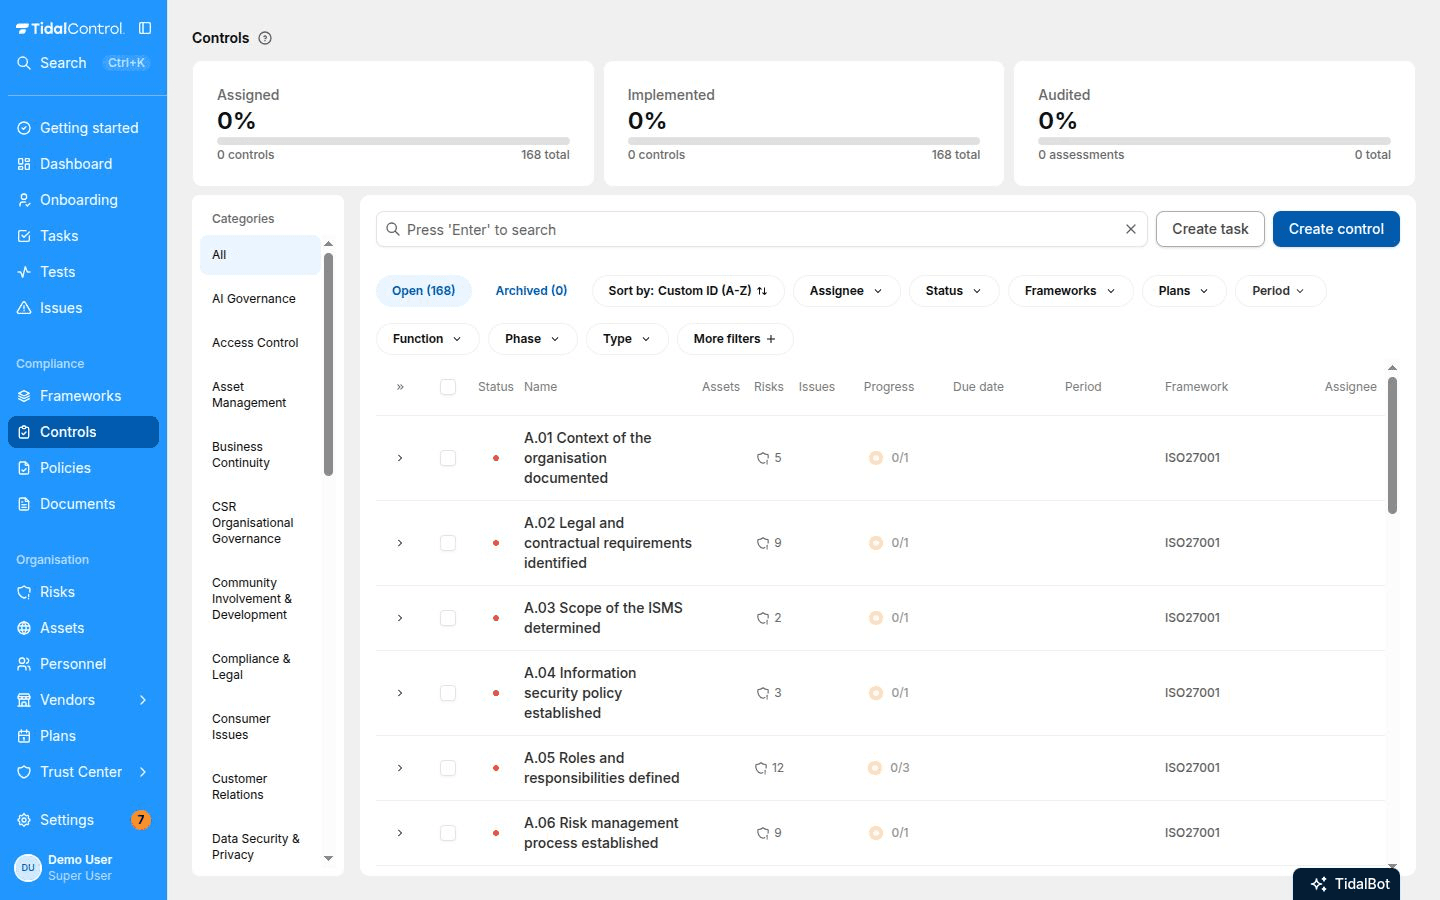
Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

Risk assessment in Tidal ControlRisk assessments that work
Controls management

Control management that works your way

Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

Controls management in Tidal ControlControl management that works your way

Vendor management

ICT providers and your register in view

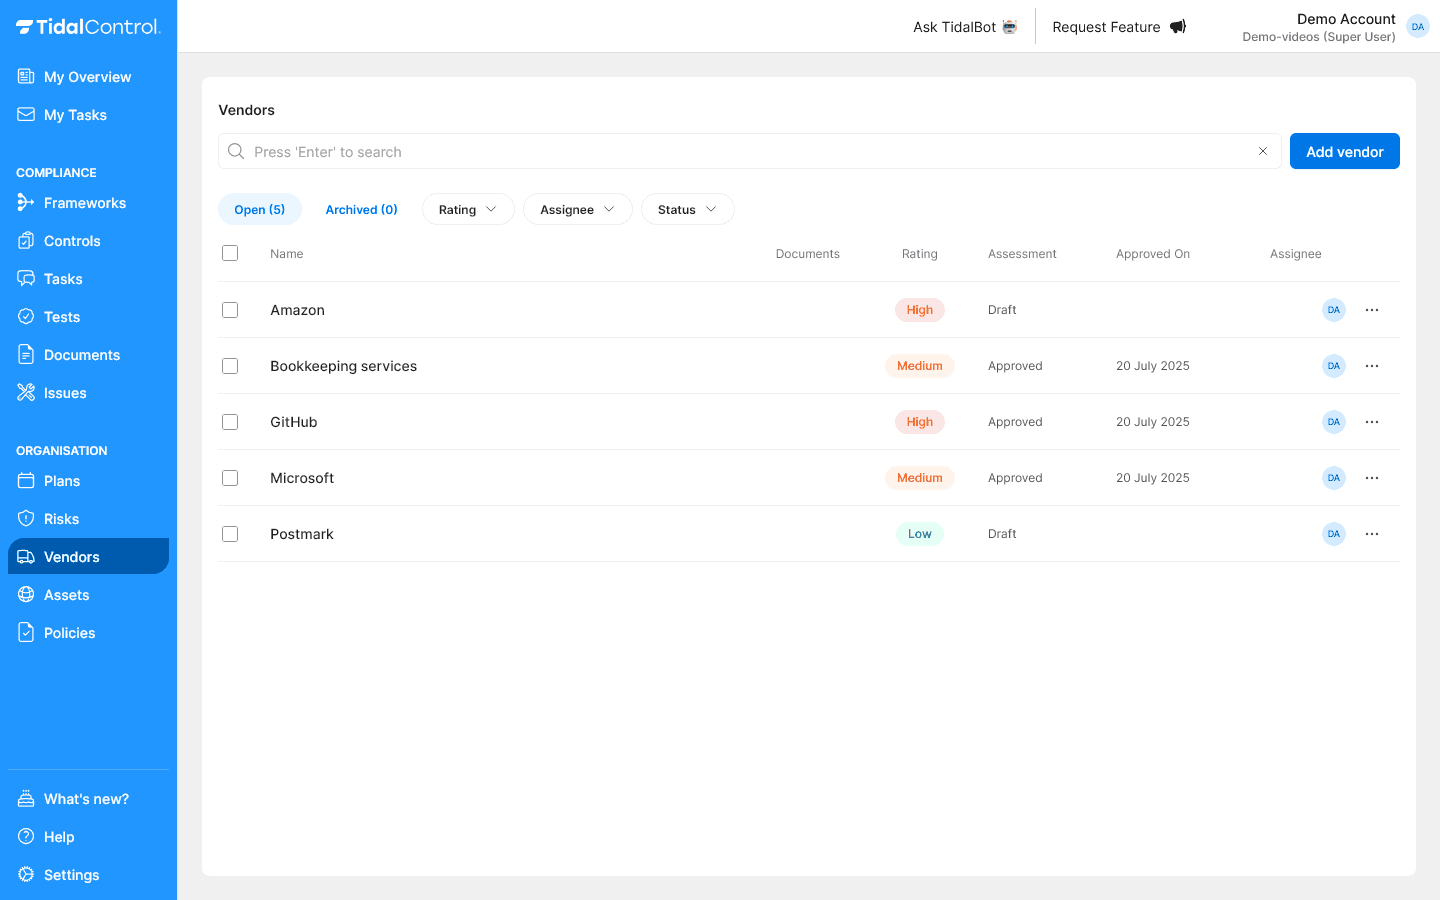
Record for each ICT provider the arrangements, the risk and the critical functions. That data also forms your Register of Information.

Vendor management in Tidal ControlICT providers and your register in view

Issues management

ICT incidents recorded, ready to report

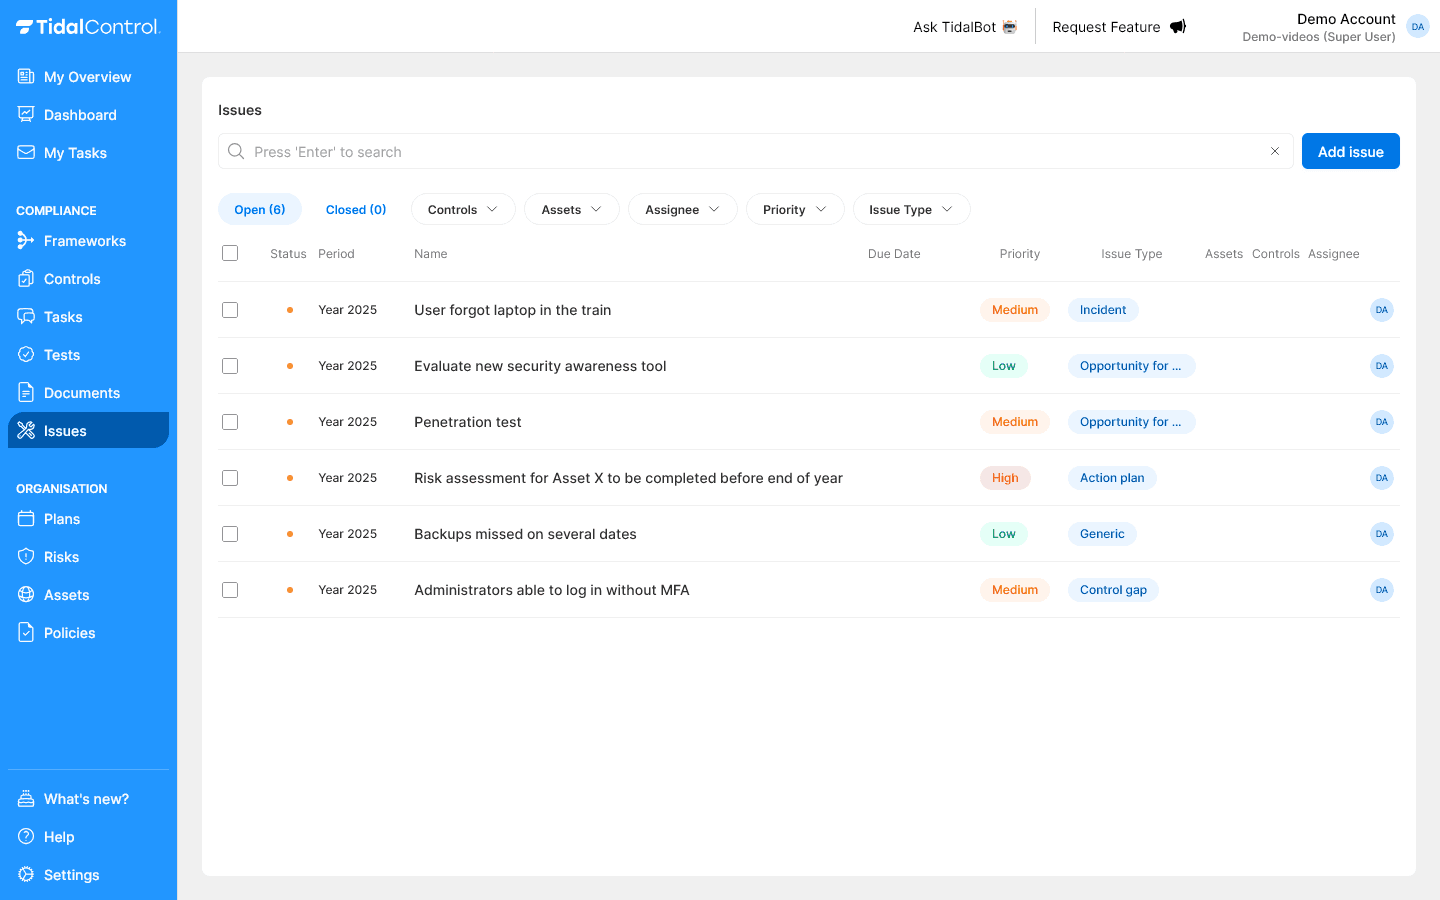
Record incidents with timeline, impact and classification, so you can report a major ICT incident on time and with evidence.

Issues management in Tidal ControlICT incidents recorded, ready to report

Policy center

Policies without the hassle

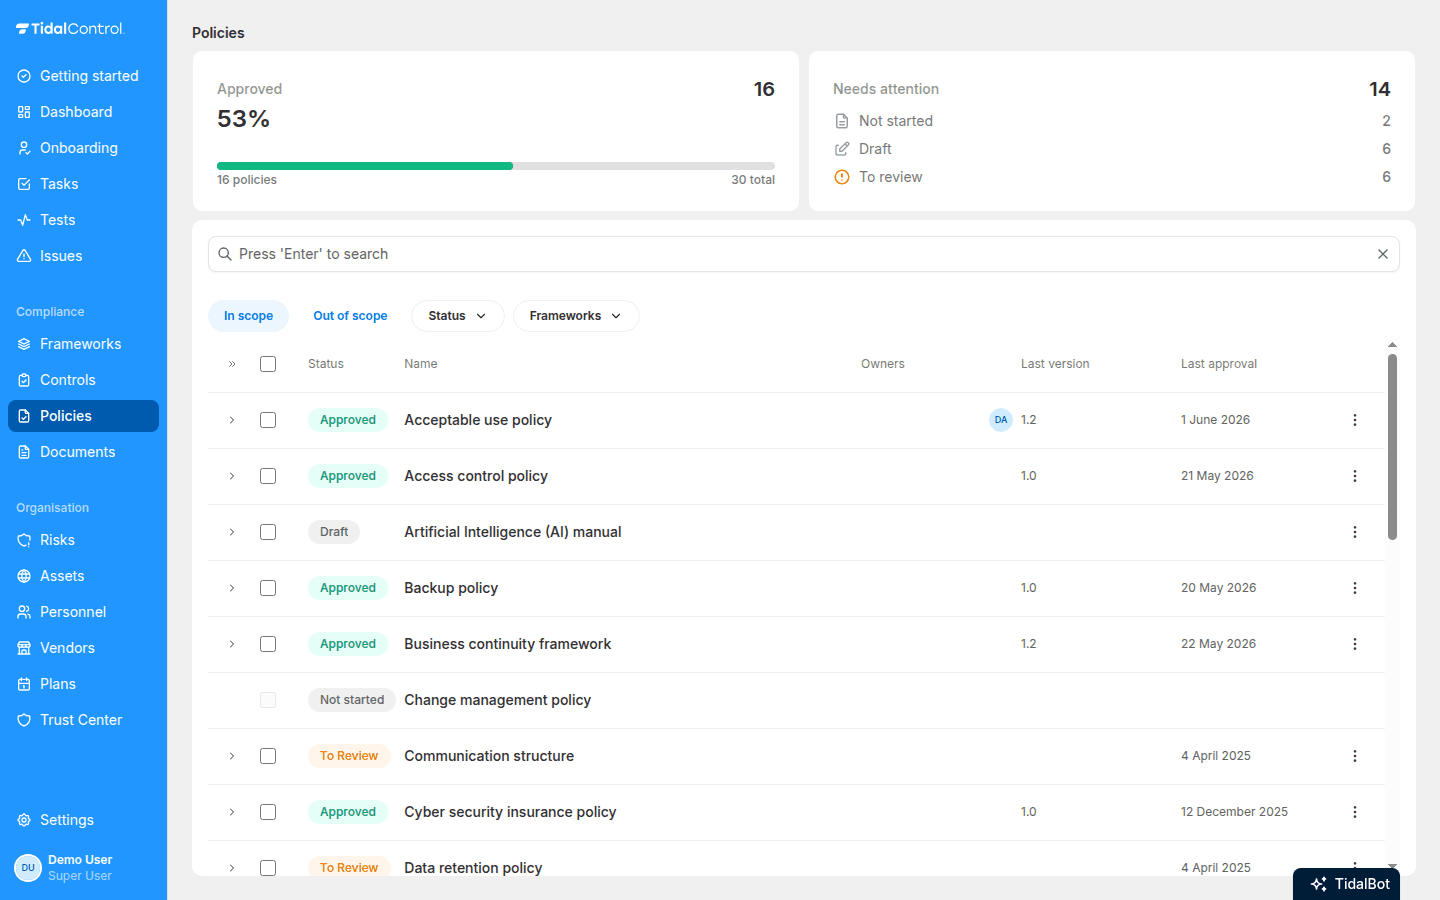
Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

Personnel & onboarding

Employee compliance without the spreadsheet

The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

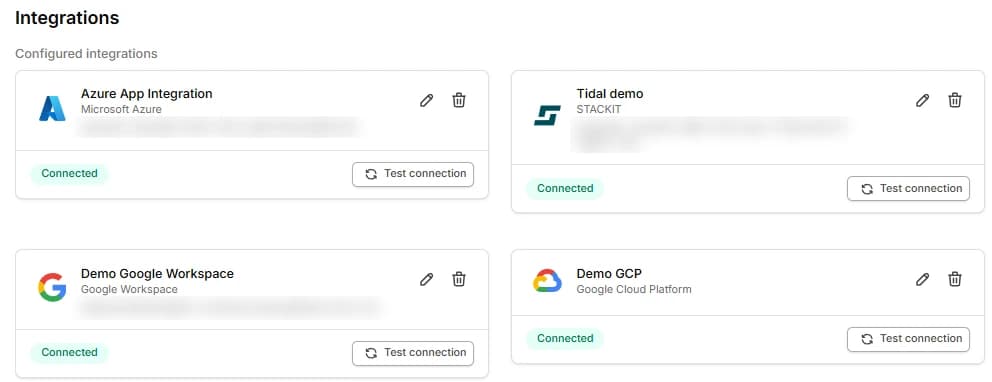
Integrations

Automation makes life more fun!

Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • ICT risk framework

    Manual

    Policies in separate documents

    With Tidal

    Risks and measures with owners

  • Register of Information

    Manual

    A spreadsheet rebuilt every year

    With Tidal

    Filled from your supplier management

  • Incident reporting

    Manual

    Looking for information when it goes wrong

    With Tidal

    Incidents recorded with timeline and classification

  • Testing

    Manual

    Reports spread across folders

    With Tidal

    Tests, findings and remediation in one place

  • DORA and ISO 27001

    Manual

    Two projects side by side

    With Tidal

    One set of measures, evidence once

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

See all success stories

Integrate with your existing tools

DORA compliance software and supervision

DORA asks for an ICT risk framework that works, not just a policy document. The board is ultimately responsible, and the supervisor can ask at any time how you manage risks, incidents and suppliers.

DORA compliance software links ICT risks to measures, owners and evidence, records incidents and tests and keeps your ICT providers current. If you choose the NOREA DORA framework as a reference, its 95 controls are already set up.

You can then show at any moment where you stand, to the board and to your supervisor.

Frequently asked questions

Our platform provides support for DORA's five pillars: ICT risk management, incident reporting, digital operational resilience testing, third-party risk management, and information sharing. We offer pre-built controls, risk assessment frameworks, and automated monitoring tools specifically aligned with DORA requirements.

Yes. Next to the regulation itself, Tidal includes the DORA control framework from NOREA, the Dutch professional association of IT auditors. It translates DORA into 95 controls under 28 control objectives, grouped into eight domains: governance and risk management, security management, operational management, continuity management, software and systems development, incident management, third-party risk management and resilience testing. It is useful when an IT auditor assesses your DORA programme against those controls.
Yes. Assets and vendors include dedicated fields for the DORA Register of Information, so you can capture your ICT assets and third-party service providers directly in Tidal Control. A DORA settings dialog on the Framework page lets you configure register-level fields such as your entity name and LEI code, and the register can be exported in the format supervisors expect.

Report a major ICT incident to your supervisor in stages: an initial notification within four hours of classifying it as major and no later than 24 hours after detecting it, an intermediate report within 72 hours and a final report within a month. In Tidal you record incidents with timeline and classification, so you can back up those reports.

Yes, we can help you manage and document your TLPT programme as required by DORA. This includes planning tests with the help of our trusted and certified penetration testing partners, tracking findings, managing remediation, and maintaining evidence of your testing activities.

Our platform includes tools for assessing, monitoring, and documenting your critical ICT third-party relationships. This includes contract management, service level monitoring, and maintaining evidence of ongoing oversight as required by DORA.

Yes, our platform helps you maintain the documentation and evidence needed for supervisory oversight. We help you demonstrate your compliance with DORA requirements through clear reporting, audit trails, and organised evidence collection.