Ready for your SOC 2 audit, Type 1 and Type 2

The audit report US and international customers ask for. Tidal Control sets up your controls on the Trust Service Criteria, collects evidence automatically across the whole observation period and prepares you for the auditor.

  • All five Trust Service Criteria
  • Evidence across the whole period
  • Together with ISO 27001
  • Built in the EU
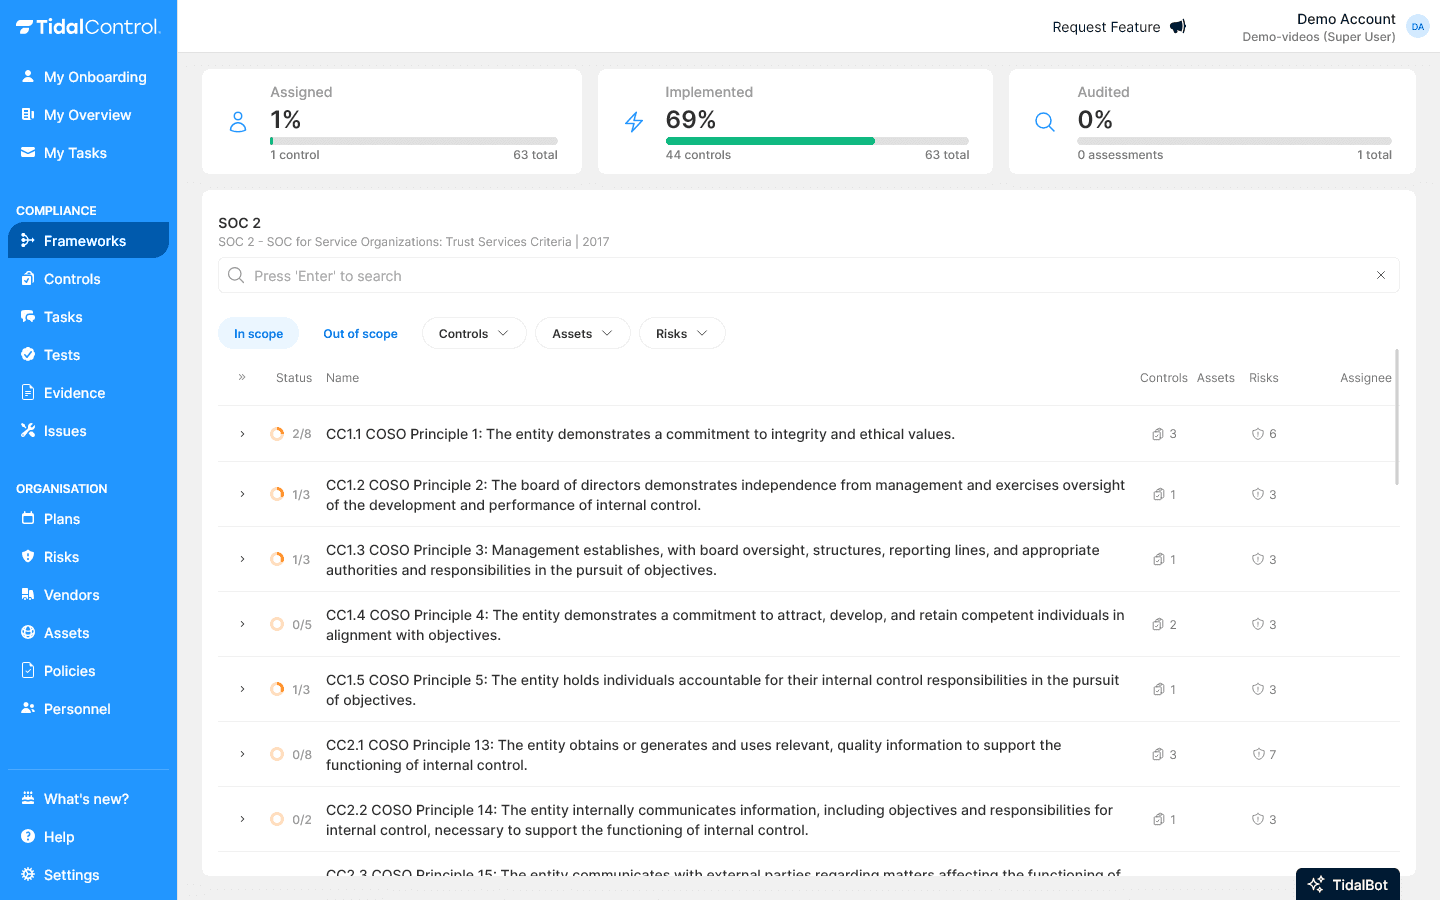
The SOC 2 overview in Tidal Control with the status of controls and evidence

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From scope to SOC 2 report

How long it takes depends on what is already in place and how long your observation period is. Tidal shows what is expected of your team at each phase.

  1. Step 1

    Scope and criteria

    Systems in scope and the Trust Service Criteria beyond security chosen.

  2. Step 2

    Gap analysis

    For each criterion, what is in place and what is missing.

  3. Step 3

    Implementation

    Policies, controls and evidence filled in with templates.

  4. Step 4

    Type 1

    The auditor assesses the design of your controls at one point in time.

  5. Step 5

    Type 2

    The auditor assesses their operation over a period of usually three to twelve months.

  6. After that

    Annual report

    Evidence keeps flowing so the next report connects, and a sparring partner when customers ask new questions.

How Tidal helps with the Trust Service Criteria

A SOC 2 report tests your controls against the AICPA's Trust Service Criteria. Security is always required; you choose the others based on what your customers expect. Tidal sets them up for you, with an owner, policy and evidence for each control.

Trust Service Criteria
5Trust Service Criteria
automated tests
300+automated tests

Trust Service Criteria

  • Required

    Security

    The common criteria: access, change, monitoring and risk.

  • Optional

    Availability

    Capacity, backups and recovery, for services customers run on.

  • Optional

    Processing integrity

    Processing that is complete, accurate and on time.

  • Optional

    Confidentiality

    Confidential customer data protected and deleted on time.

  • Optional

    Privacy

    Personal data collected, used and kept as you promise.

SOC 2 in brief

SOC 2 is an audit report by an independent auditor on how you handle customer data, tested against the AICPA's Trust Service Criteria. It is not a certificate: you get a report that you share with customers. A Type 1 report assesses the design of your controls at one point in time, a Type 2 report also their operation over a period.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • Deals with US and international customers
  • Fewer one-off security questionnaires
  • A report you can share with customers
  • Control over your security all year round
  • Work that also counts towards ISO 27001

How you work on SOC 2 in Tidal

From risk assessment to your trust center: every part of your SOC 2 programme in one place.

Controls management

Control management that works your way

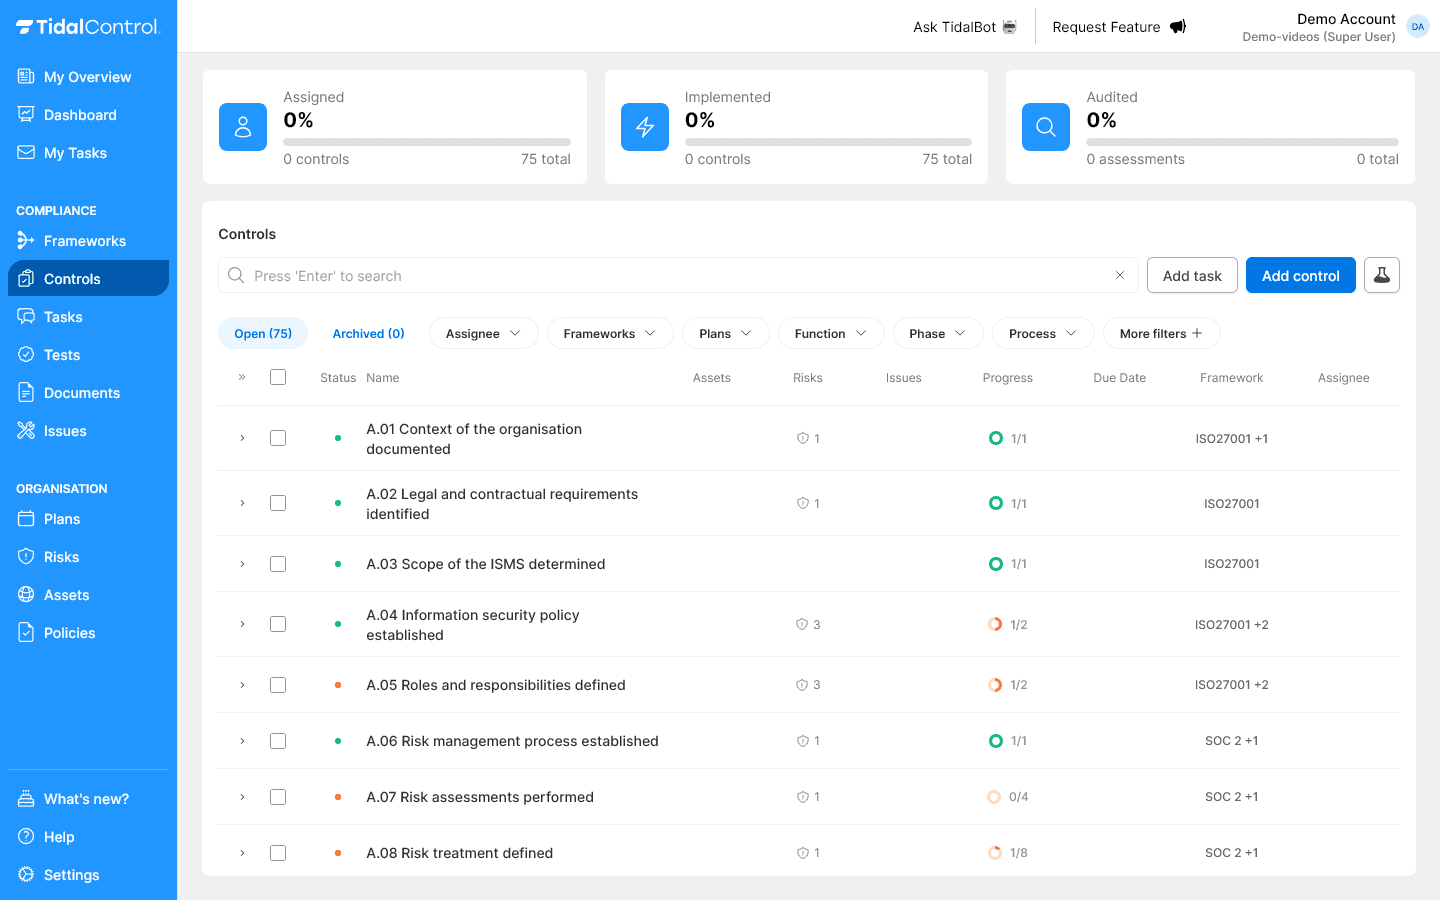
Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

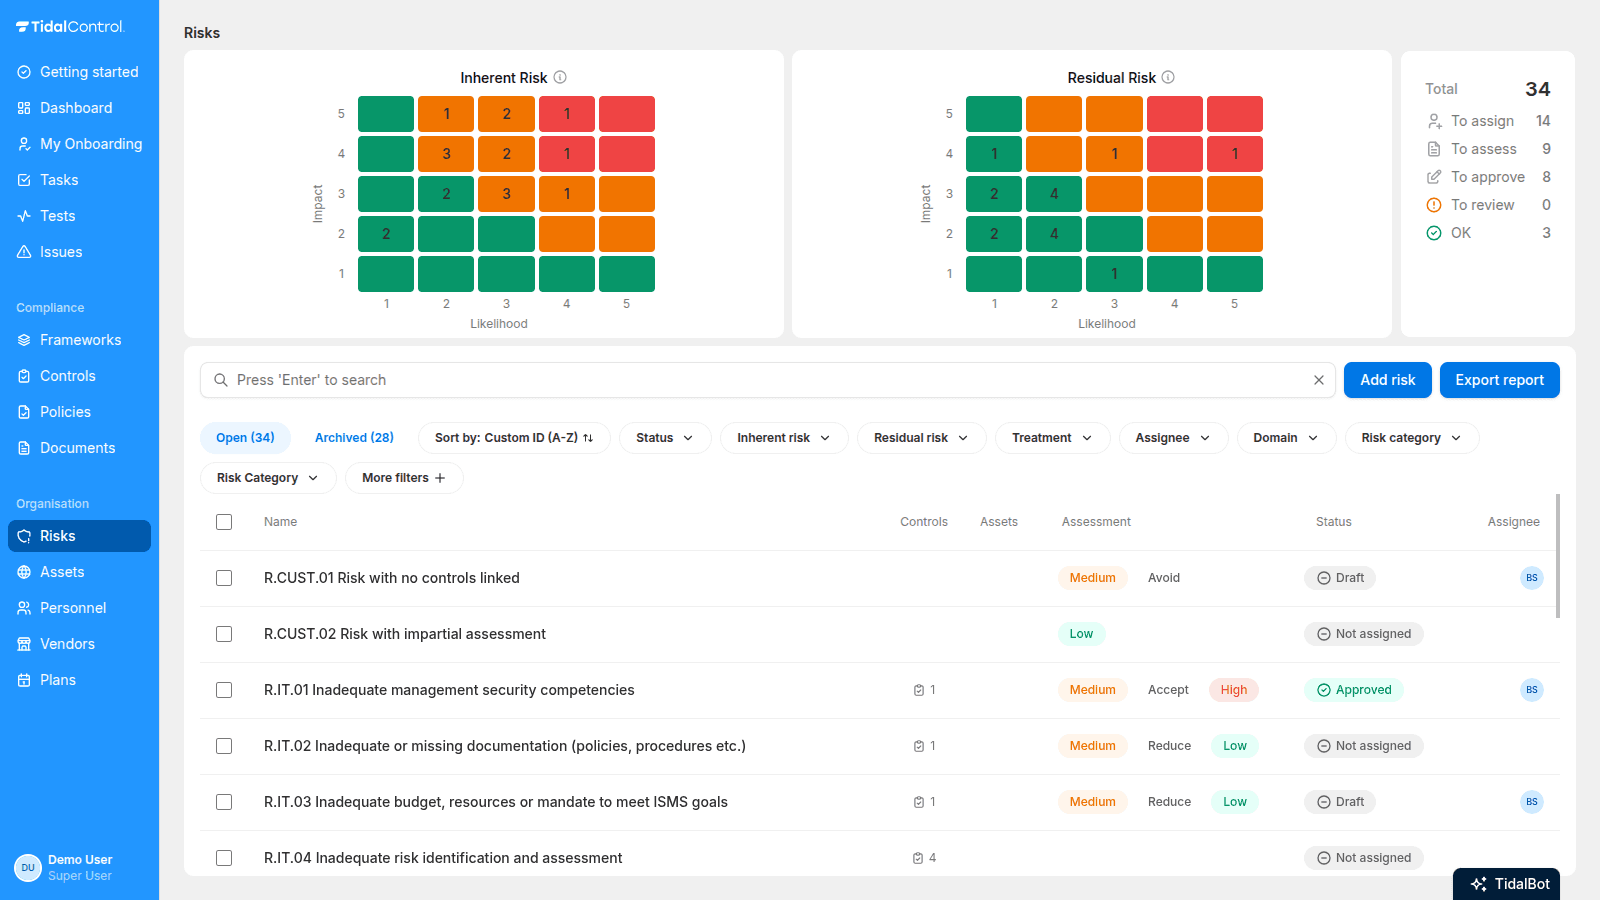
Controls management in Tidal ControlControl management that works your way
Risk assessment

Risk assessments that work

Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

Risk assessment in Tidal ControlRisk assessments that work

Policy center

Policies without the hassle

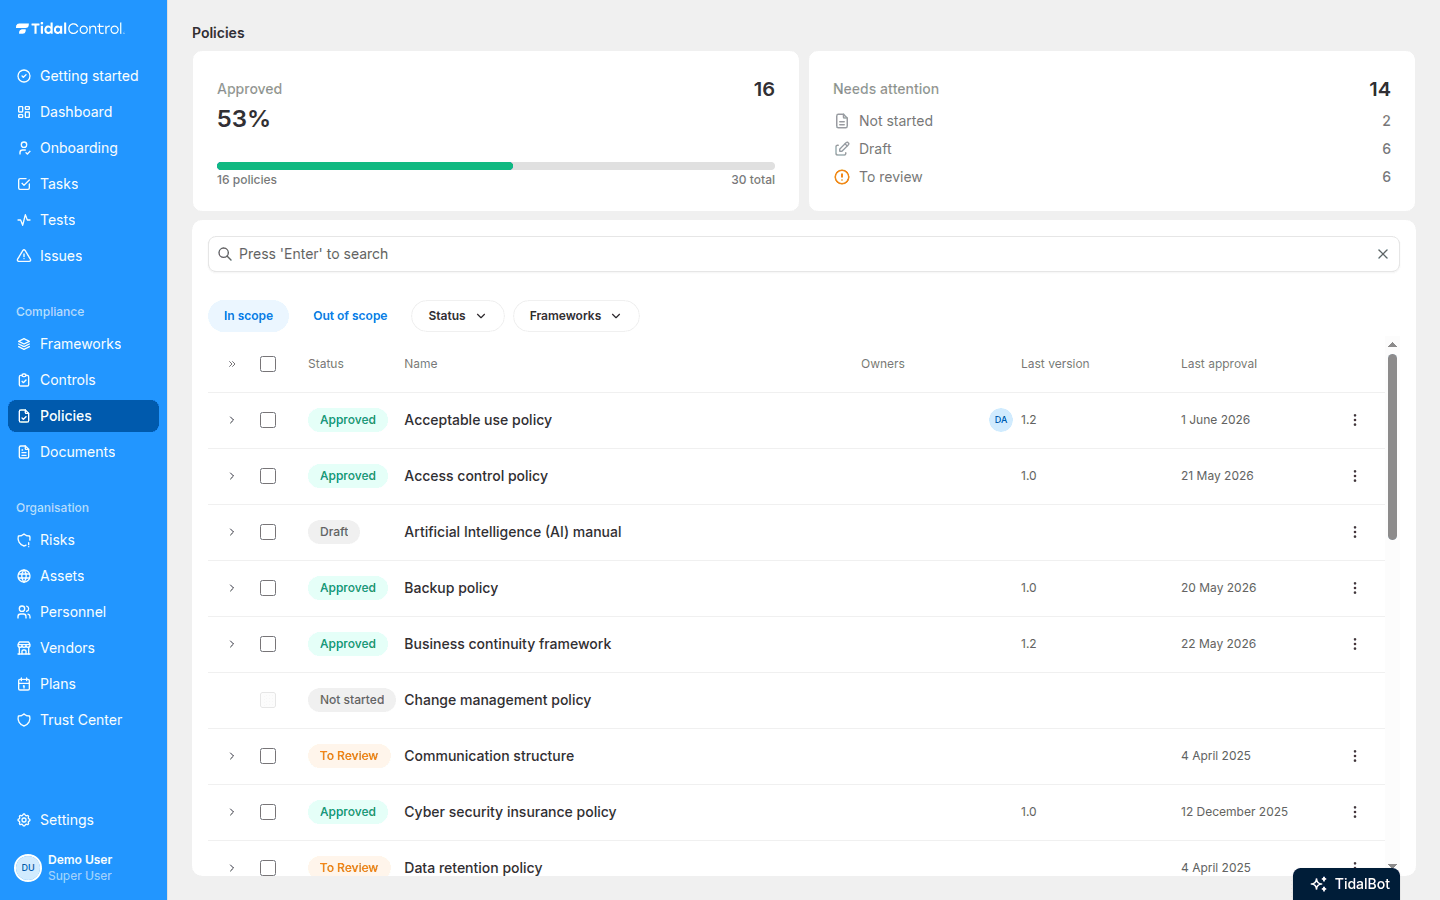
Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

Vendor management

Supplier risk assessment that actually works

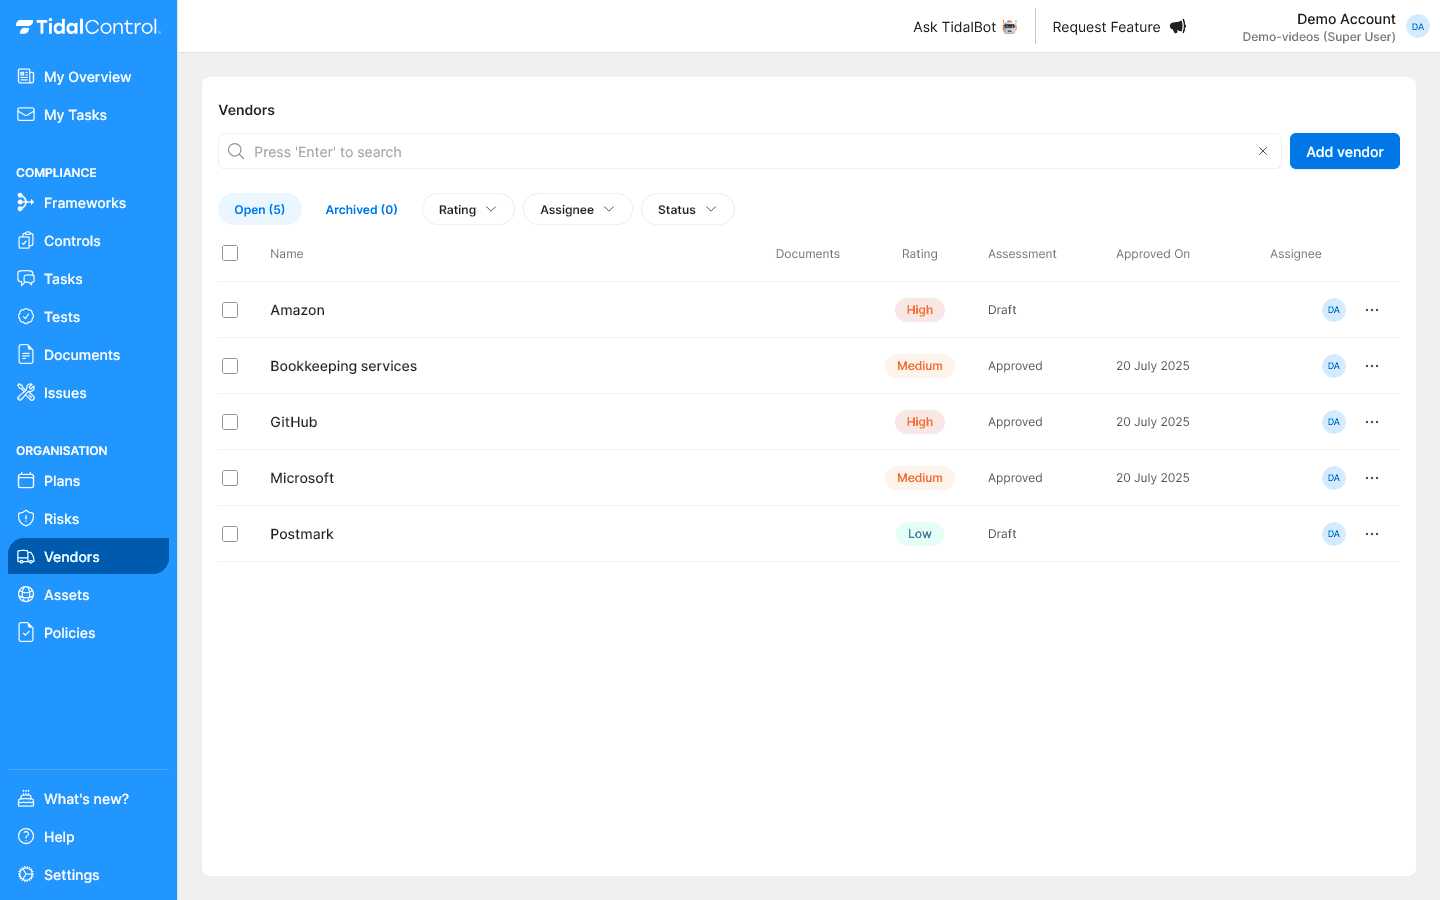
Transform supplier risk assessment from a time-consuming task into an automated process that helps your business grow. Add vendors in seconds with our vendor database that automatically fills in all important details, from privacy policies to SOC2 reports. Our intelligent system then automatically assesses risks and helps you make the right decisions.

Vendor management in Tidal ControlSupplier risk assessment that actually works

Personnel & onboarding

Employee compliance without the spreadsheet

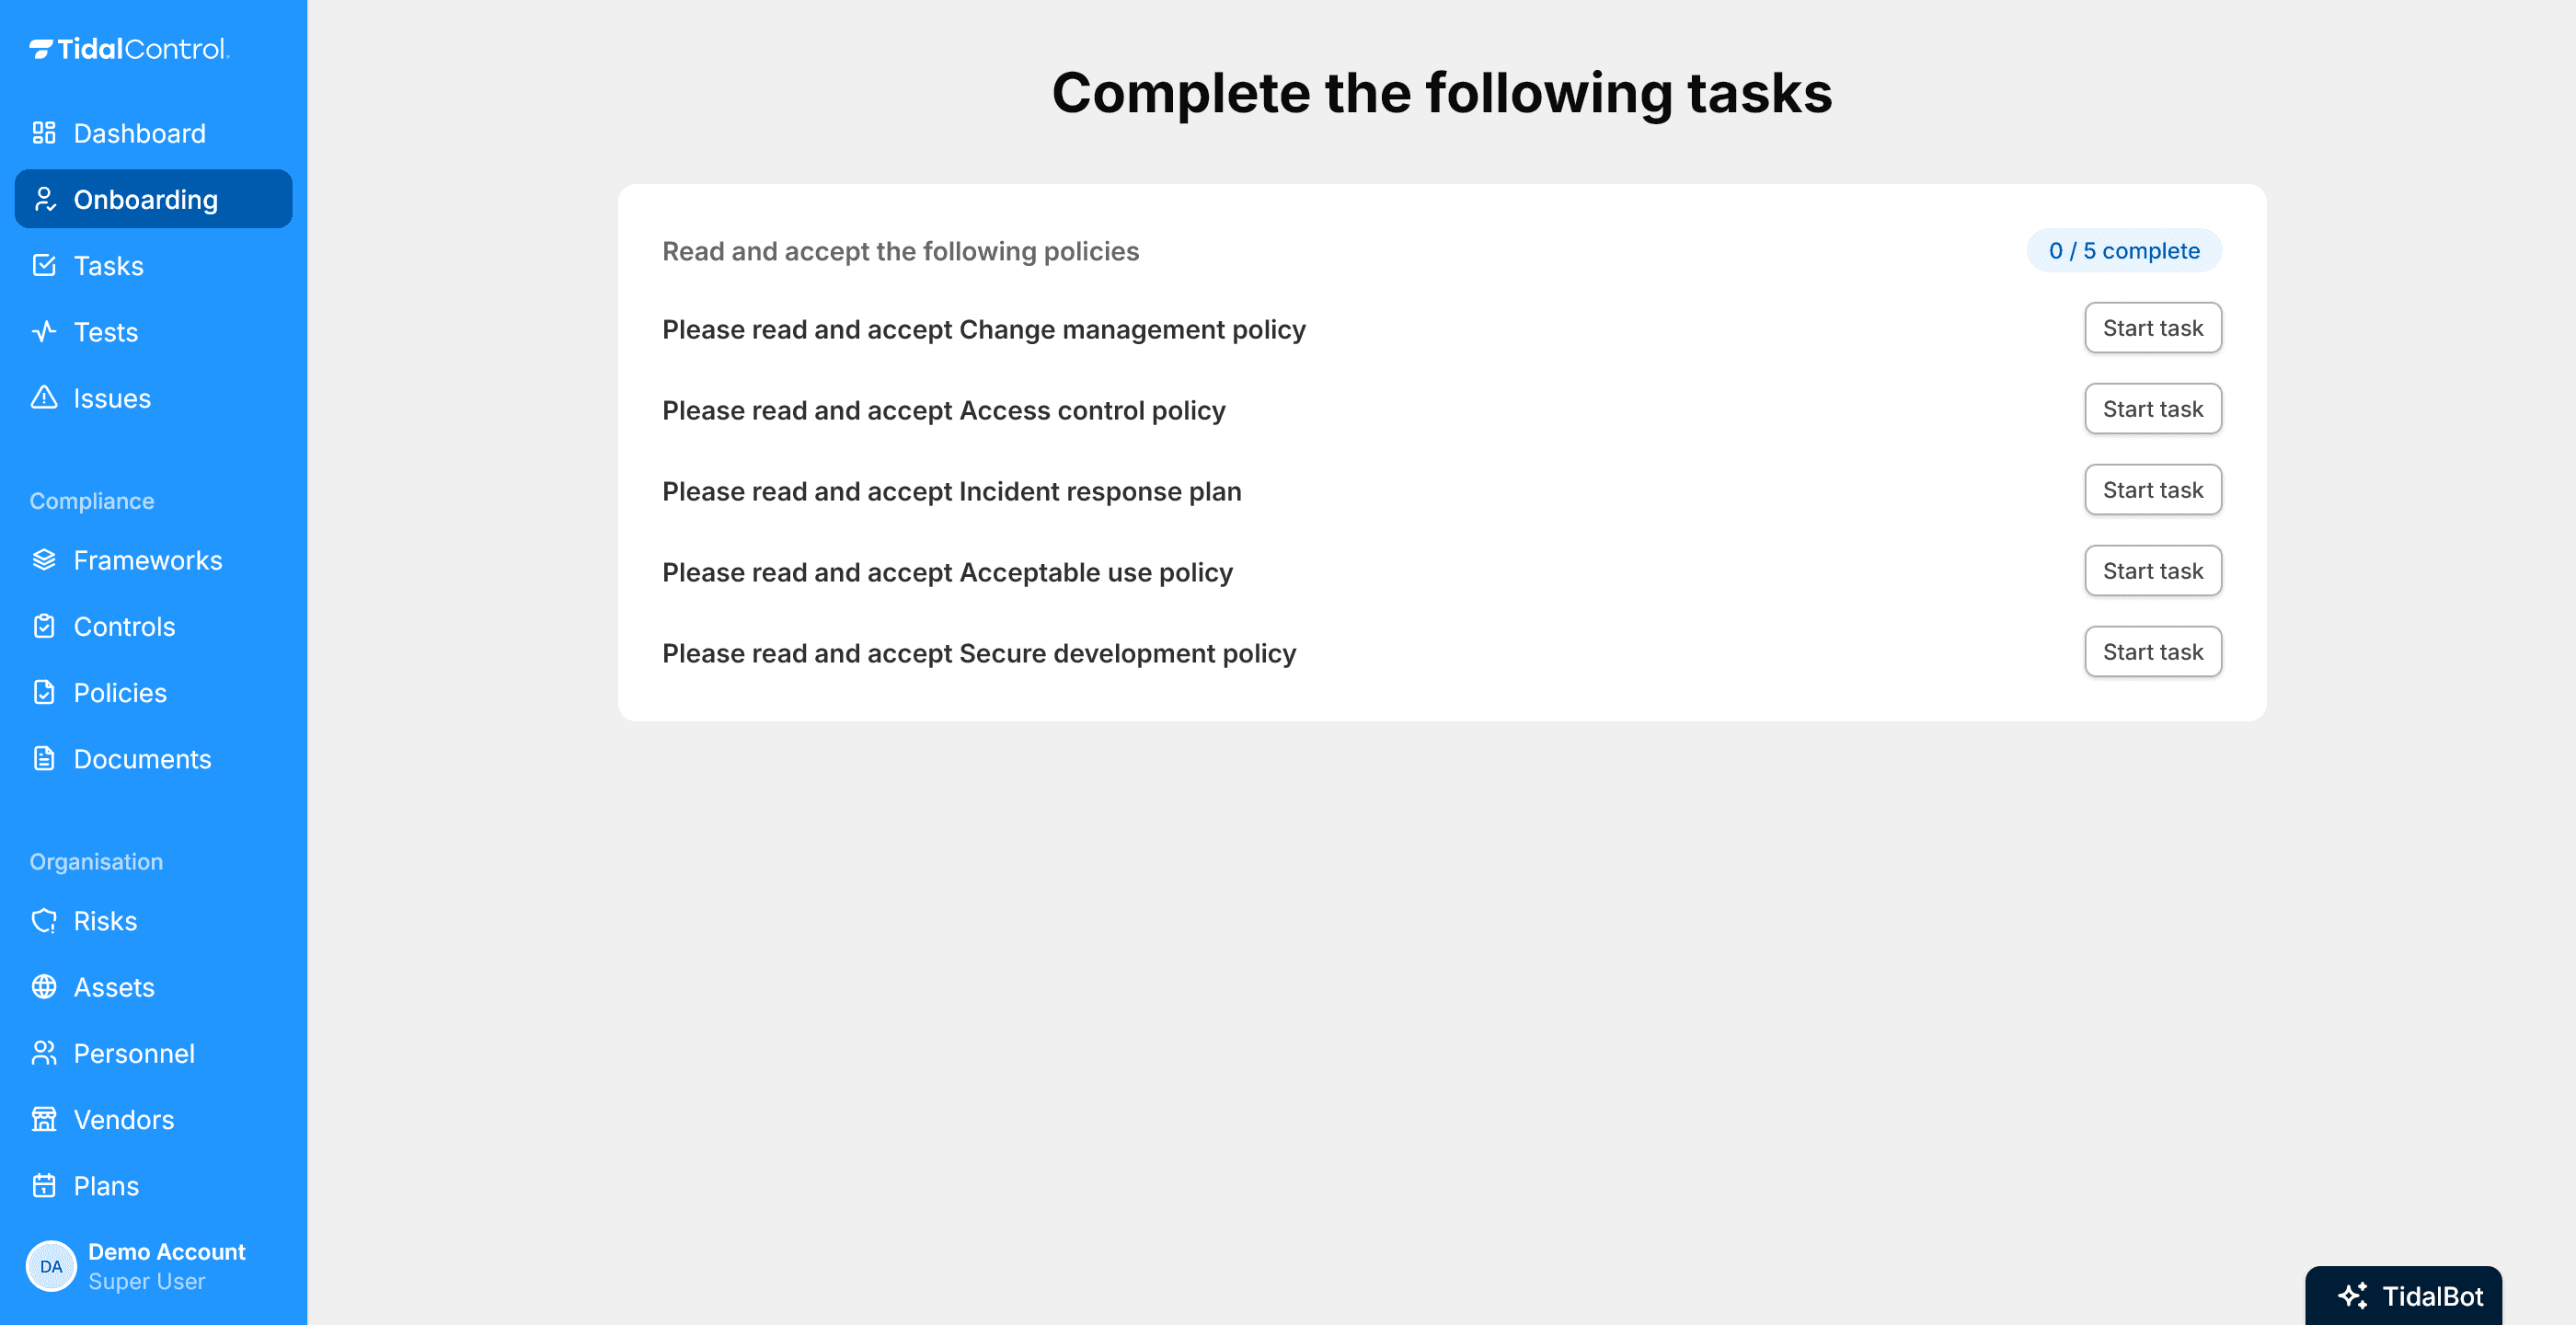
The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

Trust Center

Show prospects you take security seriously

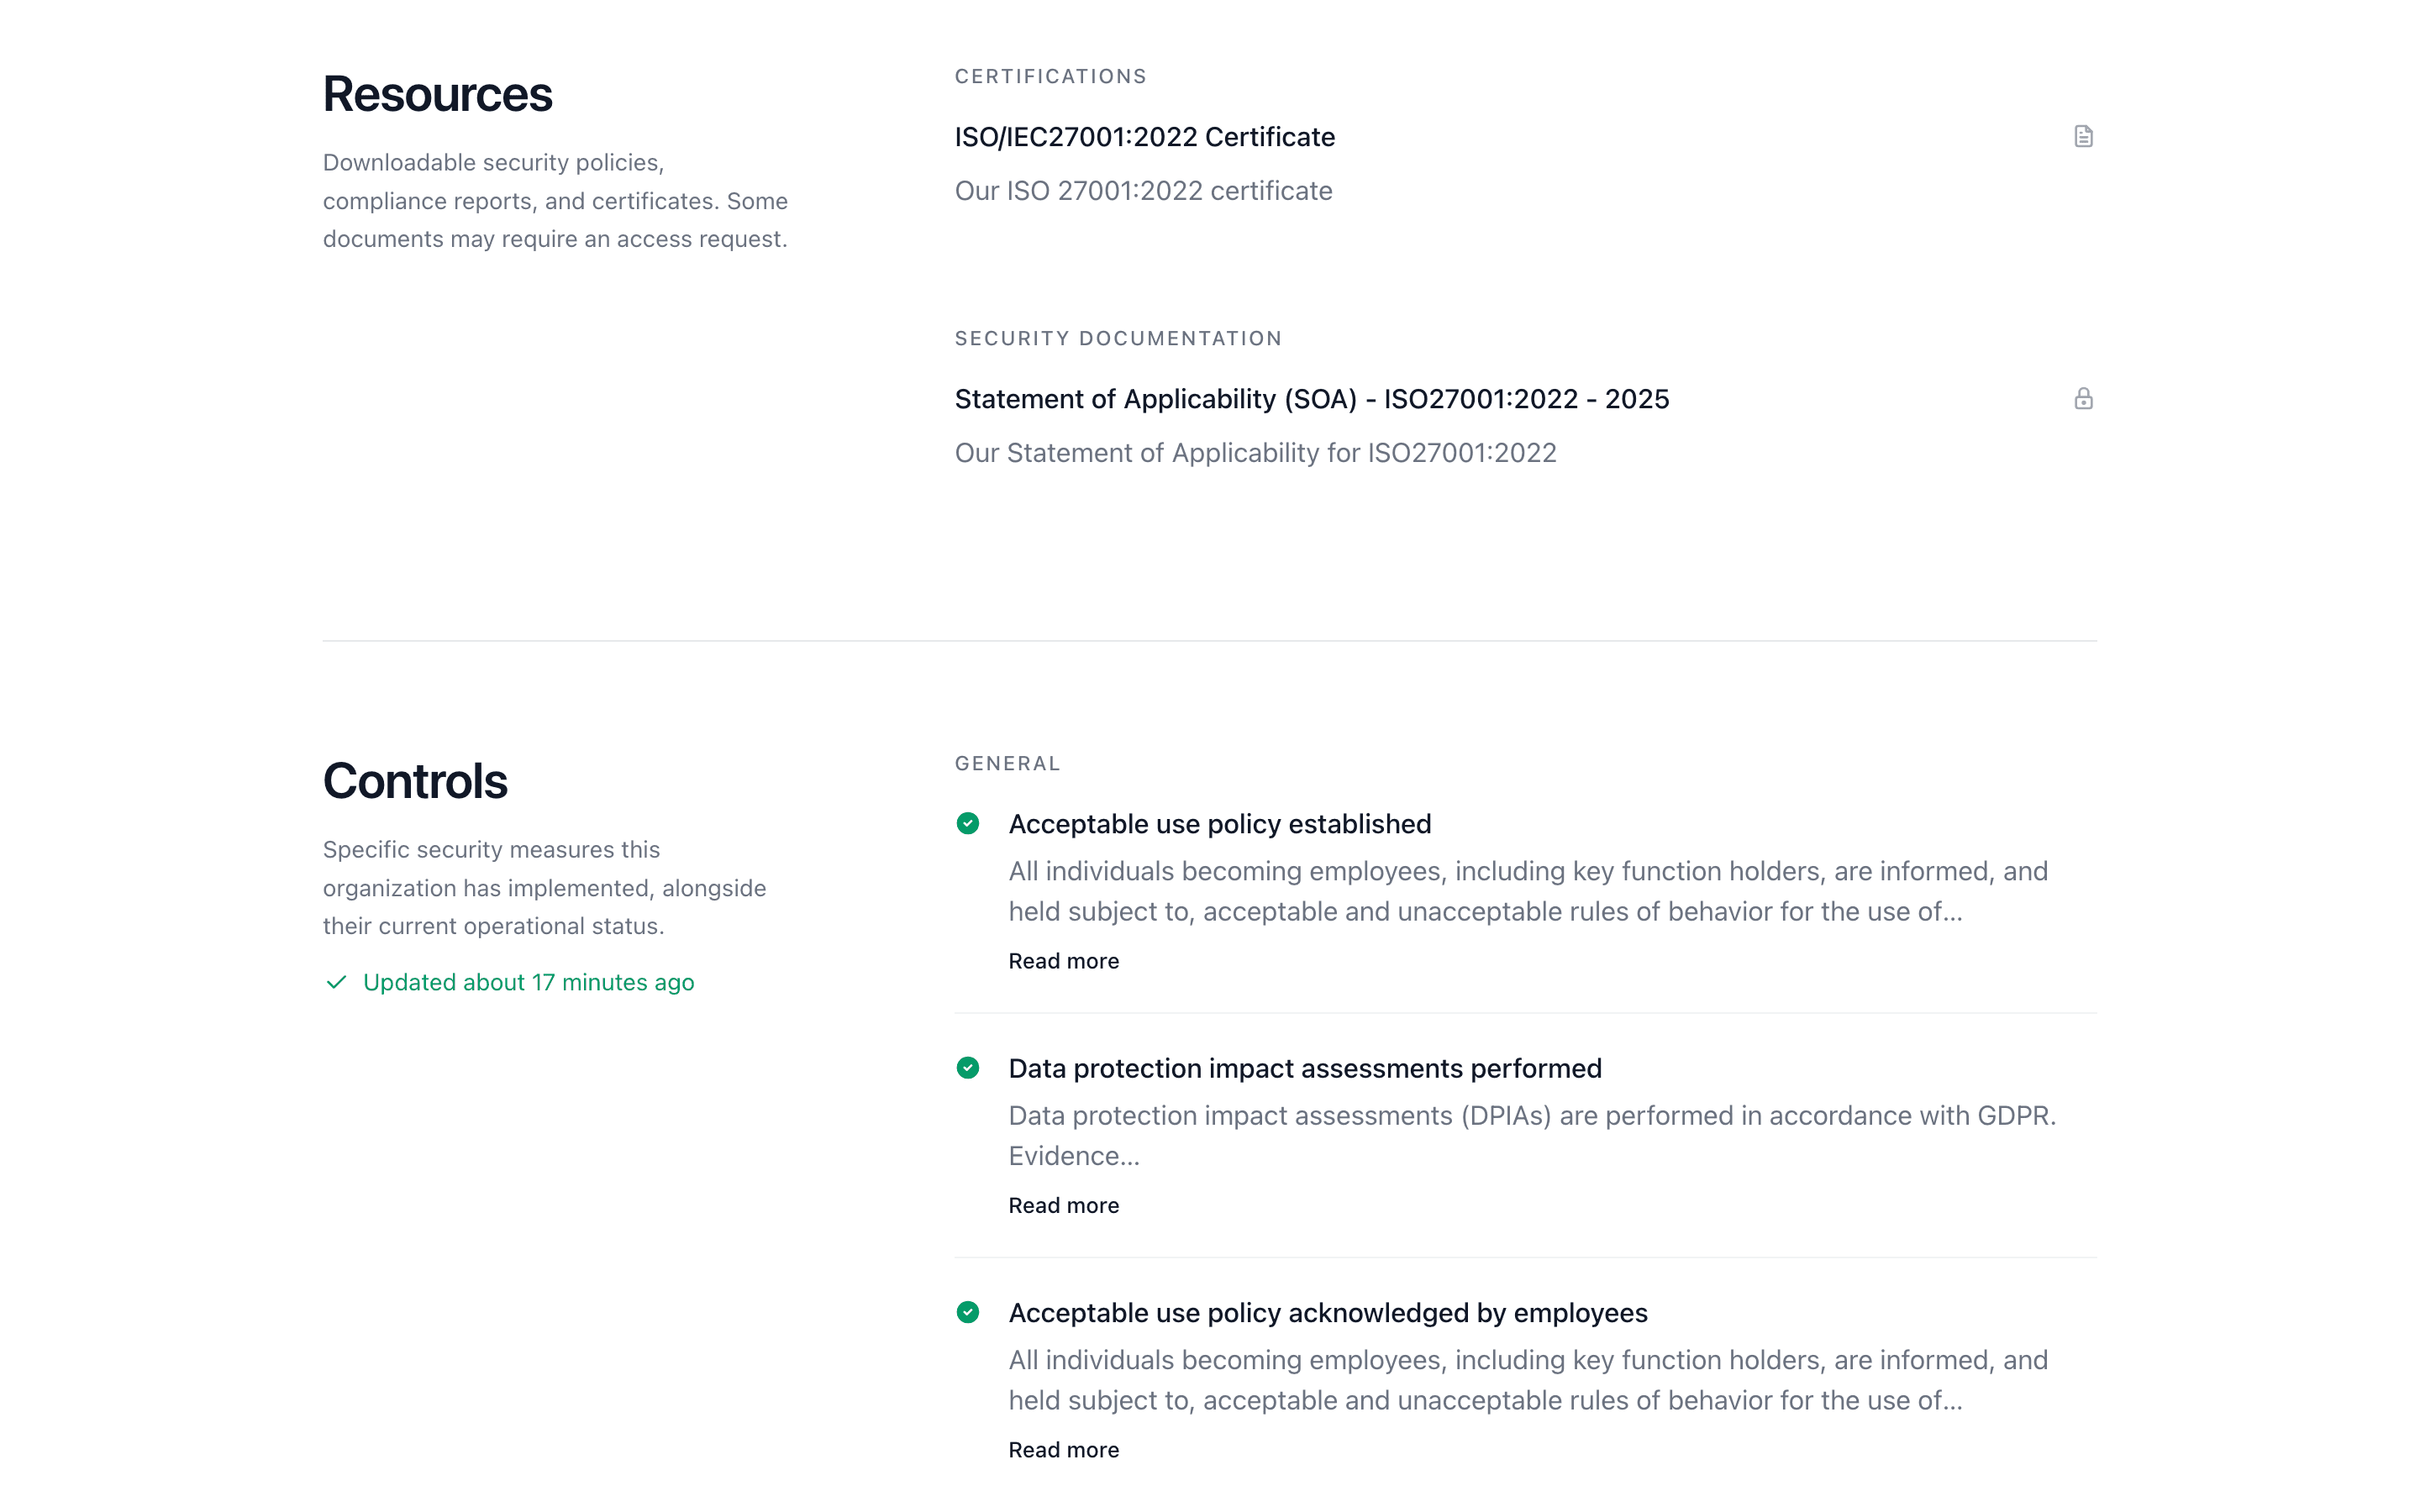
A Trust Center turns the security questions your sales team gets asked every week ("are you ISO 27001 certified?", "can I see your SOC 2 report?", "how do you handle data breaches?") into a public, auto-updated page. Built on the controls, policies, and certifications you already maintain in Tidal Control.

Trust Center in Tidal ControlShow prospects you take security seriously

Integrations

Automation makes life more fun!

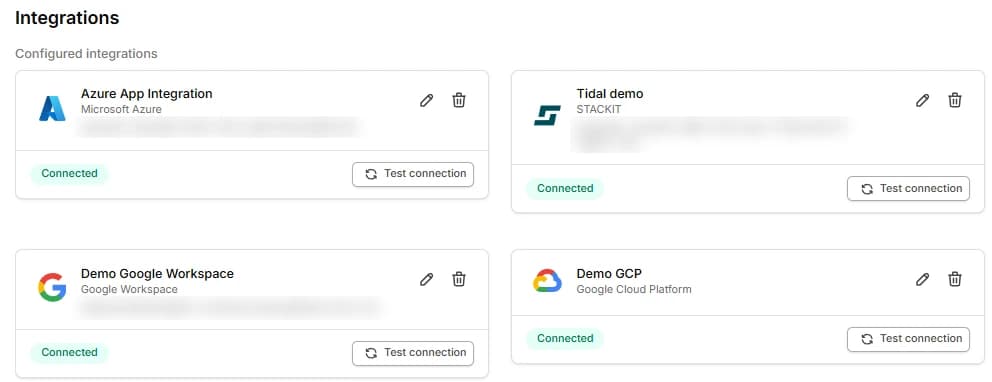
Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • Controls

    Manual

    Your own list per criterion

    With Tidal

    Pre-mapped with owners

  • Evidence over the period

    Manual

    Collecting screenshots just before the audit

    With Tidal

    Automatically from your tools, the whole period

  • Customer questionnaires

    Manual

    Filled in again every time

    With Tidal

    Report and answers in your trust center

  • SOC 2 and ISO 27001

    Manual

    Two projects side by side

    With Tidal

    One set of controls, evidence once

  • Audit preparation

    Manual

    Weeks of scrambling before the audit

    With Tidal

    Always audit-ready

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

See all success stories

Integrate with your existing tools

SOC 2 compliance software and the audit

A Type 1 report assesses whether your controls are designed well, at one point in time. A Type 2 report also assesses whether they operate, over a period of usually three to twelve months. Customers often ask for Type 2, because it shows it is not a snapshot.

Many organisations start with Type 1 so they have something to show, then begin the observation period for Type 2. Others skip Type 1 and start the period straight away.

Either way the same thing counts: controls that are agreed, owners who run them and evidence that shows it happens.

Frequently asked questions

No. SOC 2 is an audit report by an independent auditor, in practice usually a US CPA firm. You share the report under NDA with customers who ask for it. There is no SOC 2 certificate, although the word is often used that way.

It depends on what is already in place and on the length of your observation period. A Type 2 report usually covers three to twelve months, and that period only starts once your controls work. Tidal shows per criterion what is still open, so you know when you can start the period.

Security is mandatory for all SOC 2 reports. Beyond that, choose criteria based on your business needs and customer requirements. Common additions are Availability (for SaaS products) and Confidentiality (for handling sensitive data). Tidal helps you assess which criteria are relevant and implements appropriate controls.

Yes, we can recommend auditors experienced with our platform. However, you're free to work with any licensed CPA firm. Tidal's evidence collection and reporting features work with any auditor you choose.

Yes, Tidal supports both SOC 2 Type I and Type II audits. Our platform helps you establish controls for Type I and then transition to maintaining evidence for Type II's observation period. Our automated evidence collection is particularly valuable for Type II compliance.

Tidal integrates with major cloud providers (AWS, Azure, Google Cloud, Scaleway, Vercel), collaboration and development tools (GitHub, GitLab, Bitbucket, Jira, Atlassian Admin, Linear), identity and device management (Microsoft Entra ID, Google Workspace, Iru), observability and security (Datadog, Microsoft Sentinel), and CRM (HubSpot). We're continuously adding new integrations based on customer needs.

Our platform continuously monitors your controls and collects evidence automatically. You'll receive alerts for any gaps or issues, helping you maintain compliance year-round. This ongoing monitoring makes annual renewals much simpler.