ISO 27001 certification with software and GRC experts

The international standard for information security. Tidal Control builds and runs your ISMS, collects evidence automatically and keeps you continuously audit-ready. When you get stuck, a GRC expert is there.

  • 93 Annex A controls
  • Median 13 weeks to certificate
  • Evidence on autopilot
  • Built in the EU
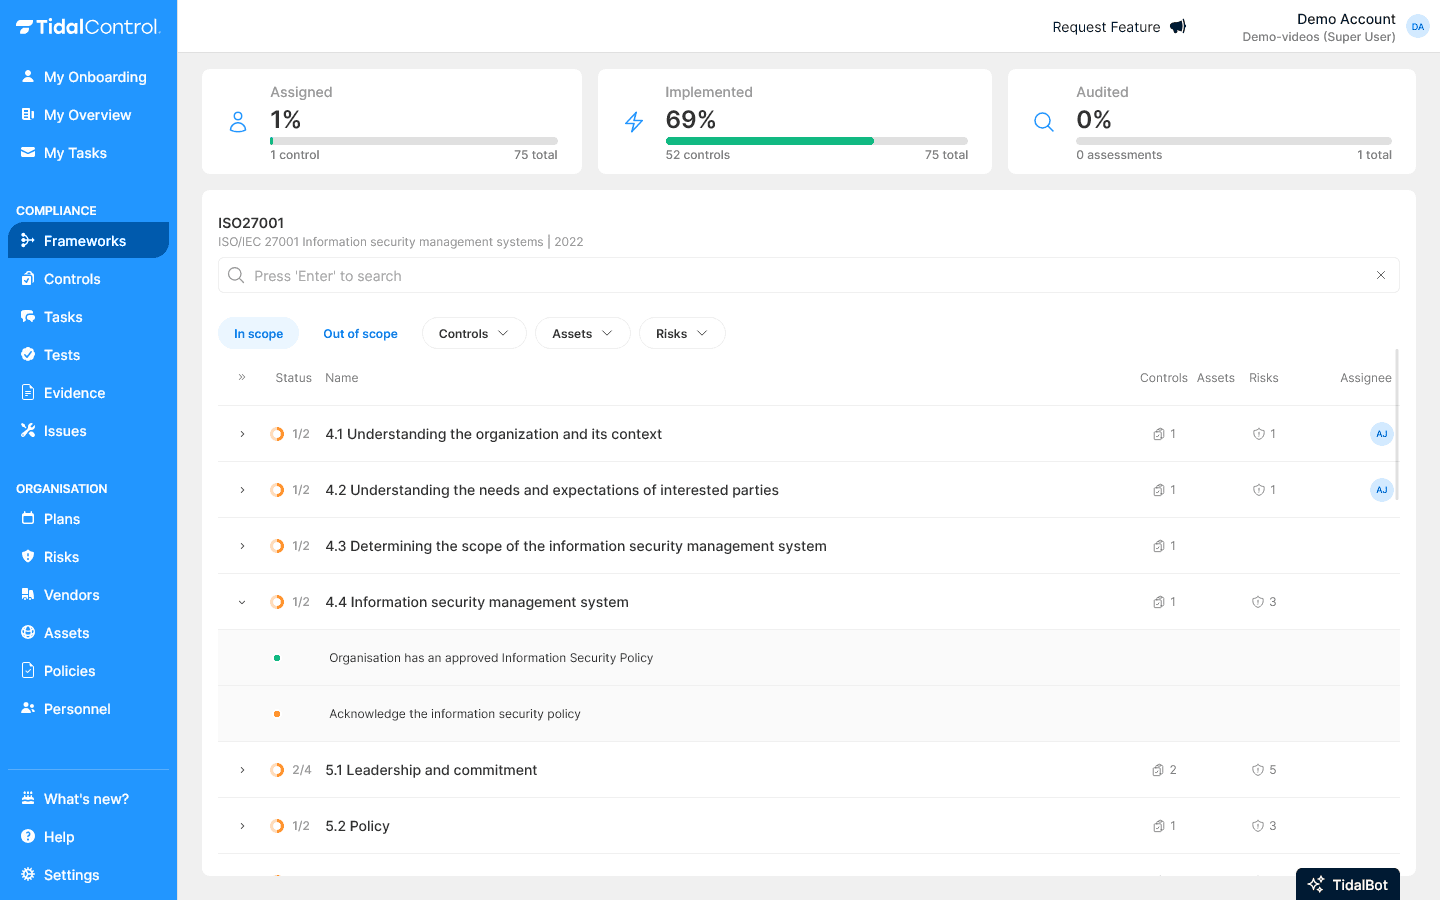
The ISO 27001 overview in Tidal Control showing control and evidence status

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From baseline to certificate

Across our customers the median is 13 weeks, not a promise of “instant compliant”. Tidal shows in every phase what is expected of your team, and it does not stop at the certificate.

  1. Week 1–2

    Baseline

    Set scope, run the gap analysis and start the risk register.

  2. Week 3–8

    Implementation

    Fill in policies, controls and evidence using templates.

  3. Week 9–10

    Internal audit

    Test yourself and run the management review.

  4. Week 11

    Stage 1 audit

    Documentation review by the certification body.

  5. Week 12–13

    Stage 2 and certificate

    Implementation audit and your ISO 27001 certificate.

  6. After that

    Audits and sparring

    Your annual audits prepared, and a sparring partner for new threats.

How Tidal helps you with all 93 controls

Tidal maps every one of the 93 Annex A controls to the four themes of ISO 27001:2022. For each control you record policy, evidence and owner in one place, and see at a glance what is still open.

controls pre-mapped
93controls pre-mapped
themes covered
4themes covered

Annex A · 93 controls

71 in order22 open

  • 37

    A.5

    Organisational

    28 of 37 demonstrably in order

  • 8

    A.6

    People

    6 of 8 demonstrably in order

  • 14

    A.7

    Physical

    11 of 14 demonstrably in order

  • 34

    A.8

    Technological

    26 of 34 demonstrably in order

ISO 27001 in brief

ISO 27001 is the international standard for information security. The certificate shows customers, partners and tendering bodies that you manage your risks demonstrably, through an Information Security Management System (ISMS). Tidal Control sets that ISMS up for you: pre-mapped controls, ready-made policies and evidence from your own tools, so you are ready for the audit.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • Win tenders that require certification
  • Show customers their data is safe
  • Fewer data breaches and incidents
  • A basis for the GDPR and NIS2
  • Insight into your risks, no surprises

How you work on ISO 27001 in Tidal

From risk assessment to vendor management: every part of your ISMS in one place.

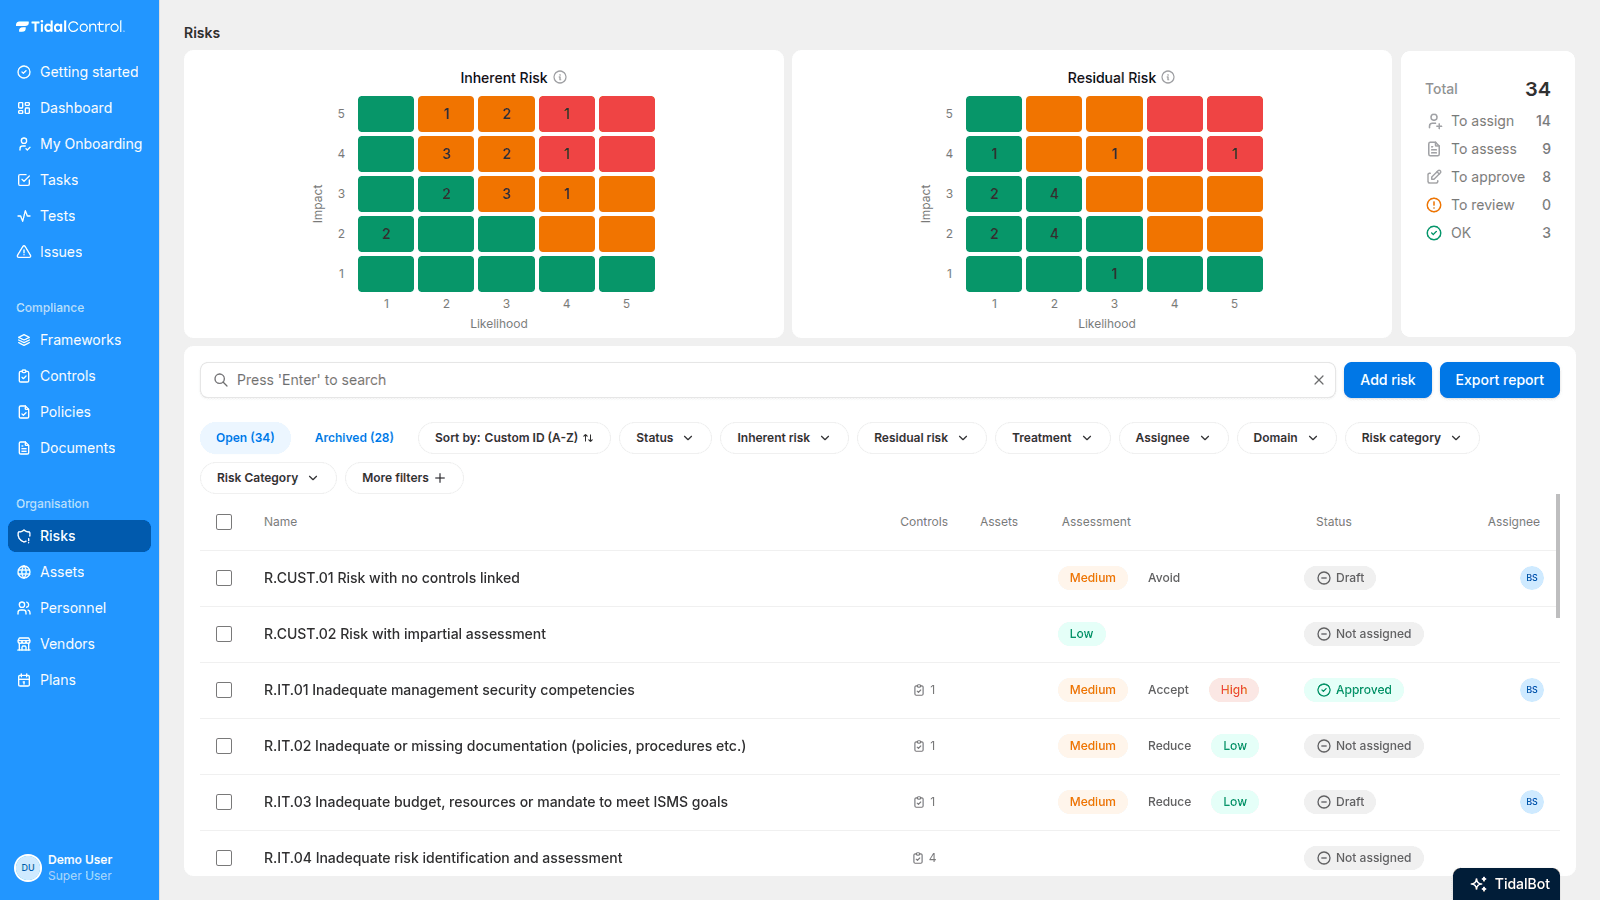
Risk assessment

Risk assessments that work

Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

Risk assessment in Tidal ControlRisk assessments that work
Controls management

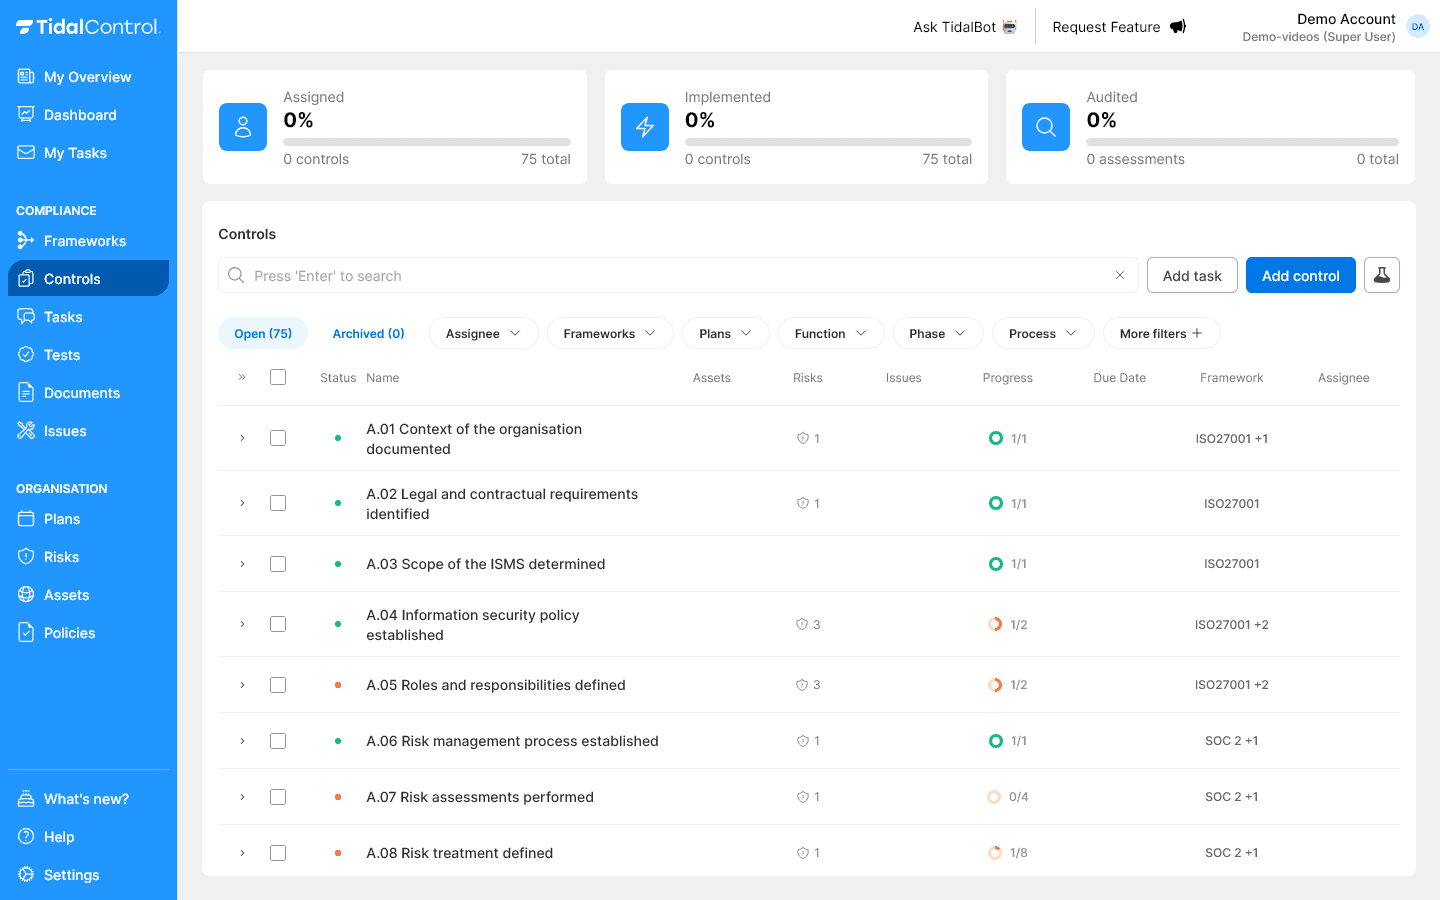
Control management that works your way

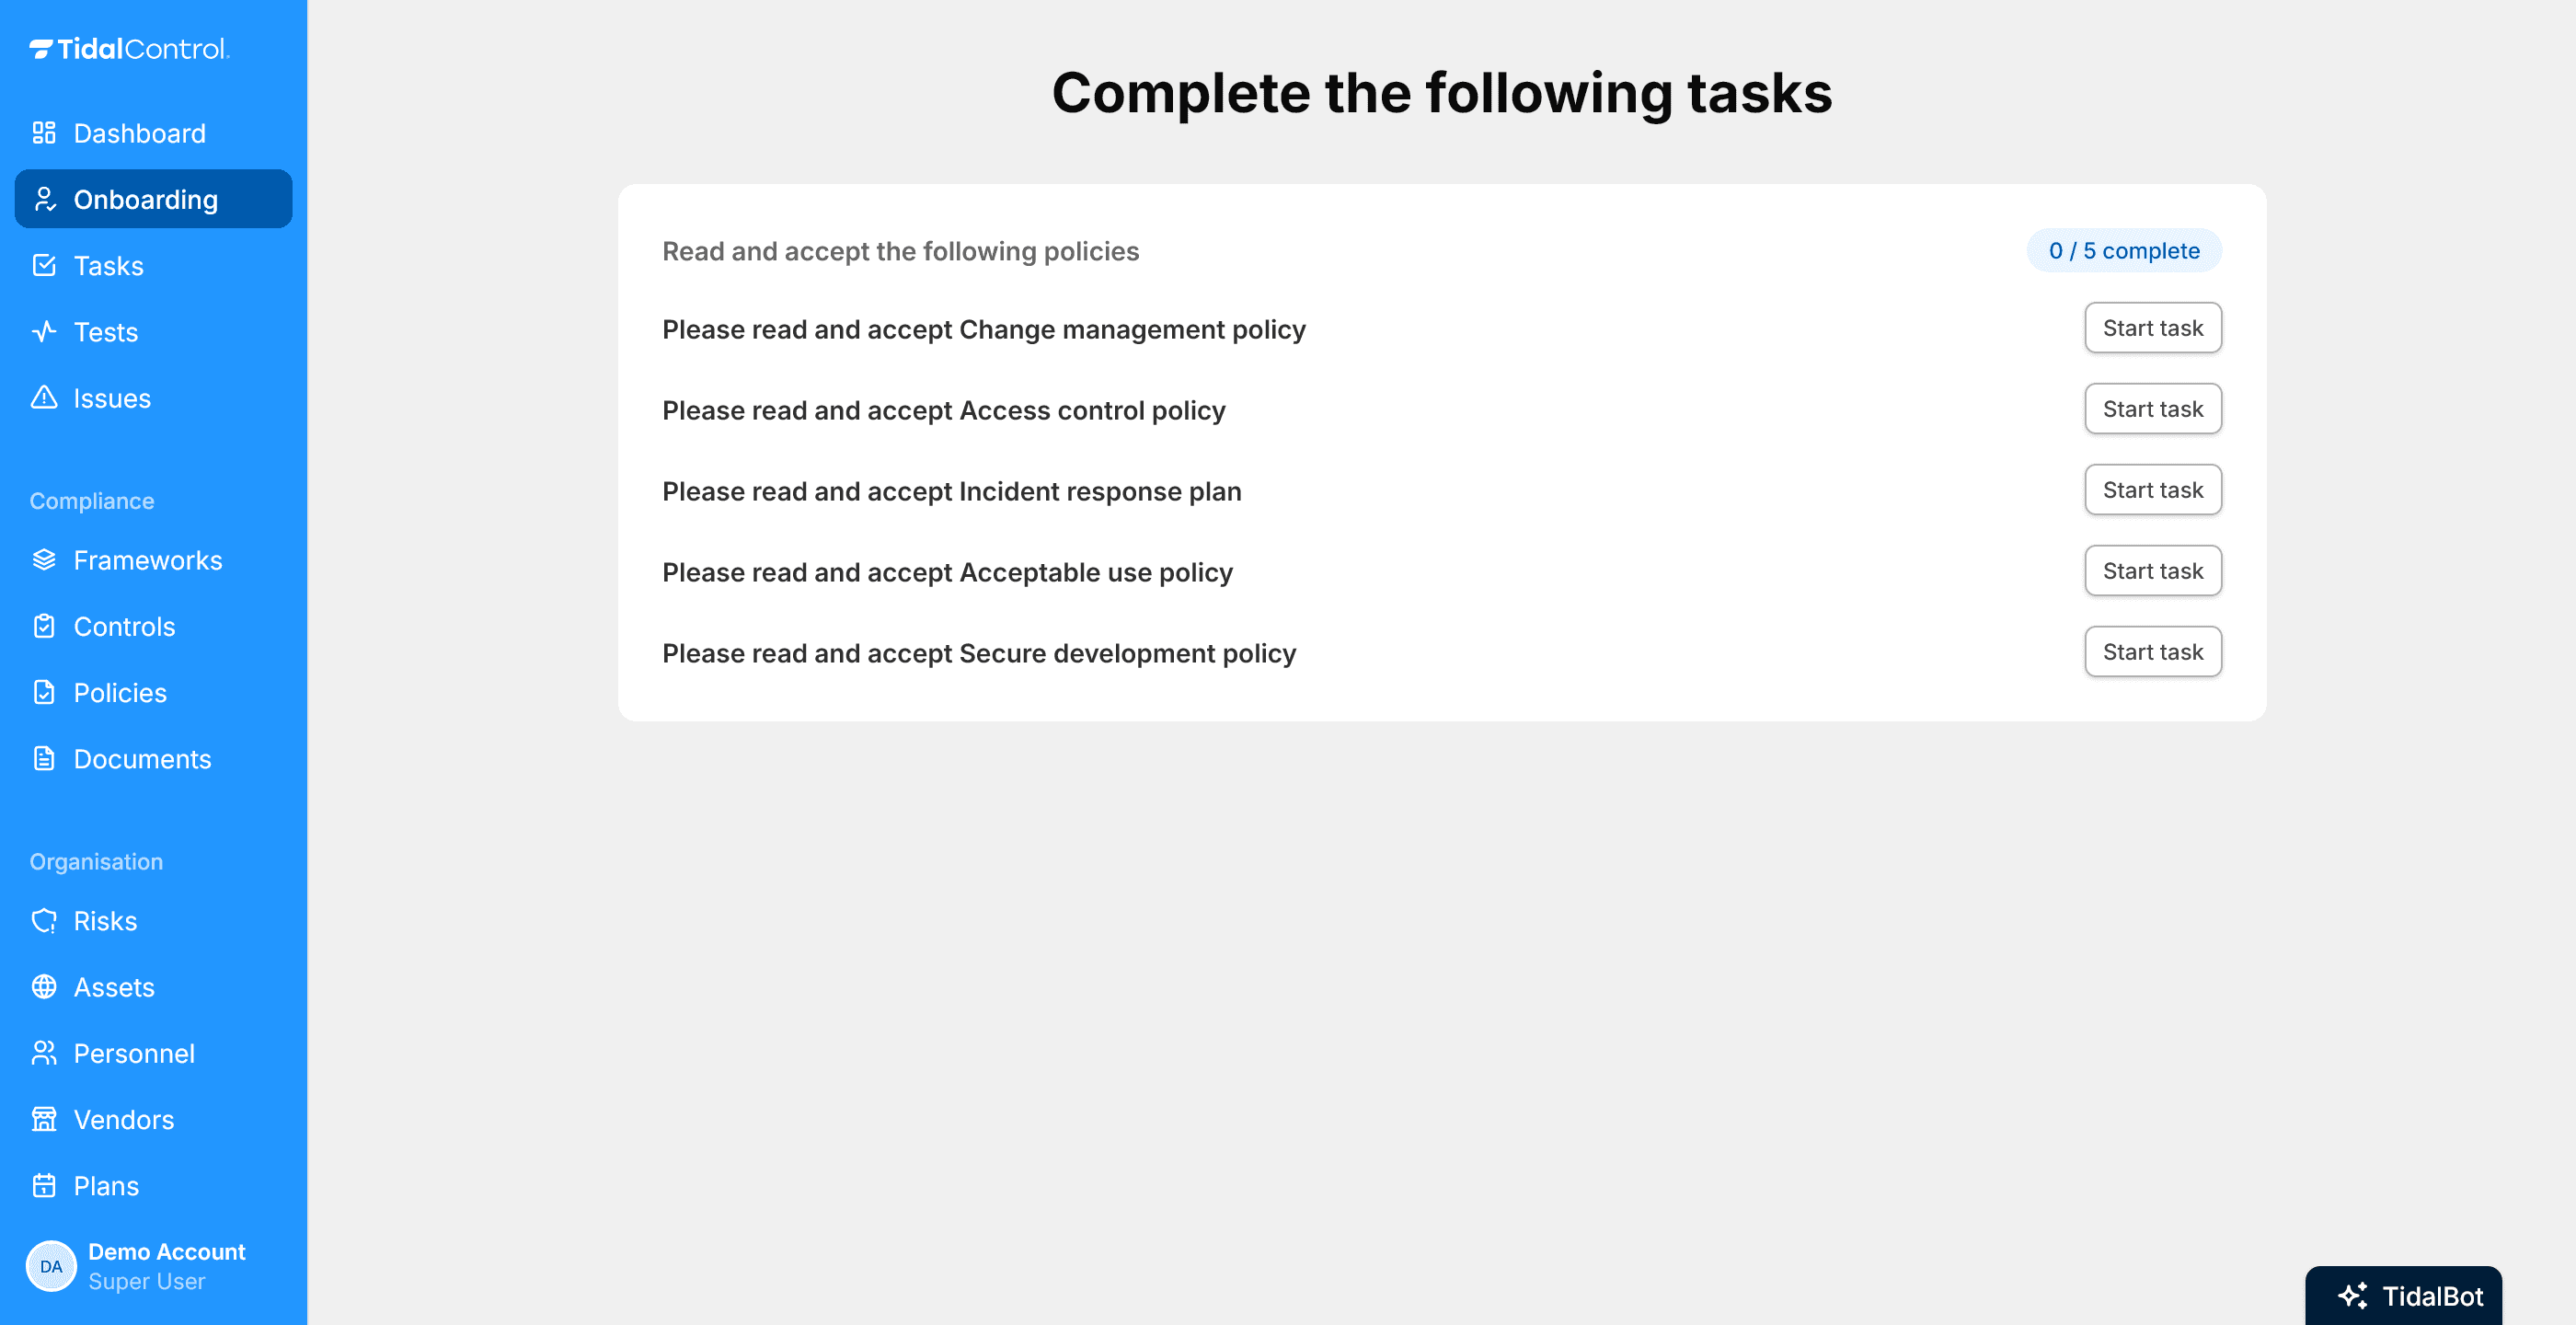
Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

Controls management in Tidal ControlControl management that works your way

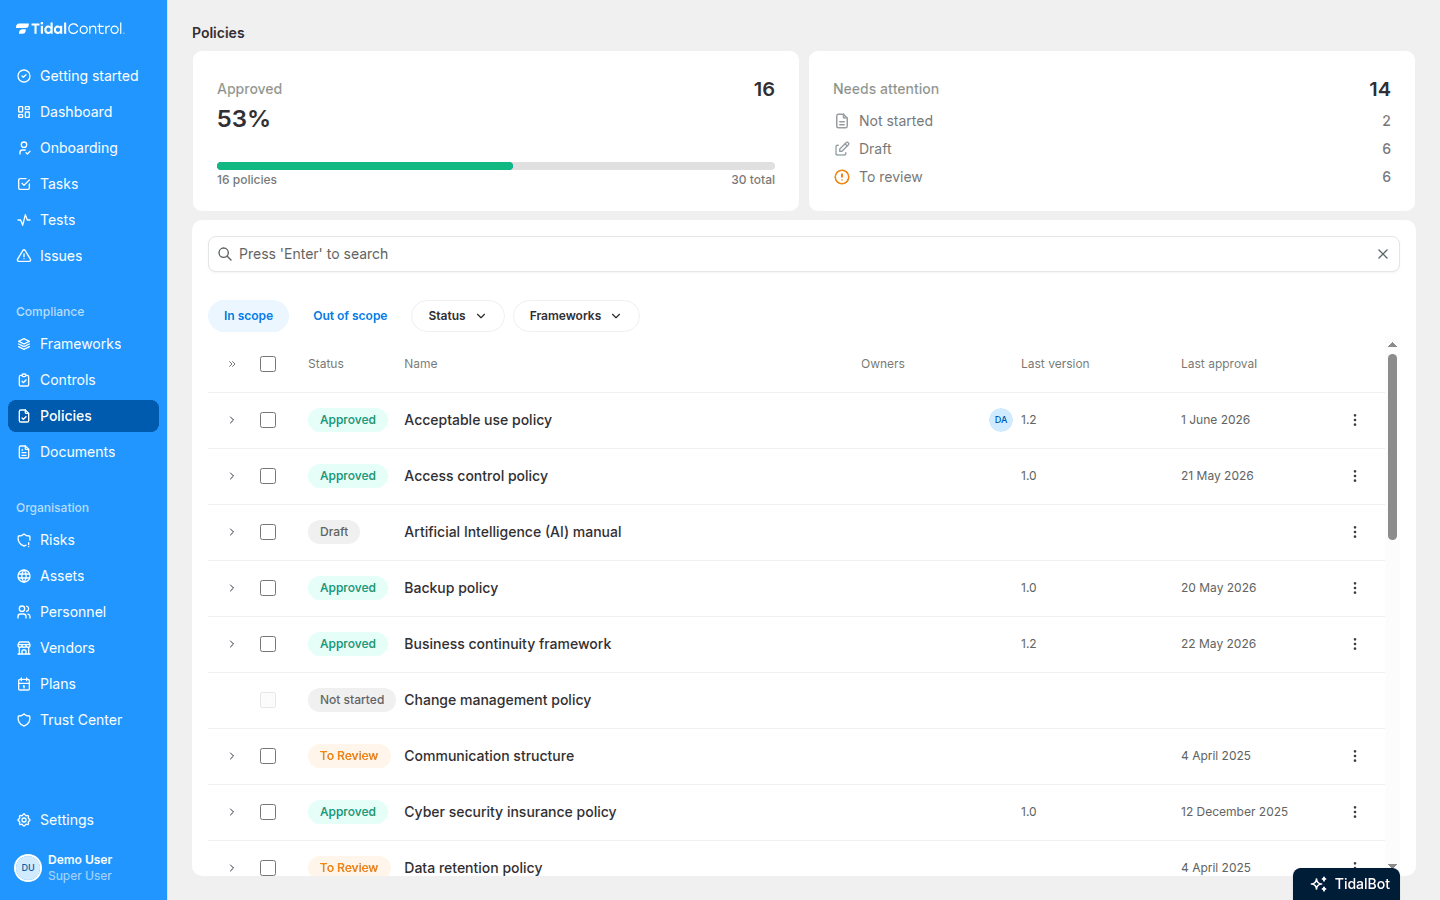
Policy center

Policies without the hassle

Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

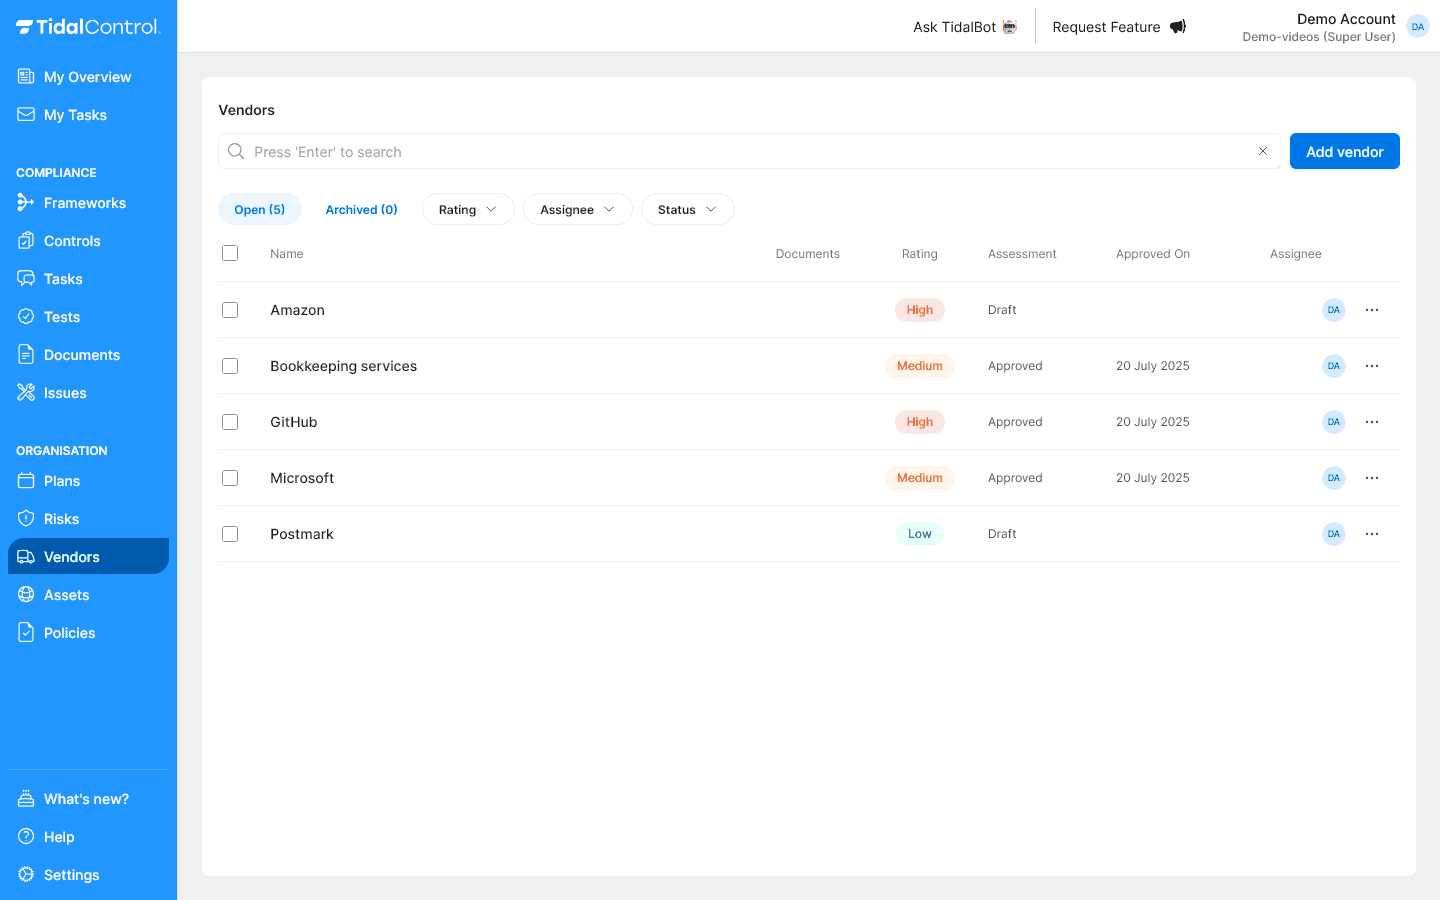
Vendor management

Supplier risk assessment that actually works

Transform supplier risk assessment from a time-consuming task into an automated process that helps your business grow. Add vendors in seconds with our vendor database that automatically fills in all important details, from privacy policies to SOC2 reports. Our intelligent system then automatically assesses risks and helps you make the right decisions.

Vendor management in Tidal ControlSupplier risk assessment that actually works

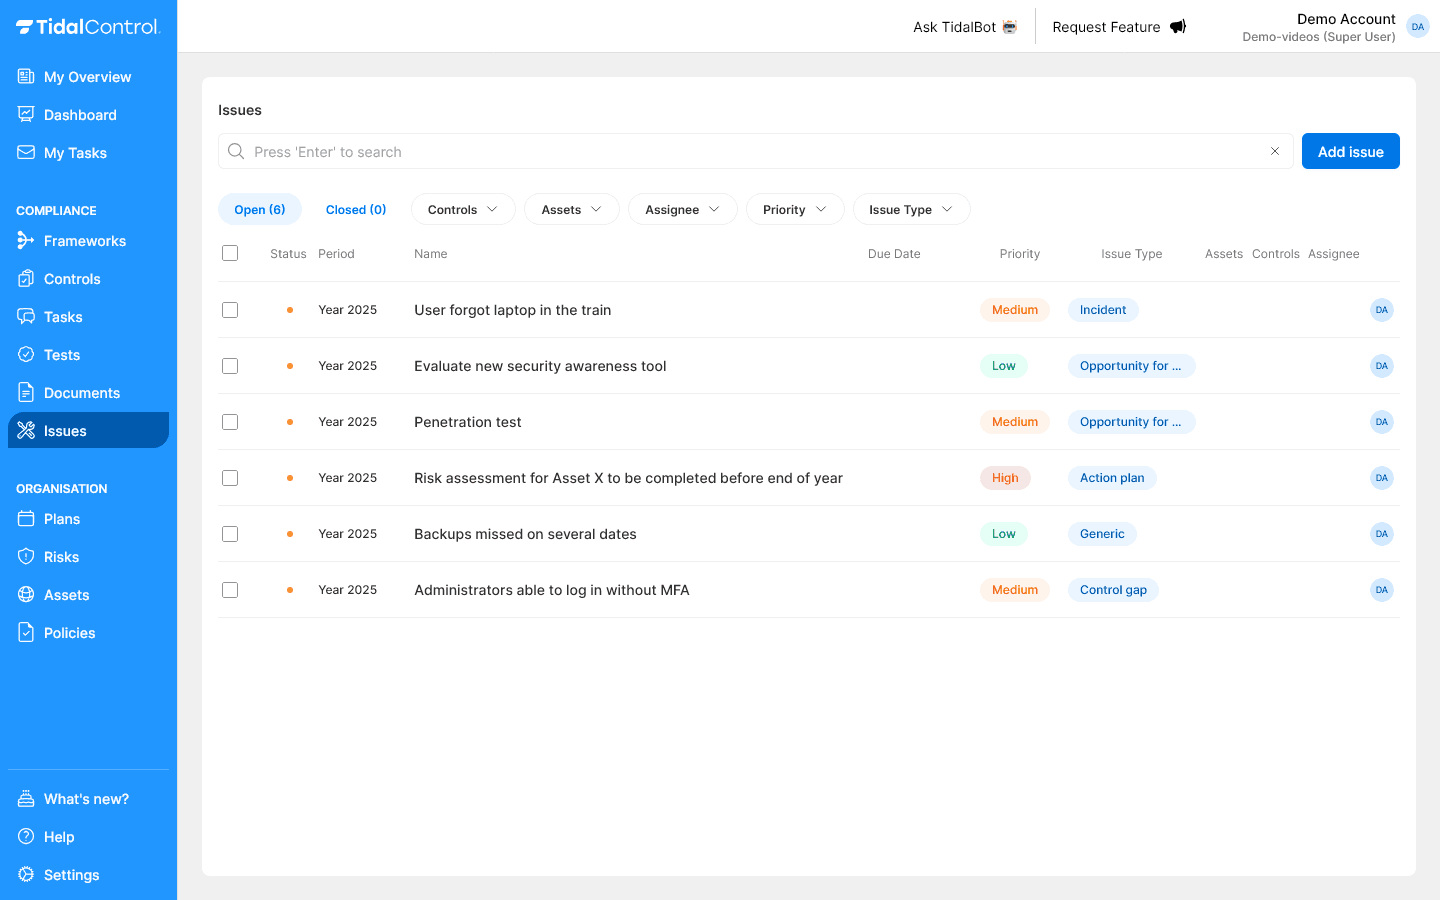
Issues management

Track and resolve issues - all in one place

Simplify issue management with a centralised system that handles everything from audit findings to improvement opportunities. Keep your team aligned and ensure nothing gets missed with clear ownership, priorities, and automated tracking.

Issues management in Tidal ControlTrack and resolve issues - all in one place

Personnel & onboarding

Employee compliance without the spreadsheet

The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

AI assistant

Compliance work with AI by your side

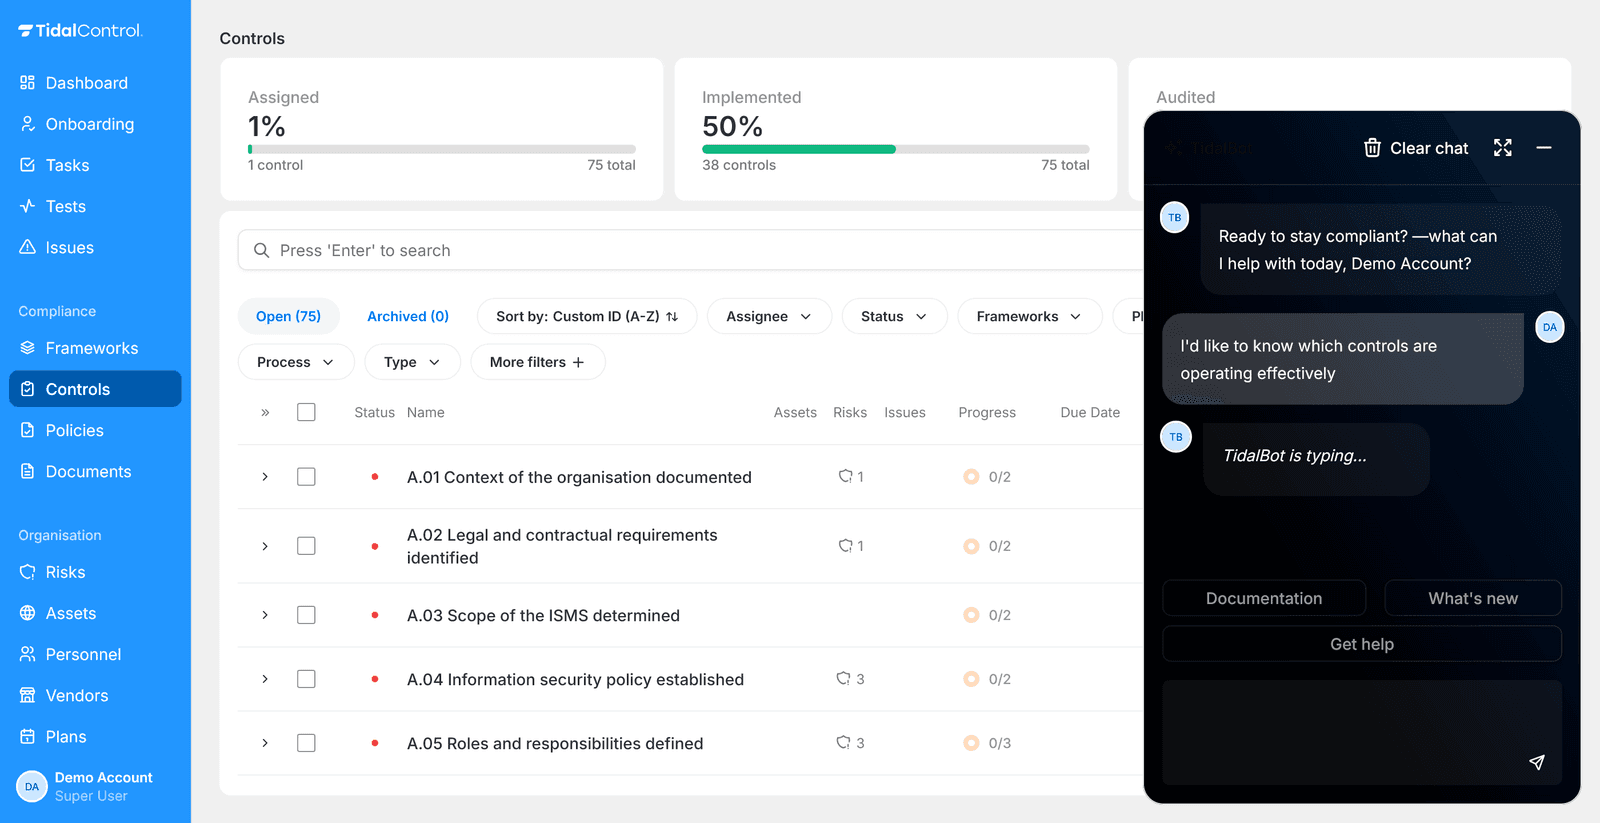
Tidal AI helps your team move faster on the work that used to take days: risk assessments, business impact analyses, policy drafting, control mapping. And with the Model Context Protocol (MCP) integration, you can now drive your entire compliance environment from Claude, ChatGPT, Codex, or VS Code, with permissions scoped to your role.

AI assistant in Tidal ControlCompliance work with AI by your side

Integrations

Automation makes life more fun!

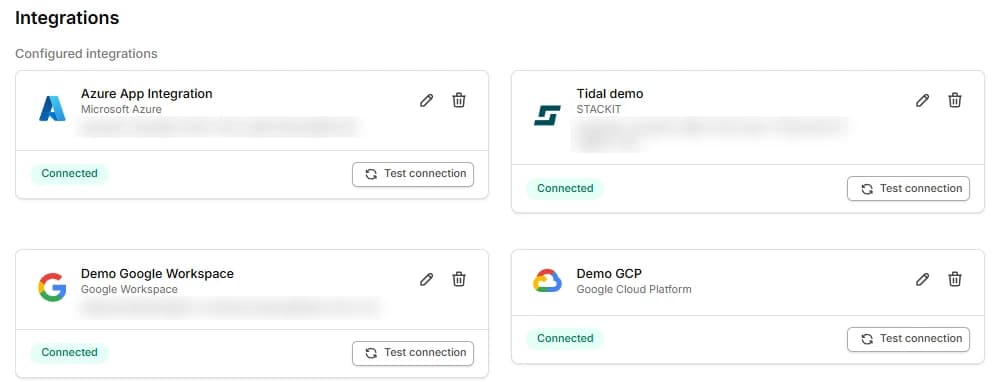
Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • Collecting evidence

    Manual

    Screenshots by hand, per control
    With Tidal

    Automatically from your tools

  • Managing controls

    Manual

    A spreadsheet with 93 rows

    With Tidal

    Pre-mapped, with owners

  • Audit preparation

    Manual

    Weeks of puzzling right before the audit

    With Tidal

    Always audit-ready

  • Keeping evidence current

    Manual

    Lapses between audits

    With Tidal

    Continuous monitoring

  • Time to certificate

    Manual

    Depends on who has time for it

    With Tidal

    Median 13 weeks to certificate

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

View all customer stories

Integrate with your existing tools

ISO 27001 software and certification

Many ISO 27001 software focuses on filling in templates and checking off controls for the audit. That helps at the start, but provides insufficient support once processes change, risks evolve, or multiple standards must be managed simultaneously.

Effective ISO 27001 software connects risk analysis, Annex A controls, and the Statement of Applicability with daily processes and ownership. This makes it always clear which measures apply, why they were chosen, and how they are followed up.

By continuously monitoring controls and automatically capturing evidence, ISO 27001 remains current. Compliance becomes not a periodic effort, but an ongoing process that moves with the organisation and its risk profile.

Frequently asked questions

An independent, accredited certification body. Tidal does not certify you itself, and that independence is what gives the certificate its weight: an auditor with no stake in the outcome tests whether your ISMS works in practice. Tidal gets you ready for that audit. Our customers have passed more than 50 audits, with 0 to 2 findings on average.

Most organisations achieve certification within 3-5 months using our platform. This includes establishing your ISMS, implementing controls, and conducting internal audits. Our pre-built content and automation tools significantly reduce the time typically needed for certification.

Yes, our platform guides you through the scoping process with templates and best practices. We help you identify relevant assets, processes, and locations to include in your ISMS scope, ensuring it's appropriate for your business while remaining manageable.

Our platform includes a risk assessment module with pre-identified risks and controls. The AI-powered system learns from your context to suggest relevant risks and controls, while automation helps you track risk treatment and reassessment over time.

Yes, we provide all required ISO 27001 documentation templates, including policies, procedures, and records. These templates are customisable to your needs while ensuring you meet all ISO 27001 documentation requirements.

We help you prepare for both Stage 1 and Stage 2 audits with pre-audit assessments and gap analysis. Our platform organises your evidence and documentation in an auditor-friendly format, making the certification process smoother.

Our platform automates many maintenance tasks including evidence collection, control testing, and review scheduling. You'll receive automated alerts for upcoming reviews, potential gaps, and required actions, helping you maintain certification with less effort.