BIO and ABDO for public sector organisations
One platform for the BIO, your ENSIA accountability and ABDO. Ready-made control frameworks, evidence that collects itself, and one dossier your IT auditor and the executive board can both look into.
- BIO, ENSIA and ABDO on one set of controls
- Evidence that collects itself through integrations
- Built and hosted in the EU
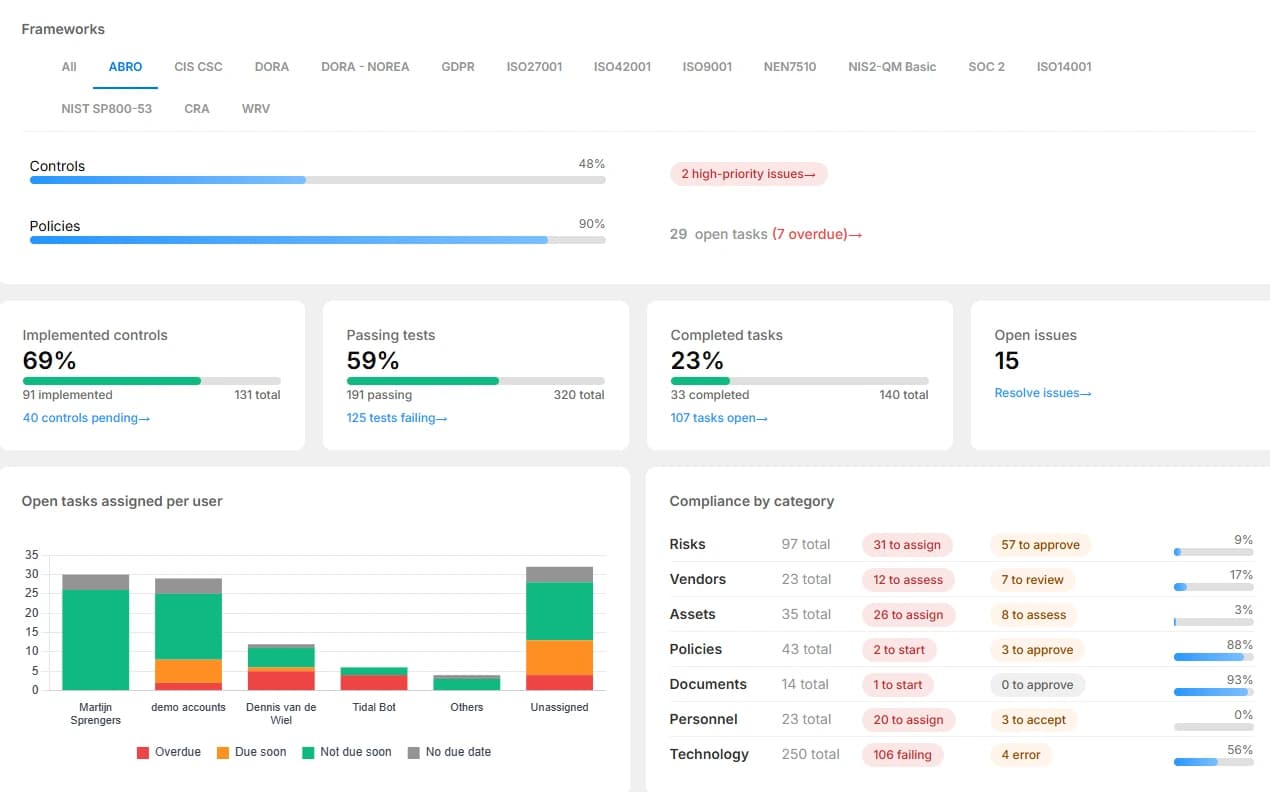
What public sector organisations achieve with Tidal
- 35+
- Frameworks on one set of controls, including BIO, ABDO and ISO 27001
- 300+
- Automated tests on your cloud and tooling
- 1 dossier
- For your IT auditor and the executive board, instead of separate folders
Why the BIO is a sprint every year
The work runs all year, the accountability comes once a year.
Searching again every year
For the ENSIA cycle, evidence is gathered from scratch each time, out of folders and mailboxes.
Outsourcing without oversight
Hosting, case management and archiving sit outside the organisation, but the responsibility does not.
Controls without an owner
When nobody owns a control, it waits until just before the accountability round.
Frameworks side by side
BIO, ENSIA and sometimes ABDO are kept separately, while the controls largely overlap.
How public sector organisations use Tidal
From the BIO controls to the executive statement, always from the same source.
The BIO controls, set up and ready
The BIO is the mandatory baseline for central government, municipalities, provinces and water authorities, and follows the structure of ISO 27002. In Tidal those controls are mapped and waiting, each with an owner and a status, so you never start from a blank page.
More on the BIO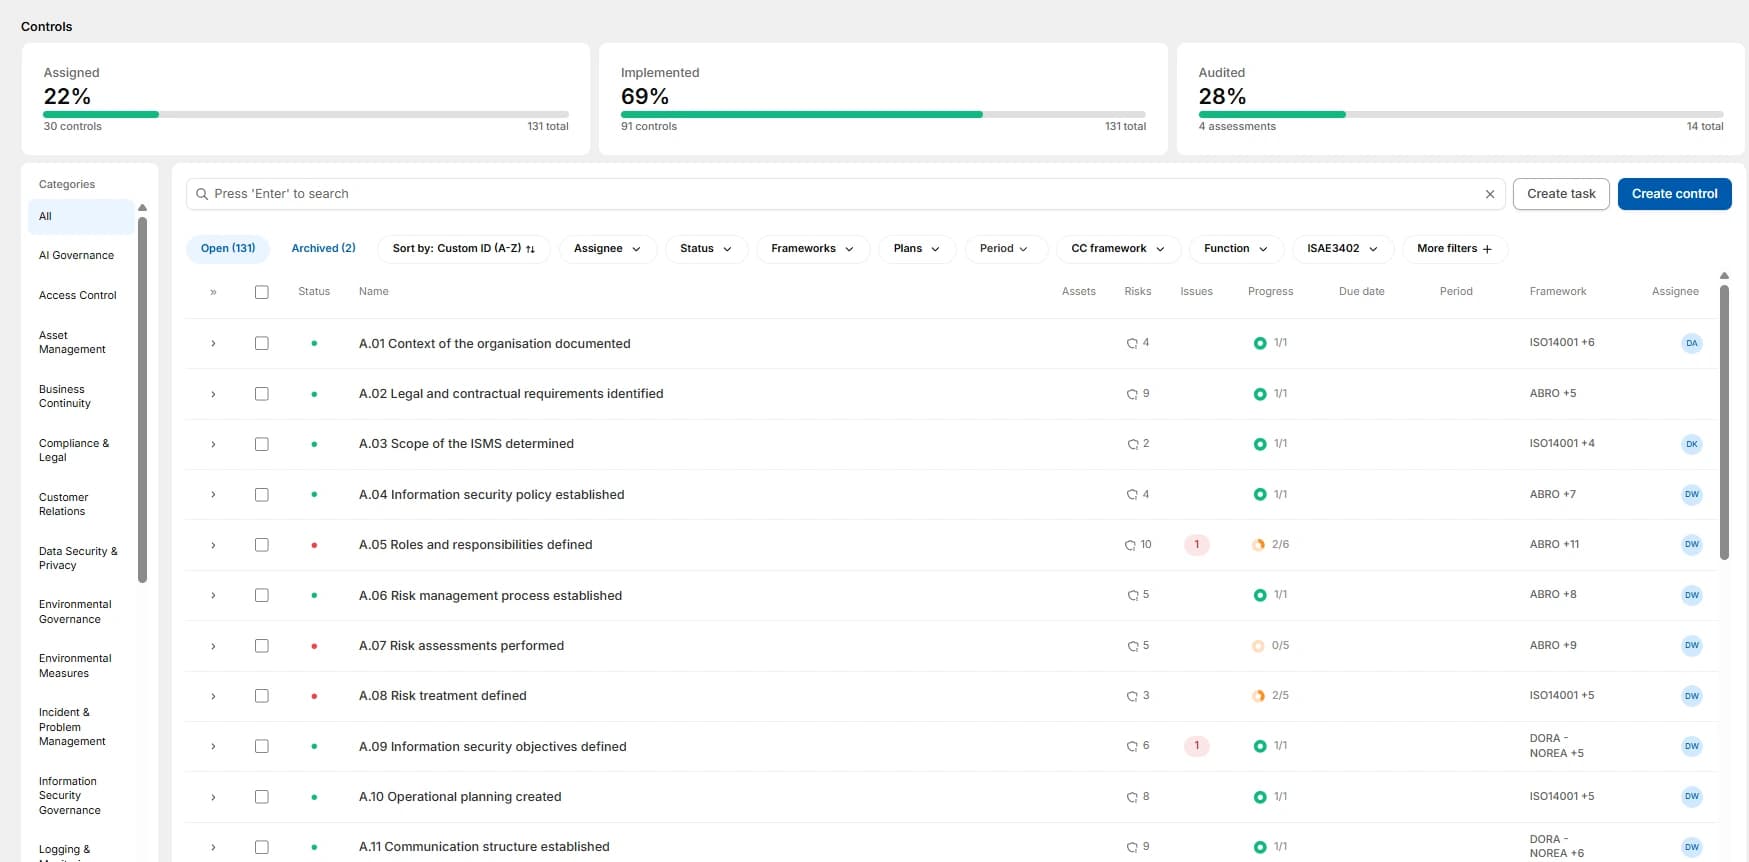
Evidence for your controls collects itself
Connect Azure and Entra ID and the rest of your tooling. Tidal pulls the evidence in automatically and attaches it to the right control, so you stop chasing screenshots when the ENSIA cycle comes round again.
See all integrations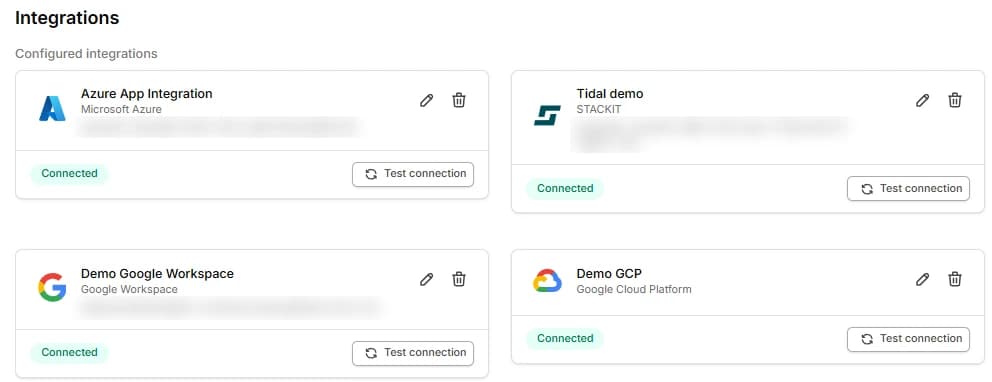
Outsourcing in view, including the risk
You may outsource the work, not the responsibility. From hosting provider to case management system: Tidal tracks the risk per supplier and whether the security annex to the contract actually exists.
More on vendor management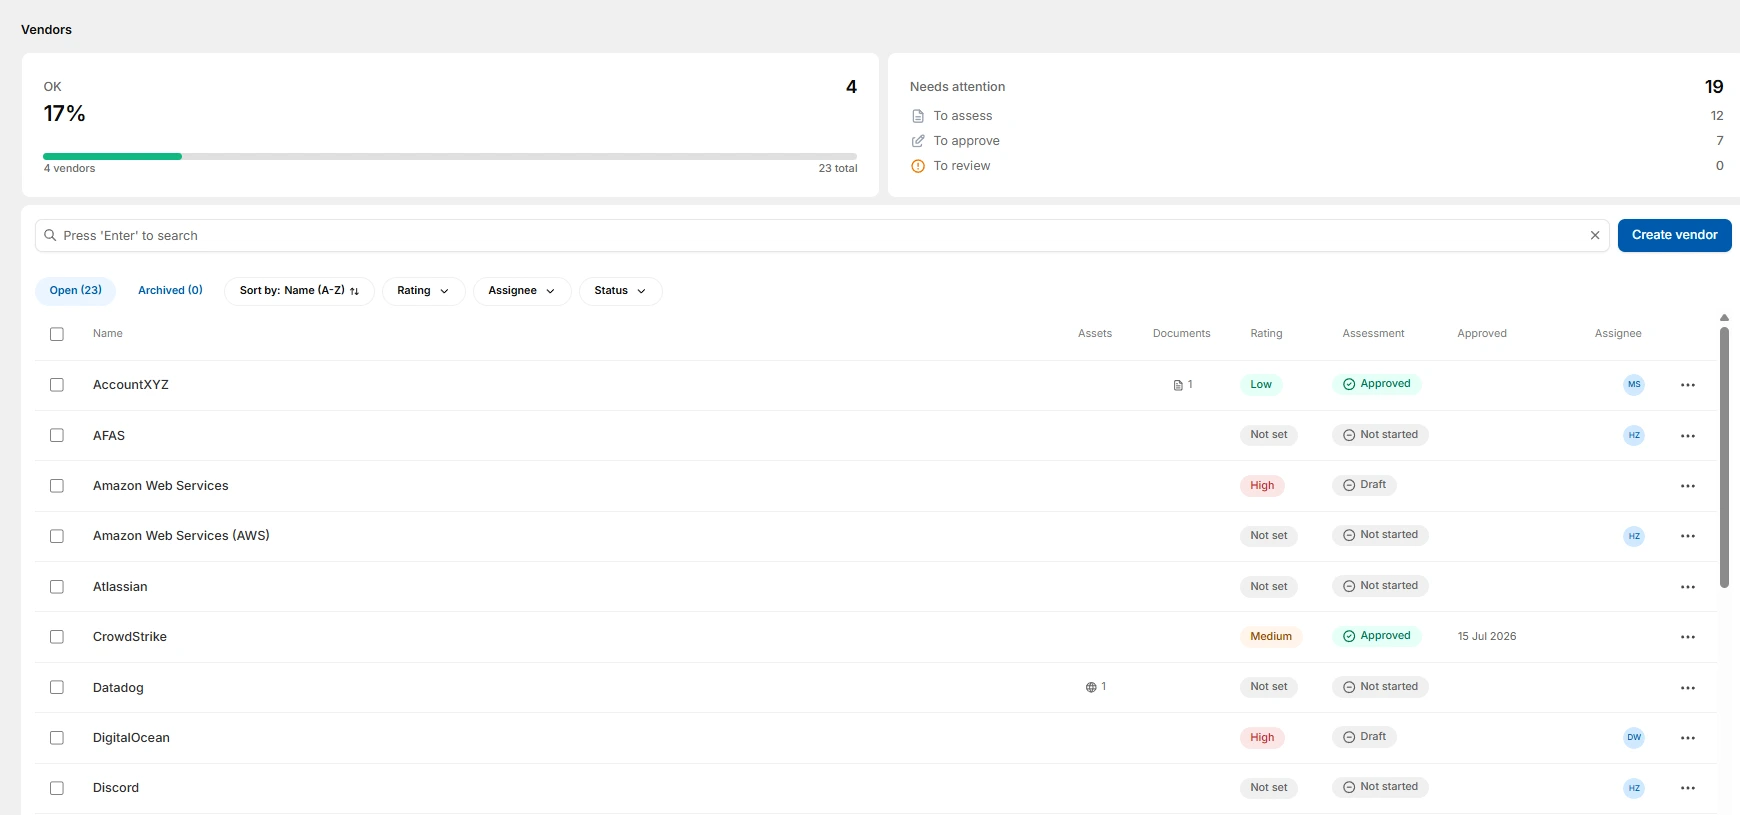
One dossier for ENSIA and your IT auditor
DigiD, Suwinet, BAG, BGT, BRO, BRP and PNIK all run through the same annual cycle. In Tidal those accountability reports build themselves from your live data, so the executive statement and the assurance report are one export.
More on controls and reportingENSIA accountability
- DigiDCurrent
- SuwinetCurrent
- BAG, BGT and BROCurrent
- BRP and PNIKCurrent
Manual or with Tidal
ENSIA accountability
Manual
A sprint every year
With Tidal
From the same evidence as the BIO
BIO controls
Manual
A spreadsheet
With Tidal
Pre-mapped with owner and status
Suppliers and outsourcing
Manual
Spread across contracts
With Tidal
Risk and agreements per supplier
Evidence current between rounds
Manual
Not included
With Tidal
Continuous tests through your integrations
BIO and ABDO together
Manual
Two sets of records
With Tidal
One set of controls
From baseline assessment to accountability, with government as the starting point
No certificate, but accountability: you set it up once and then follow the annual cycle.
Stage 1
Baseline assessment
We map your processes, systems and base registries and test them against the BIO. You see immediately where you stand and what the next accountability cycle requires.
Stage 2
Setup
Policy, risk analysis and controls go into Tidal, with templates written for public sector organisations.
Stage 3
Accountability
Your evidence is ready and keeps collecting itself through your integrations. The IT auditor and the executive board get one dossier instead of separate folders per base registry.
After that
Keeping it current
It does not stop at the report. The annual ENSIA cycle, new suppliers and changes to the standard are handled in the same system.
Connect the systems you already use
 Azure
 Entra ID
 Google Workspace
 TOPdesk
 Microsoft Sentinel
 Jira
 OVHcloud
 Scaleway
 STACKIT
 Hetzner
 AWS
- All integrations
In the public sector this is not the organisation's choice
Four frameworks that are already fixed for public sector organisations.
- BIO
- The mandatory baseline for central government, municipalities, provinces and water authorities
- ENSIA
- Annual accountability for DigiD, Suwinet and the base registries
- ABDO
- Security requirements for organisations carrying out work for the Ministry of Defence
- NIS2
- The Dutch Cybersecurity Act brings a duty of care and a reporting duty for public sector organisations
Frequently asked questions
Yes. The BIO is the established baseline for central government, municipalities, provinces and water authorities. Unlike ISO 27001 it is not about a certificate, but about demonstrably complying and accounting for it.
The BIO follows the structure of ISO 27002 and is the public sector reading of it. If you have already implemented ISO 27001 you will recognise most of the controls; on top of that, the BIO fixes the minimum level you have to reach.
The BIO says what you have to arrange, ENSIA is the annual accountability for it, with its own control frameworks for DigiD, Suwinet and the base registries. In Tidal you set up the BIO once and use the same evidence for the ENSIA cycle.
When you carry out work for the Ministry of Defence involving classified information. ABDO then adds requirements for personnel, physical security and information security, on top of what you already do for the BIO or ISO 27001.
That depends on your size and what is already in place. After the baseline assessment you see per control what is left to do, so you know what the next accountability round needs. After that you follow the annual cycle in the same system.