NEN 7510 and GDPR for healthcare organisations
One platform for NEN 7510, ISO 27001 and your GDPR accountability. Healthcare templates, evidence that collects itself and one file for your auditor and the regulator.
- NEN 7510 and ISO 27001 on one set of controls
- Suppliers and chain partners in view
- Built and hosted in the EU
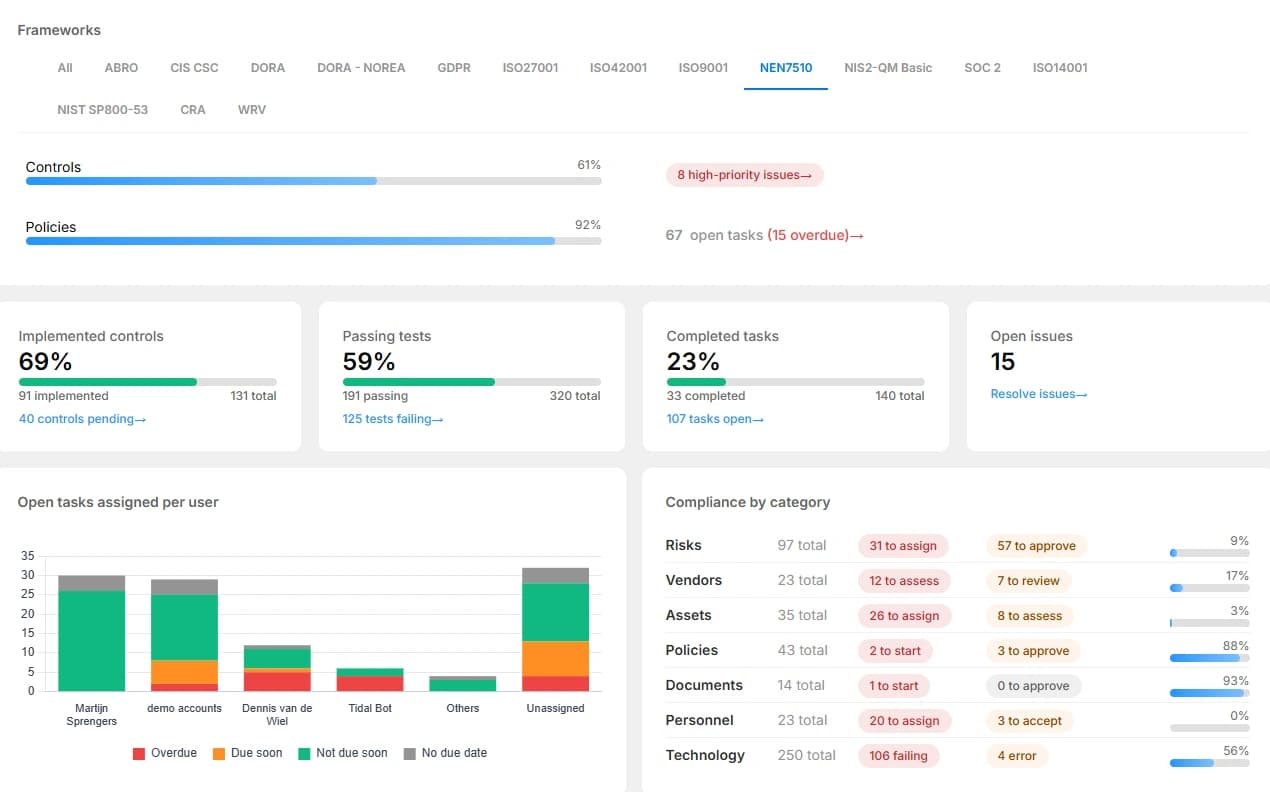
What healthcare organisations achieve with Tidal
- 50+
- Audits passed by our customers, a 100% pass rate
- 0-2
- Findings on average at the certification audit
- 35+
- Frameworks on one set of controls, including NEN 7510 and ISO 27001
Why NEN 7510 stalls in healthcare
The standard is clear. Healthcare organisations get stuck on execution: a long supply chain, policies that do not keep up and evidence only gathered at audit time.
Many parties touch patient data
From EHR vendor to lab links, the overview sits in separate contracts. A missing data processing agreement only surfaces at the audit.
Policies on the shelf
Written for the first certification and not updated since. The auditor checks whether they match how you work today.
Evidence spread across folders
Access rights, logging and backups are only gathered when the auditor asks. That takes weeks and shows a single moment.
Quiet after the certificate
Without a steady rhythm of checks and reviews, the organisation nearly starts over at recertification.
How healthcare organisations use Tidal
From the controls to the file the regulator asks for, always from the same source.
Every healthcare-specific control in one place
NEN 7510 builds on ISO 27001 and adds requirements on patient data, access and logging. In Tidal those controls are pre-mapped, each with an owner and a status, so you never start from a blank page.
More on NEN 7510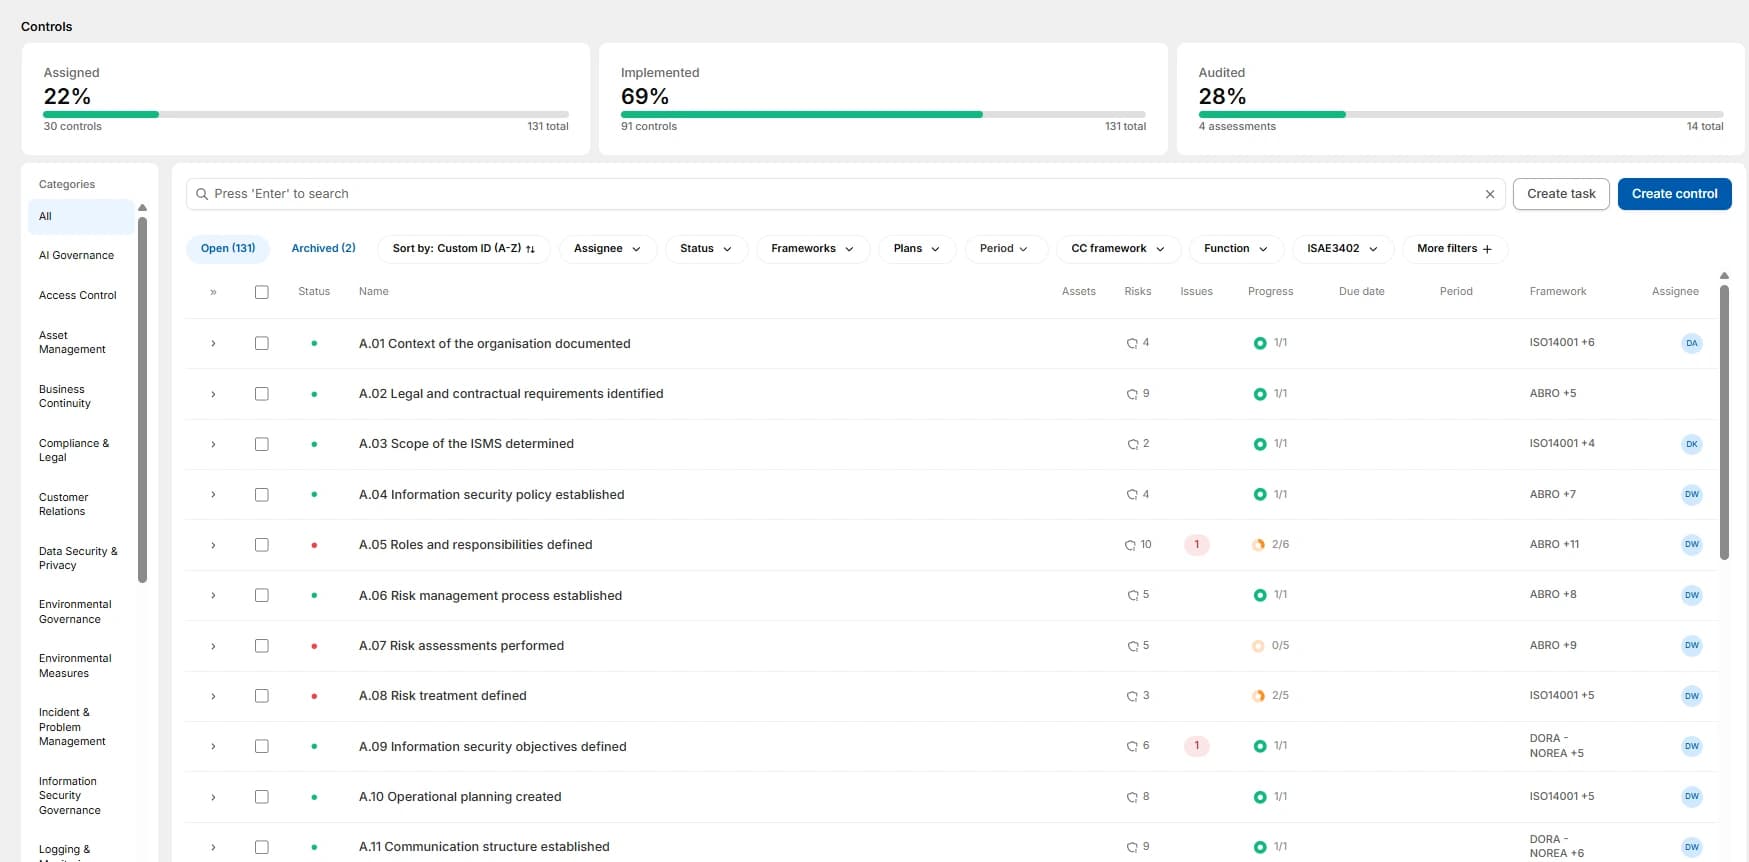
Evidence for your controls collects itself
Connect Azure and Entra ID, Google Workspace and the rest of your tooling. Tidal collects the evidence automatically and attaches it to the right control. Where there is no integration, as with many EHR systems, you record evidence with an expiry date.
See all integrations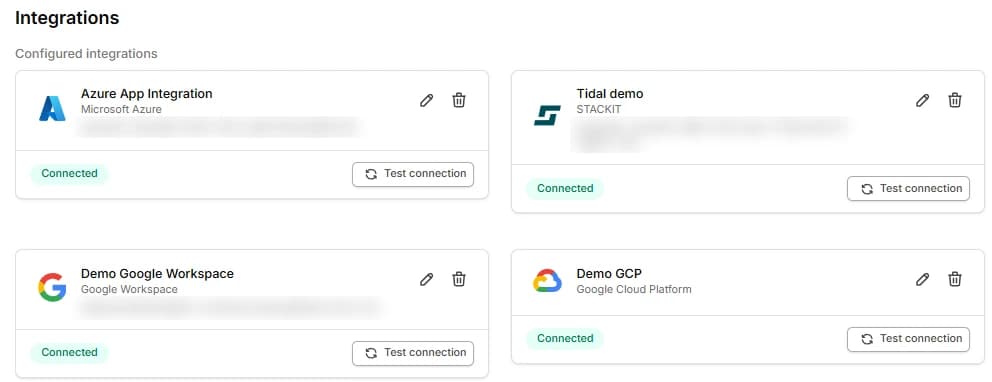
Chain partners in view, including their risk
From your EHR vendor to scheduling tools and lab links, you remain responsible for every party that touches patient data. Tidal tracks the risk per supplier and whether the data processing agreement is in place.
More on vendor management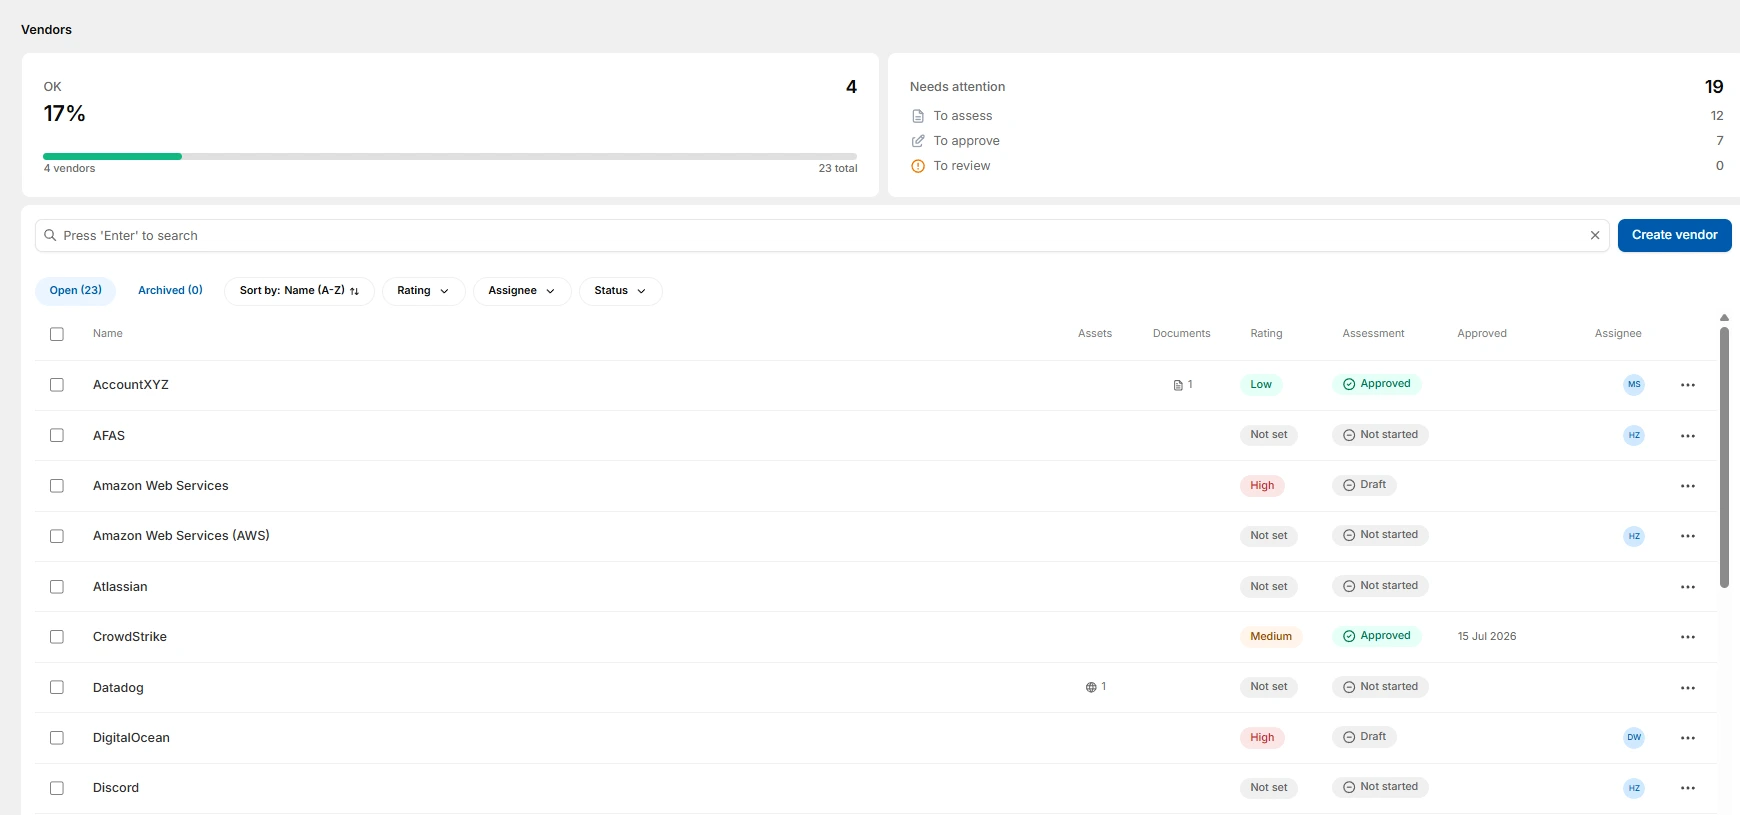
One file for your auditor and the regulator
Your Statement of Applicability, risk assessment and management review build themselves from live data. When the regulator asks how you control access to records, the answer is ready, including who changed what and when.
More on controls and reportingNEN 7510 audit dossier
- Statement of ApplicabilityCurrent
- Care process risk analysisCurrent
- Management reviewCurrent
- Internal audit reportCurrent
Manual or with Tidal
Suppliers and chain partners
Manual
A list in a spreadsheet
With Tidal
Risk and data processing agreement per party
NEN 7510 controls
Manual
An empty template
With Tidal
Pre-mapped with owner and status
Collecting evidence
Manual
Manually per control
With Tidal
Automatic where an integration exists
Evidence current between audits
Manual
Not included
With Tidal
An expiry date per piece of evidence
Combining with ISO 27001
Manual
A separate project
With Tidal
One set of controls
The journey: a median of 13 weeks from kickoff to certificate
A realistic path, not a promise of compliance in a few days. You always see what is expected of your team.
Day 1
Setup
Connect your tooling and see straight away which NEN 7510 controls are already in place.
Week 1-2
Plan
We map your care processes, systems and chain partners and set the scope for NEN 7510.
Week 3-11
Implement
Policies, risk assessment and controls go into Tidal, with templates written for healthcare.
Week 12-13
Certify
An independent, accredited certification body carries out the audit. Your evidence is ready in one file.
After
Maintain
Annual audits, new chain partners and changes to the standard run in the same system.
Connect the systems you already use
 Azure
 Entra ID
 Google Workspace
 TOPdesk
 Microsoft Sentinel
 Jira
 AWS
 Google Cloud
 OVHcloud
 Scaleway
 Hetzner
- All integrations
“The pace genuinely surprised me. I hear from others that it usually takes six months to a year in an implementation like this.”
Ties Verberne
Co-founder, Aivory
In healthcare this is not a board decision
Four places where information security in healthcare is already written down.
- GDPR art. 32
- Appropriate technical and organisational measures
- Begz
- Dutch healthcare providers must meet NEN 7510 when processing data electronically
- Health inspectorate
- Supervision of information security as part of good care
- NIS2
- Larger healthcare providers fall under the duty of care of the Dutch Cybersecurity Act
Frequently asked questions
Certification is not a legal requirement, but meeting NEN 7510 is. The Dutch decree on electronic data processing by healthcare providers (Begz) prescribes the standard for processing patient data. In practice insurers, chain partners and tenders increasingly ask for the certificate.
NEN 7510 is the Dutch healthcare-specific reading of ISO 27001. The structure is the same; NEN 7510 adds requirements around patient data, access to records and logging of who viewed what. If you already have ISO 27001, you are not starting over.
Across our customers the median is 13 weeks from kickoff to certificate. How long it takes for you depends on your size, the number of chain partners and what is already in place.
Tidal connects to the systems your evidence comes from, such as Azure and Entra ID and Google Workspace. Most EHR systems have no direct integration. There you record evidence manually with an expiry date, so it does not go stale unnoticed.
The certificate is valid for three years, with annual surveillance audits. Tidal keeps your evidence current in between, so every audit starts with a file that is already in order.