NEN 7510 certification for healthcare organisations and healthcare software

The Dutch standard for information security in healthcare. Tidal Control sets up your NEN 7510 measures on the same base as ISO 27001, collects evidence automatically and prepares you for the audit by the certification body.

  • 131 clauses pre-mapped
  • Together with ISO 27001
  • NEN 7512 and 7513 included
  • Built in the EU
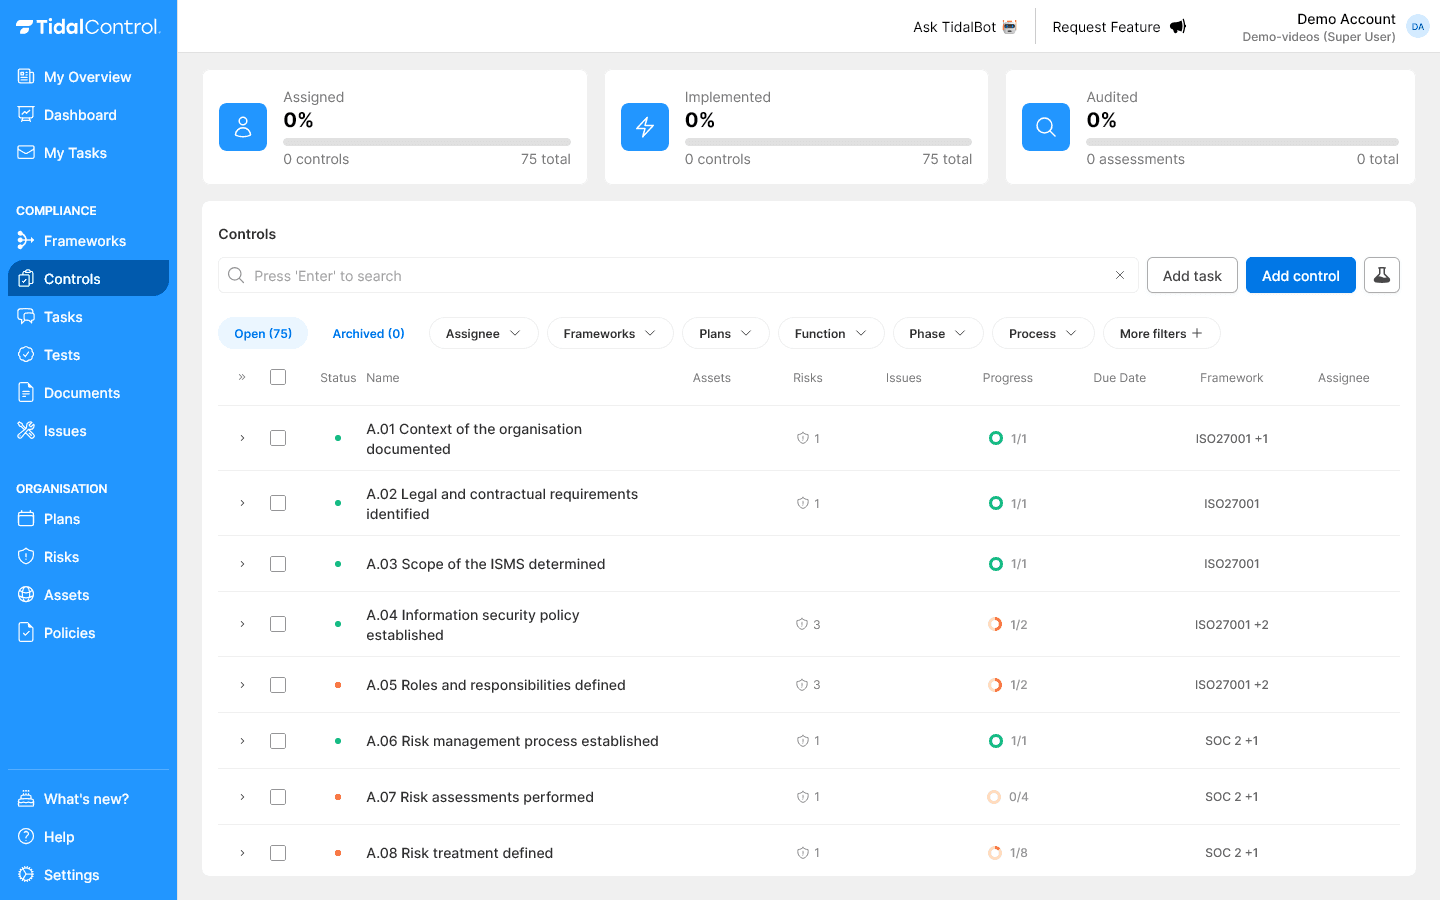
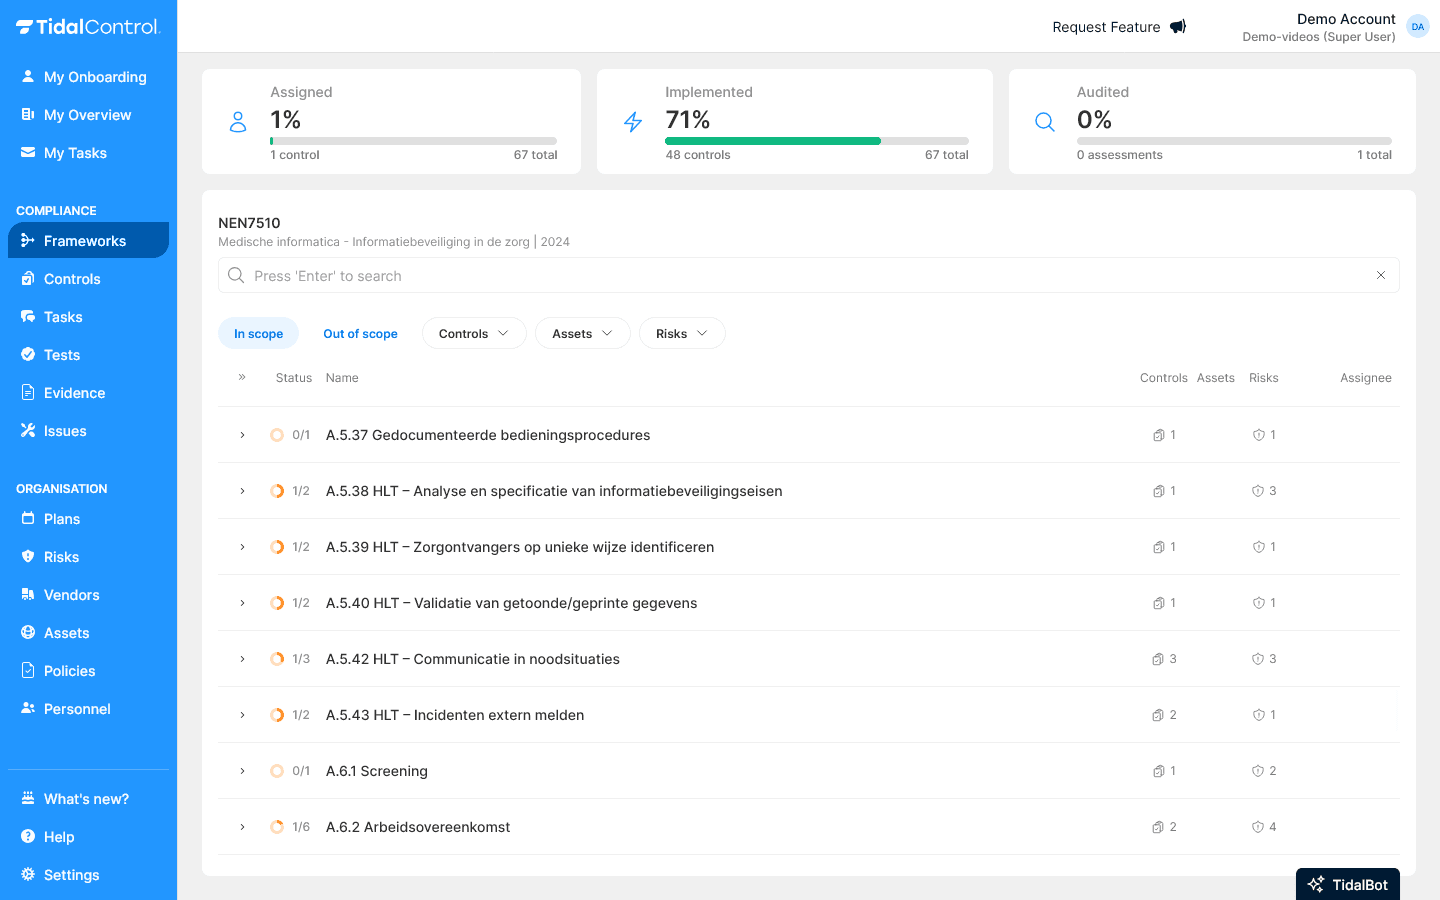
The NEN 7510 overview in Tidal Control with the status of measures and evidence

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From baseline to NEN 7510 certificate

How long it takes depends on your size and what is already in place. Tidal shows what is expected of your team at each phase, and it does not stop at the certificate.

  1. Step 1

    Baseline

    Scope, care processes and a gap analysis against NEN 7510.

  2. Step 2

    Implementation

    Policies, measures and evidence filled in with templates.

  3. Step 3

    Internal audit

    Self-assessment and management review.

  4. Step 4

    Stage 1 audit

    Documentation review by the certification body.

  5. Step 5

    Stage 2 and certificate

    Implementation audit and your NEN 7510 certificate.

  6. After that

    Audits and sparring

    Your annual audits prepared, and a sparring partner for new requirements.

How Tidal helps with the NEN 7510 requirements

NEN 7510 consists of management system requirements and a set of controls, with NEN 7512 and NEN 7513 alongside. Tidal sets them up for you, with an owner, policy and evidence for each measure.

clauses mapped to ISO 27001
131clauses mapped to ISO 27001
audits passed, 100% pass rate
50+audits passed, 100% pass rate

The NEN 7510 family

  • NEN 7510-1

    Management system

    Scope, risk analysis, roles and the cycle of plan, do and improve.

  • NEN 7510-2

    Controls

    The controls from ISO 27002, extended with requirements for healthcare.

  • NEN 7512

    Data exchange

    Trust when exchanging data with other parties.

  • NEN 7513

    Logging

    Recording who viewed or changed which record.

NEN 7510 in brief

NEN 7510 is the Dutch standard for information security in healthcare, based on ISO 27001 and ISO 27002. Healthcare providers are bound by it through the Besluit elektronische gegevensverwerking door zorgaanbieders, together with NEN 7512 and NEN 7513. For healthcare software suppliers and others that process patient data, it is usually a requirement from their customers. A certificate shows that an independent auditor has checked it.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • Meeting the legal requirement for care providers
  • Access to healthcare customers that require certification
  • Trust from patients and partners in the chain
  • Less chance of data breaches and incidents
  • Work that also counts towards ISO 27001

How you work on NEN 7510 in Tidal

From risk analysis to supplier management: every part of your NEN 7510 ISMS in one place.

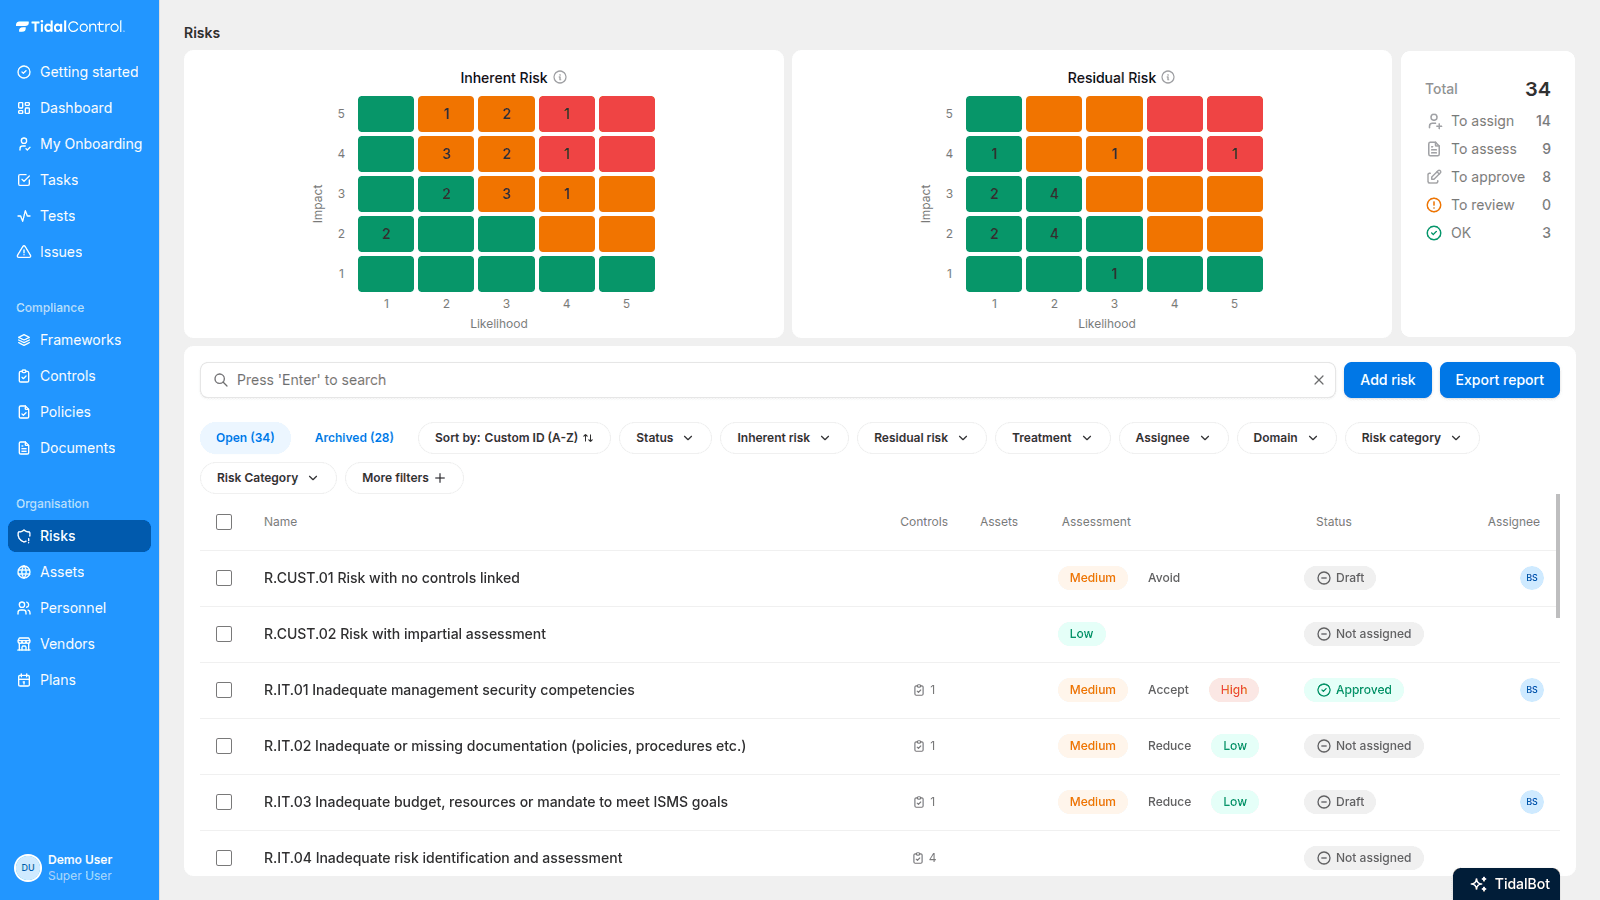
Risk assessment

Risk assessments that work

Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

Risk assessment in Tidal ControlRisk assessments that work
Controls management

Control management that works your way

Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

Controls management in Tidal ControlControl management that works your way

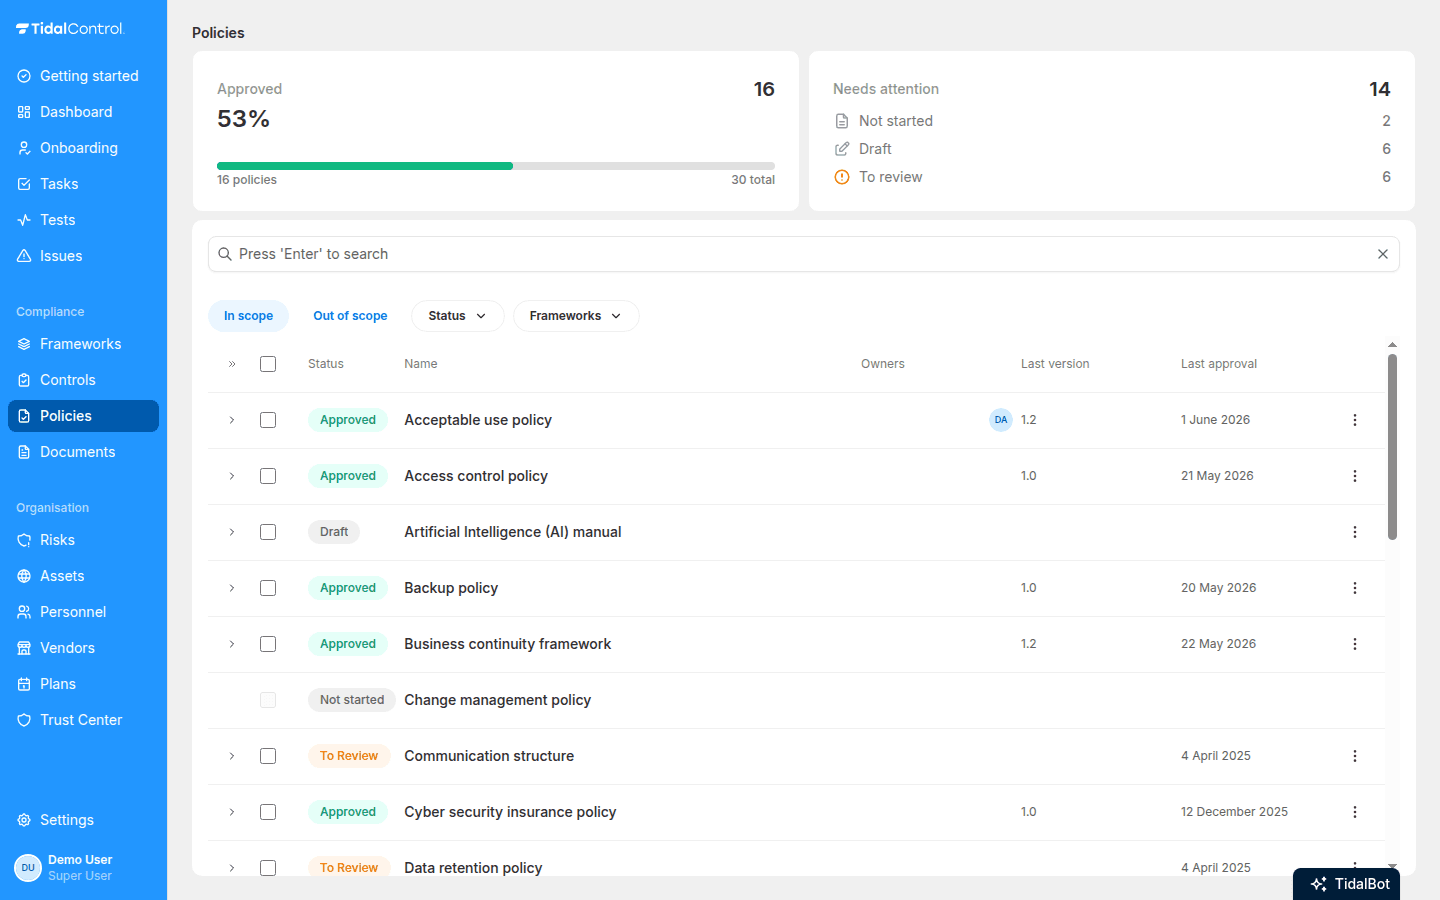
Policy center

Policies without the hassle

Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

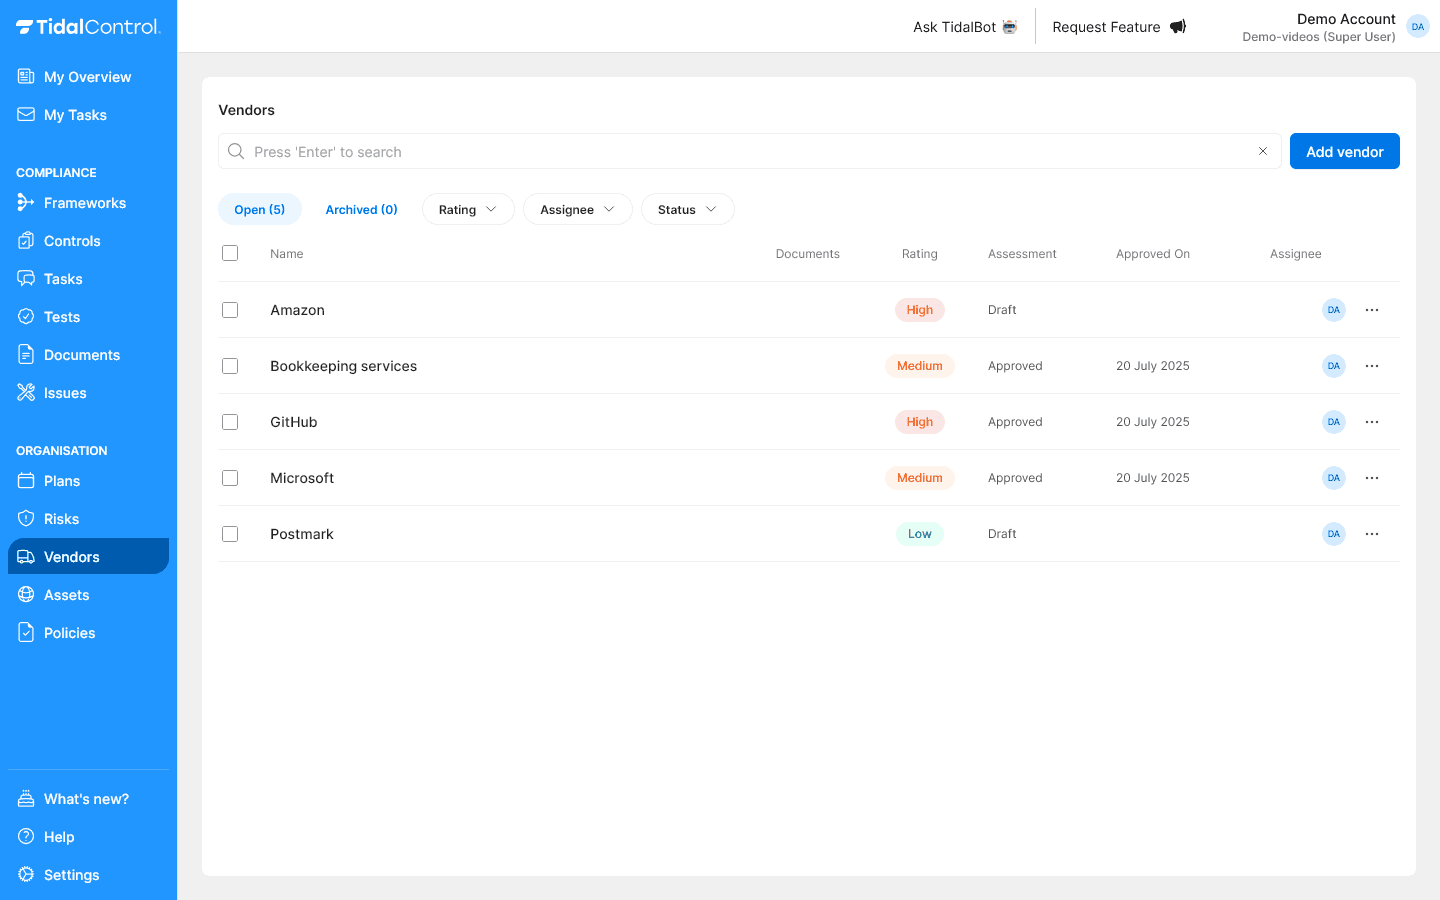
Vendor management

Partners that handle patient data in view

Assess the risk of each supplier, record data processing agreements and arrangements and schedule a reassessment. You see which parties touch patient data.

Vendor management in Tidal ControlPartners that handle patient data in view

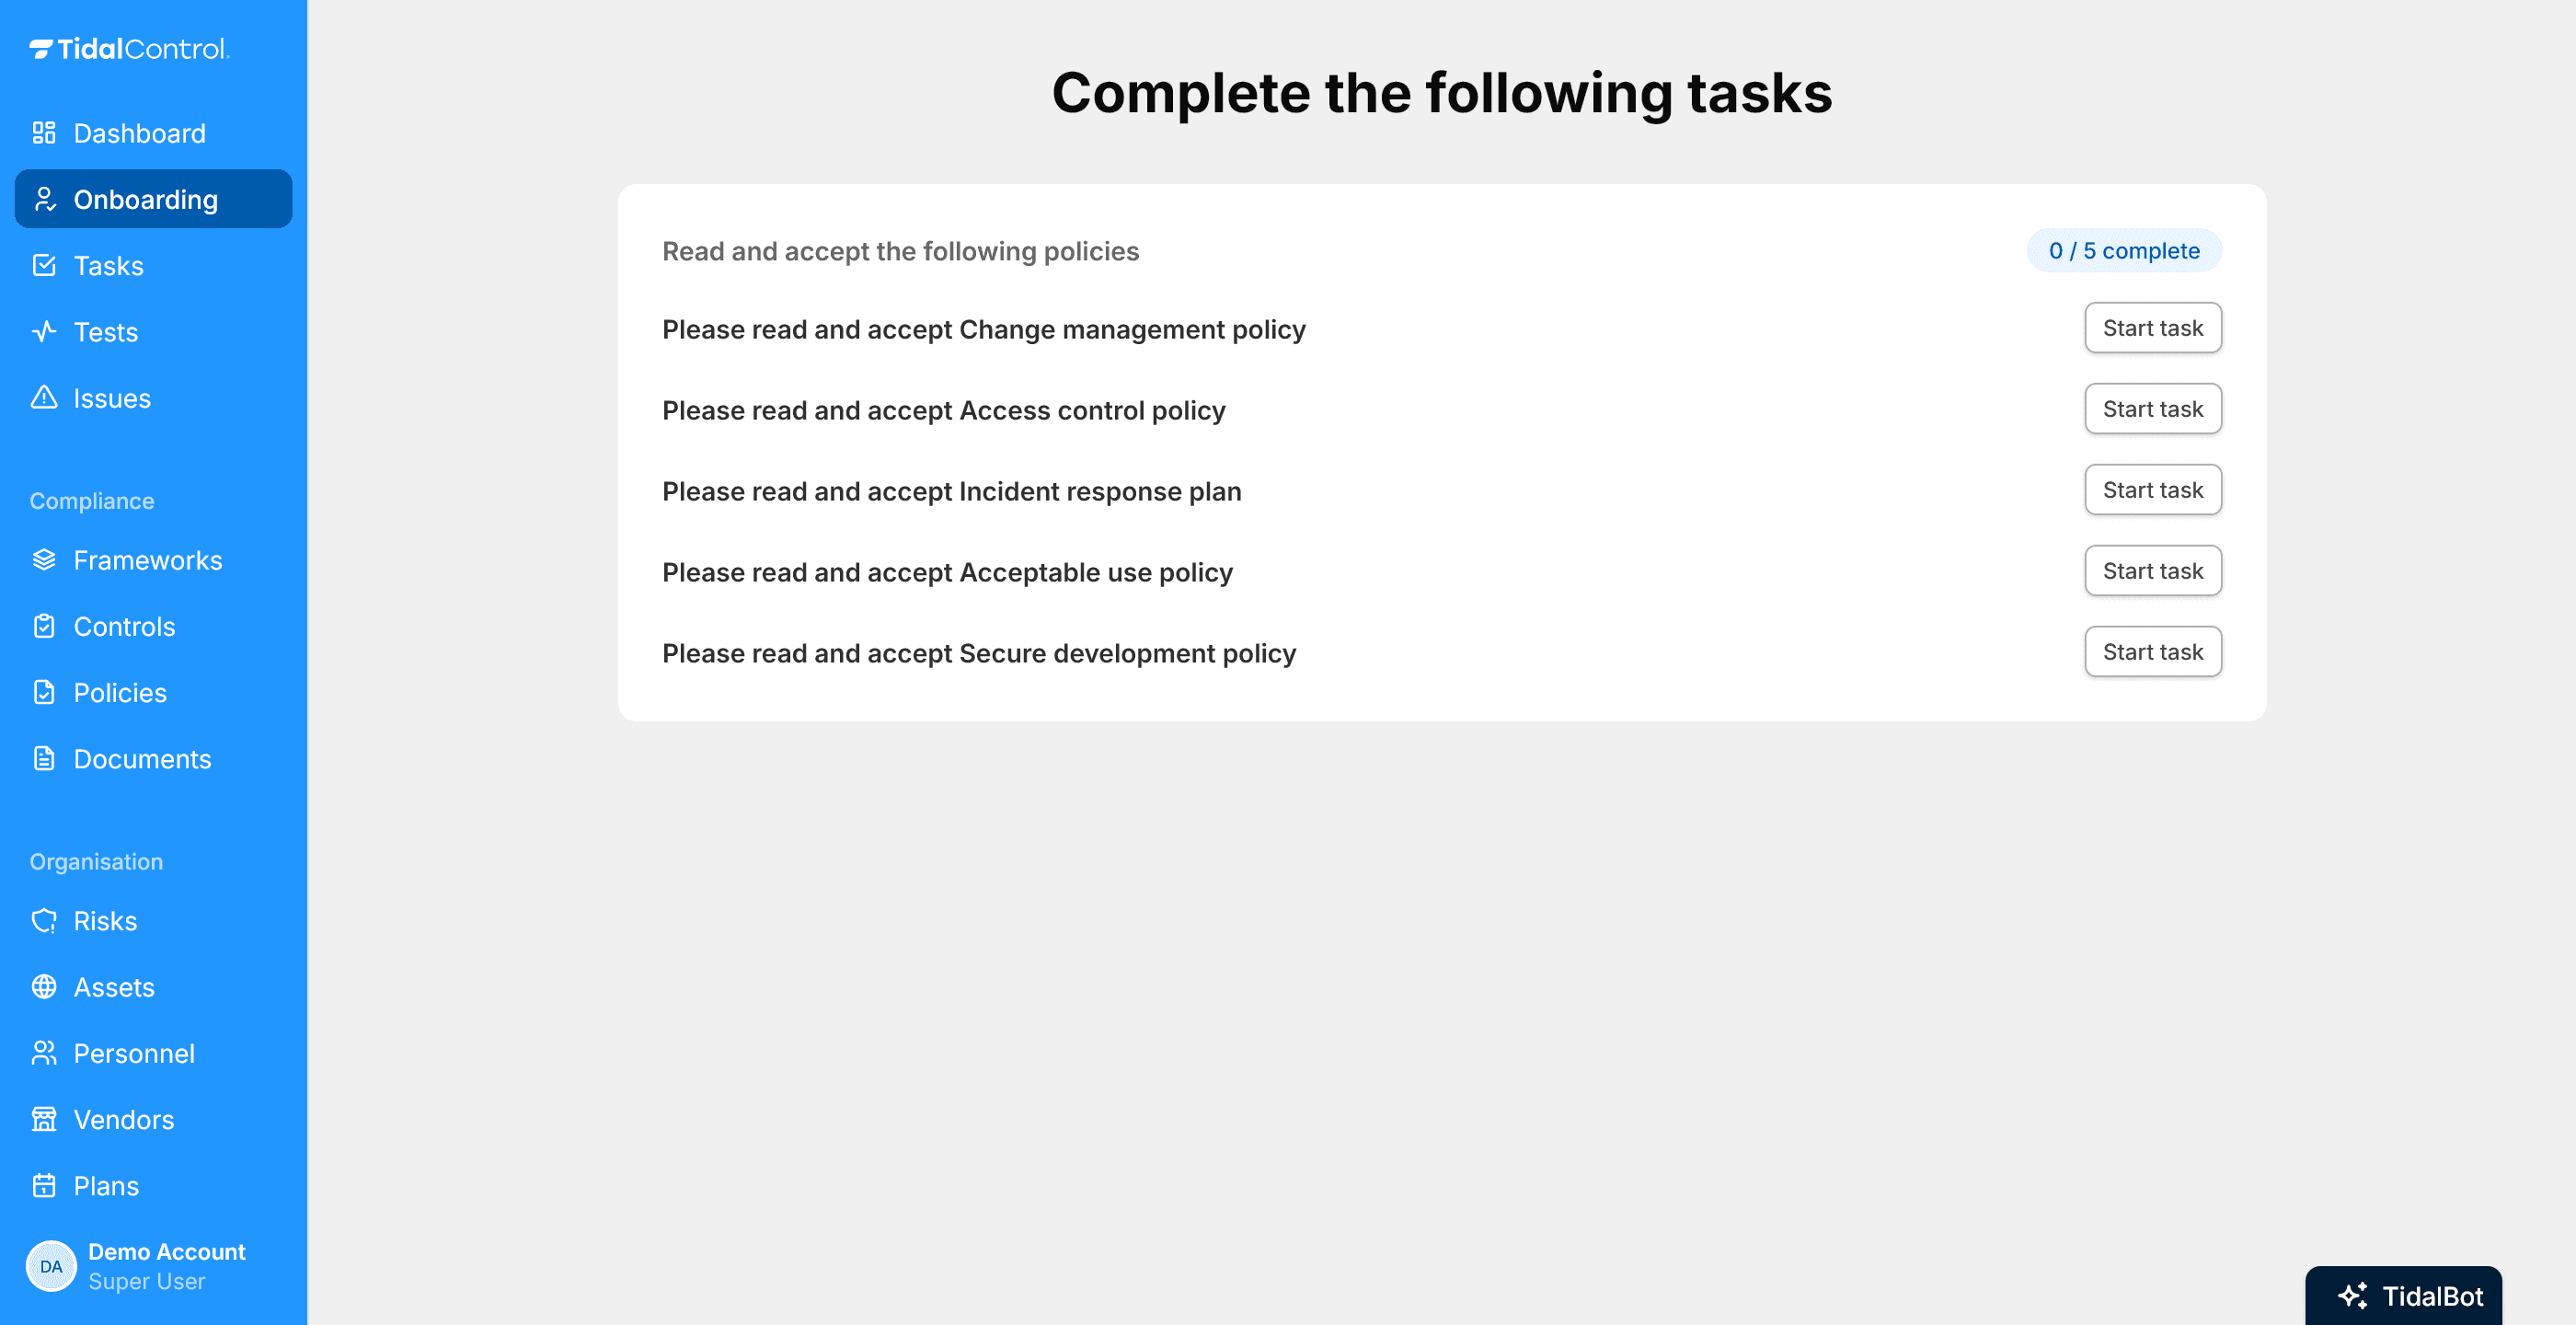
Personnel & onboarding

Employee compliance without the spreadsheet

The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

Issues management

Track and resolve issues - all in one place

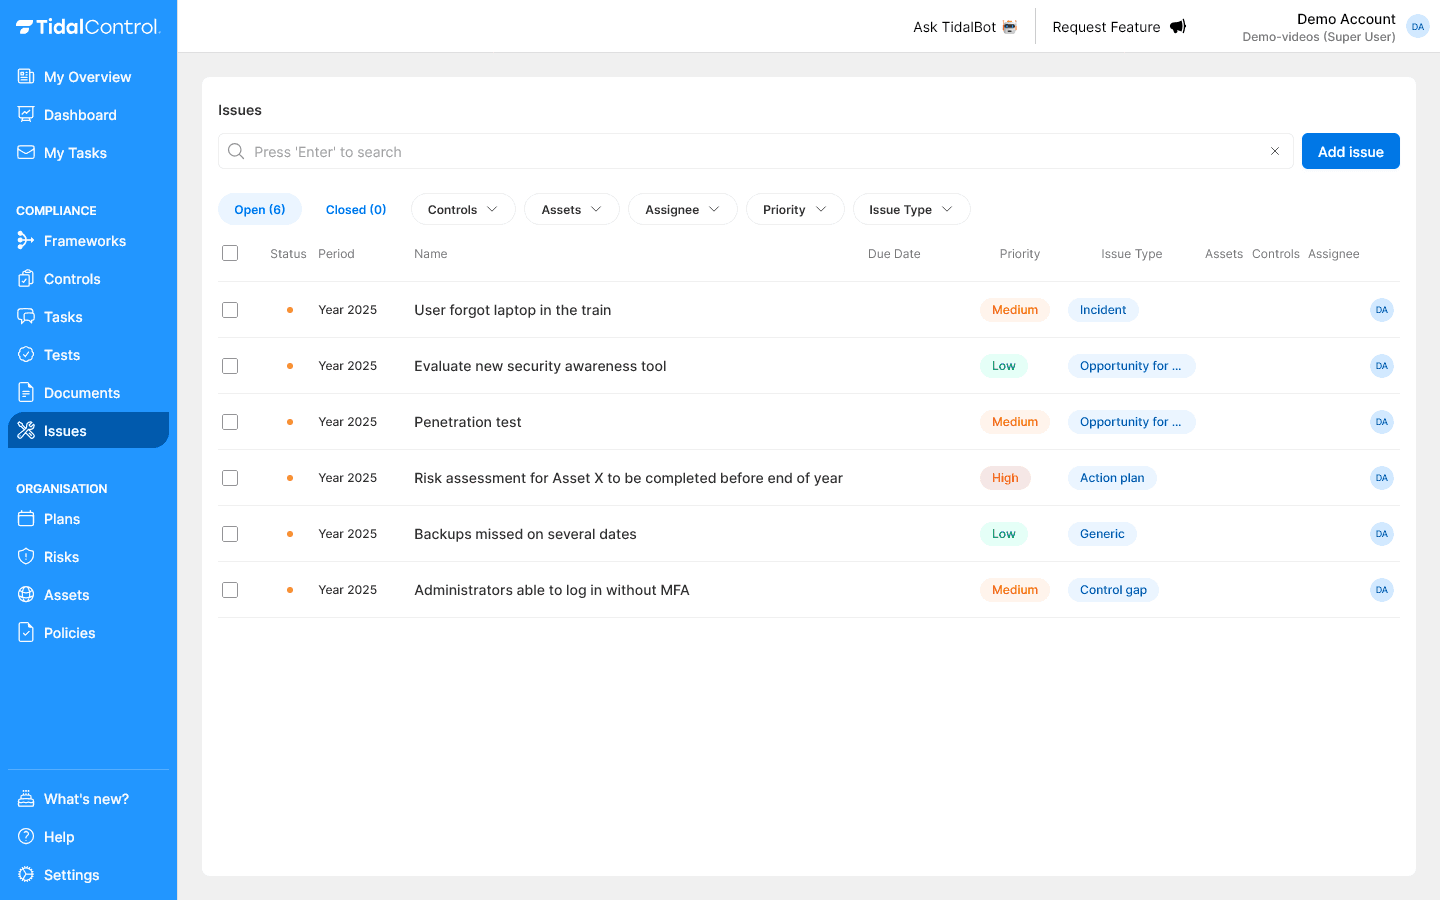
Simplify issue management with a centralised system that handles everything from audit findings to improvement opportunities. Keep your team aligned and ensure nothing gets missed with clear ownership, priorities, and automated tracking.

Issues management in Tidal ControlTrack and resolve issues - all in one place

Integrations

Automation makes life more fun!

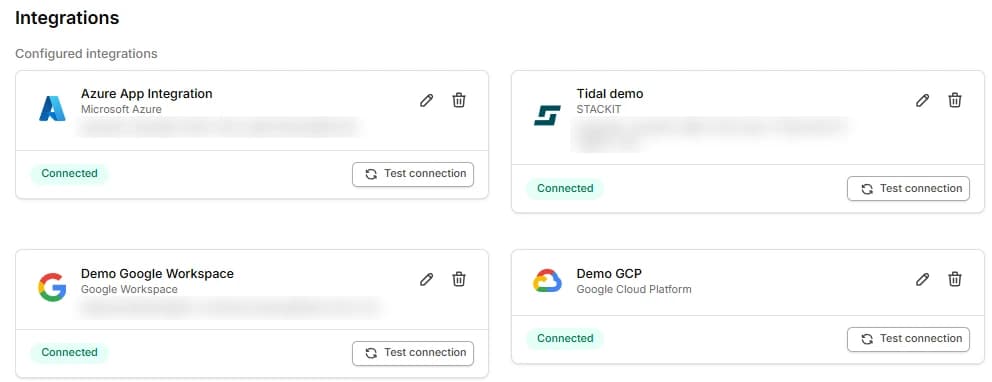
Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • Managing measures

    Manual

    A spreadsheet per standard

    With Tidal

    Pre-mapped with owners

  • Collecting evidence

    Manual

    Manual screenshots per measure

    With Tidal

    Automatically from your tools

  • NEN 7510 and ISO 27001

    Manual

    Two projects side by side

    With Tidal

    One set of measures, evidence once

  • Partners in the chain

    Manual

    Processing agreements in a folder

    With Tidal

    Risk per supplier with reassessment

  • Audit preparation

    Manual

    Weeks of scrambling before the audit

    With Tidal

    Always audit-ready

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

See all success stories

Integrate with your existing tools

NEN 7510 certification and audit

You get a NEN 7510 certificate from a certification body accredited for it. The audit has two stages: in Stage 1 the auditor looks at your documentation, such as scope, risk analysis and policies. In Stage 2 they check whether the measures work in practice.

After that comes a surveillance audit every year and a recertification every three years. Evidence collected just before the audit stands out quickly: auditors look at follow-up over time.

If audit preparation is part of your day-to-day management, the audit is a snapshot of how you already work.

Frequently asked questions

NEN 7510 is the Dutch standard for information security in healthcare. Healthcare providers are bound by it in law: Article 3 of the Dutch decree on electronic data processing by healthcare providers (Besluit elektronische gegevensverwerking door zorgaanbieders) requires them to follow NEN 7510, 7512 and 7513. For others that process patient data, such as healthcare software suppliers, it is usually a contractual requirement from their customers.

NEN 7510 is based on ISO 27001 but adds healthcare-specific requirements and guidance. If you already have ISO 27001, implementing NEN 7510 involves adding sector-specific controls. Our platform manages both standards efficiently.

NEN 7510 is the base: an information security management system with controls for healthcare. NEN 7512 covers trust when exchanging data with other parties. NEN 7513 covers logging: recording who viewed or changed which record. Care providers have to follow all three. In Tidal you manage them in the same system.

An independent, recognised certification body in the healthcare sector, using accredited auditors. Tidal does not certify you itself. In healthcare that matters: an auditor with no stake in the outcome tests whether patient data is demonstrably protected. Tidal makes sure your evidence is ready.

Two parts. The audit is bought from a certification body accredited for NEN 7510 that charges per audit day, with the number of days following from your size and scope. On top of that, implementation takes your own team's time: risk analysis, controls, policy and evidence. If you have already done that work for ISO 27001 it saves a lot, because both standards build on the same ISO 27002 basis. There is no fixed rate, so ask for a quote based on your scope.

Partly. NEN 7510 covers the security of patient data, which is a large part of what the GDPR asks in appropriate measures. Other GDPR duties, such as a record of processing, the rights of data subjects and processing agreements, come on top. In Tidal you manage the GDPR next to NEN 7510, with the same measures where they overlap.

Tidal sets up the NEN 7510 requirements for you, with policy templates, a risk analysis and an owner and evidence for each measure. Evidence from your own tools is collected automatically. Our customers have passed more than 50 audits, with 0 to 2 findings on average. The audit itself is done by an independent certification body.