Solutions
The European alternative to Vanta and Drata
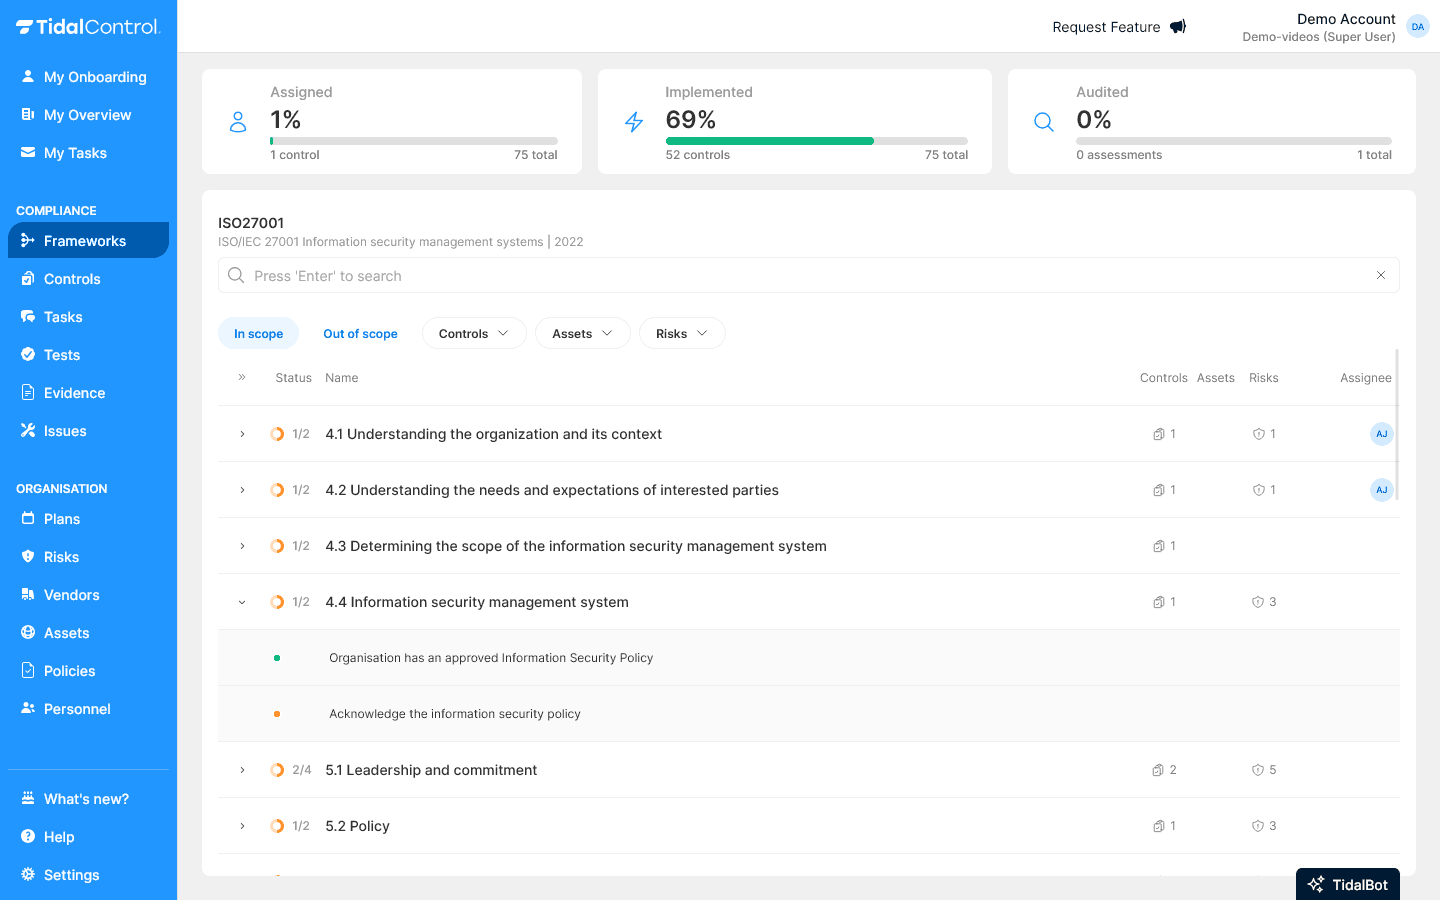
Tidal Control is built and hosted in Europe. It covers more than 30 frameworks, collects evidence from the cloud and development tools your team already runs, and brings accredited auditors to the certification itself.
If you need NIS2 or DORA next to ISO 27001 or SOC 2, one platform handles all of them and your compliance data never leaves the EU.
What EU-based means here
Data residency is the starting point. The rest is what European buyers usually end up asking about twice.
Your data stays in the EU
The platform is built and hosted in Europe, so evidence, policies and risk records stay under EU jurisdiction.
NIS2 and DORA are first-class frameworks
Both sit next to ISO 27001, SOC 2, GDPR and ISO 42001, and controls are shared across the frameworks you run, so overlapping requirements are implemented once.
Accredited auditors, not a badge
Certification is carried out by accredited auditors. More than 50 audits have passed this way, averaging 0-2 findings.
Evidence collected automatically
Over 300 tests run against Microsoft, AWS, Google Cloud, Jira and the rest of your stack, so evidence is gathered continuously instead of the week before an audit.
The frameworks behind this question
European buyers rarely need one framework on its own. These four are the combination that comes up most.
NIS2
The EU directive on network and information security, and the reason many organisations start looking for a European platform at all.
DORA
Digital operational resilience for financial entities and their ICT suppliers, including incident reporting and third-party risk.
ISO 27001
The information security baseline most NIS2 and DORA programmes are built on.
SOC 2
Still the report your American customers ask for, run from the same platform as your EU obligations.
Integrate with your existing tools


Testimonials
What our customers say
With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Frequently asked questions
Most teams that find this page are comparing the three. What Tidal Control adds is a European base: the platform is built and hosted in the EU, NIS2 and DORA sit alongside ISO 27001 and SOC 2, and accredited auditors carry out the certification. Whether it replaces what you run today depends on which frameworks you need and where your data has to live, which a demo settles in half an hour.
In the EU. The platform is built and hosted in Europe, and your controls, risks, policies and evidence stay under EU jurisdiction.
More than 30, including ISO 27001, SOC 2, GDPR, NIS2, DORA, ISO 9001, ISO 42001 and NEN 7510. Controls are shared across frameworks, so a requirement that appears in three of them is implemented once.
Yes. SOC 2 runs on the same platform as your EU obligations, so an American customer asking for SOC 2 and a European regulator asking for NIS2 are both served from one set of controls.
About three months on the standard path: one day of setup, two weeks of planning, nine weeks of implementation and two weeks for certification.
Yes. Audits are carried out by accredited auditors, and the platform assembles the evidence they ask for.