NIST SP 800-53 controls demonstrable per baseline

The US catalogue of security and privacy controls, the base for FedRAMP and many government contracts. Tidal Control sets up the Revision 5 controls per baseline, records tailoring and keeps evidence for the assessor.

  • Revision 5, 20 families
  • Low, moderate, high baselines
  • Together with ISO 27001
  • Built in the EU
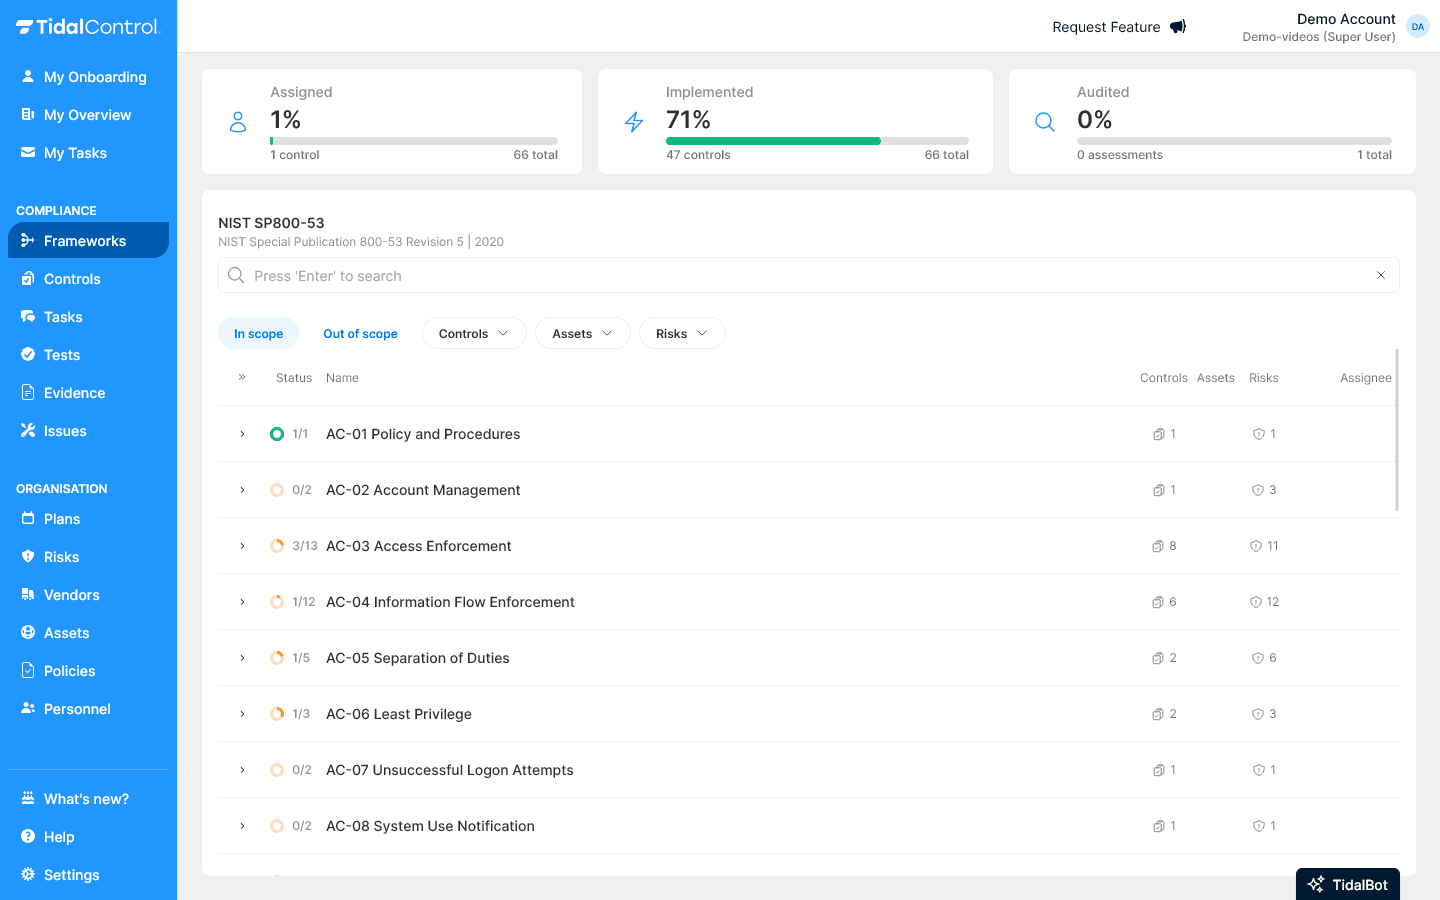
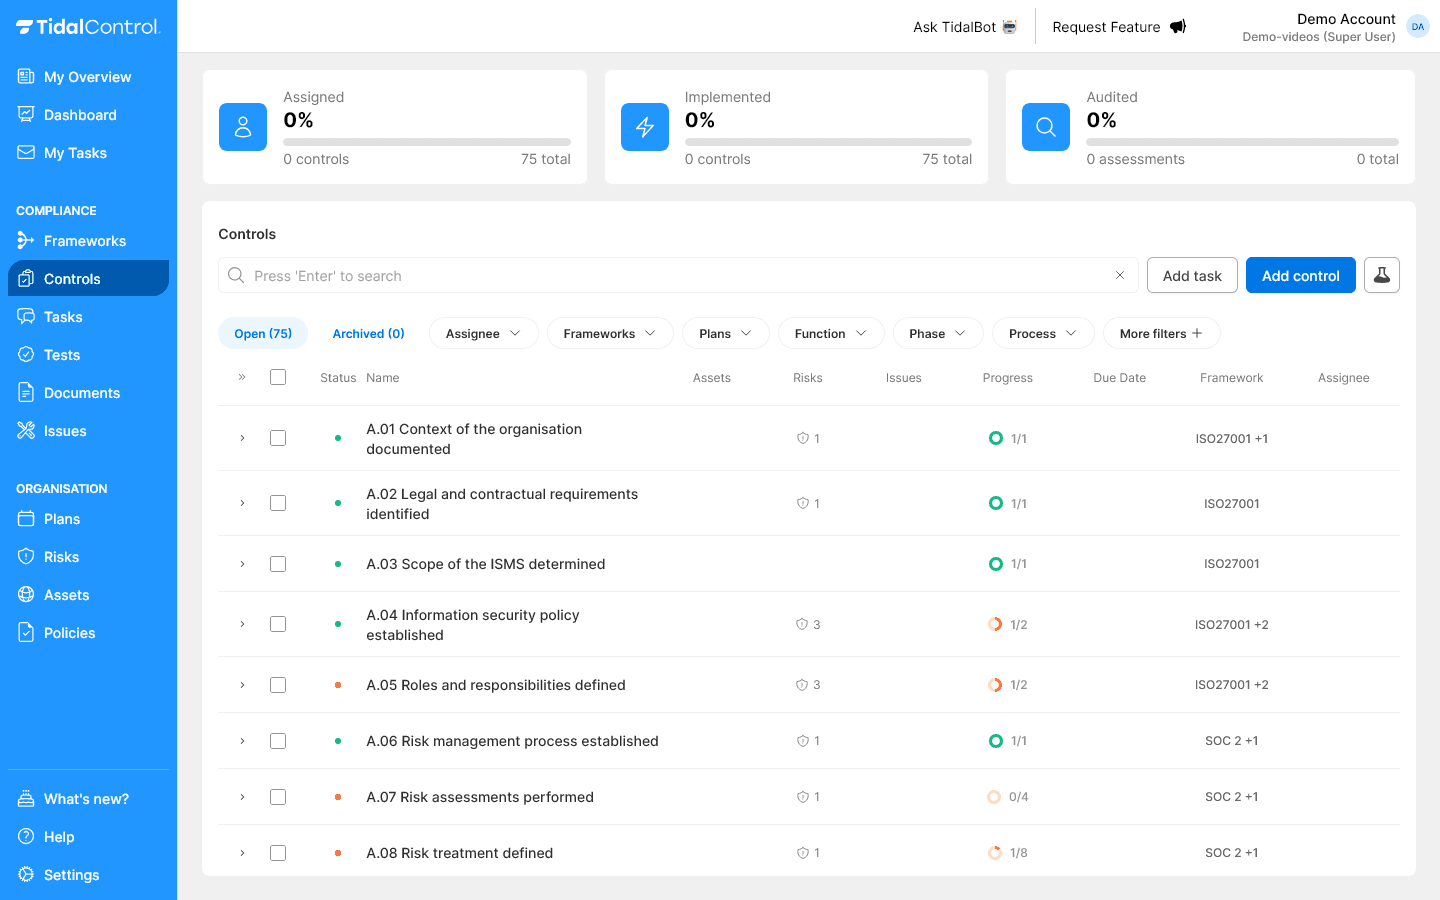
The NIST SP 800-53 overview in Tidal Control with the status of controls and evidence

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From categorisation to assessment

How long it takes depends on your baseline and what is already in place. Tidal shows what is expected of your team at each step.

  1. Step 1

    Categorisation

    Classifying the system by impact: low, moderate or high.

  2. Step 2

    Baseline and tailoring

    Choosing the controls and adapting them to your system.

  3. Step 3

    Implementation

    Controls, policies and evidence recorded.

  4. Step 4

    Assessment

    Checking that the controls work, and following up findings.

  5. Step 5

    Authorisation

    Evidence ready for the assessor and the decision to operate.

  6. After that

    Continuous monitoring

    Controls monitored and findings followed up, and a sparring partner for changes.

How Tidal helps with the control families

Revision 5 has twenty control families, from access control to the supply chain. Tidal groups them into six and sets them up for you, with an owner, policy and evidence for each control.

control families
20control families
baselines: low, moderate, high
3baselines: low, moderate, high

NIST SP 800-53 Rev. 5

  • AC, IA

    Access and identity

    Who has access to which systems, and how you check it.

  • AU

    Audit and logging

    Recording, keeping and reviewing events.

  • CM, SI

    Configuration and integrity

    Secure configuration, patching and protection against malware.

  • IR, CP

    Incidents and continuity

    Handling incidents and being able to recover systems.

  • RA, CA, PM

    Risk and assessment

    Assessing risks, testing controls and running the programme.

  • SR, PT

    Supply chain and privacy

    Supply chain risks and the processing of personal data.

NIST SP 800-53 in brief

NIST Special Publication 800-53 is a catalogue of security and privacy controls from the US National Institute of Standards and Technology. US federal agencies and their contractors must work with it, and FedRAMP builds on it. Outside that, organisations use the catalogue as a detailed reference. Revision 5 is the current version.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • Access to US government contracts
  • A base for FedRAMP
  • A detailed, recognised control set
  • Well-founded choices per system
  • Work that also counts towards ISO 27001 and the NIST CSF

How you work on NIST SP 800-53 in Tidal

From risk assessment to continuous monitoring: your controls per baseline in one place.

Controls management

Control management that works your way

Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

Controls management in Tidal ControlControl management that works your way
Risk assessment

Risk assessments that work

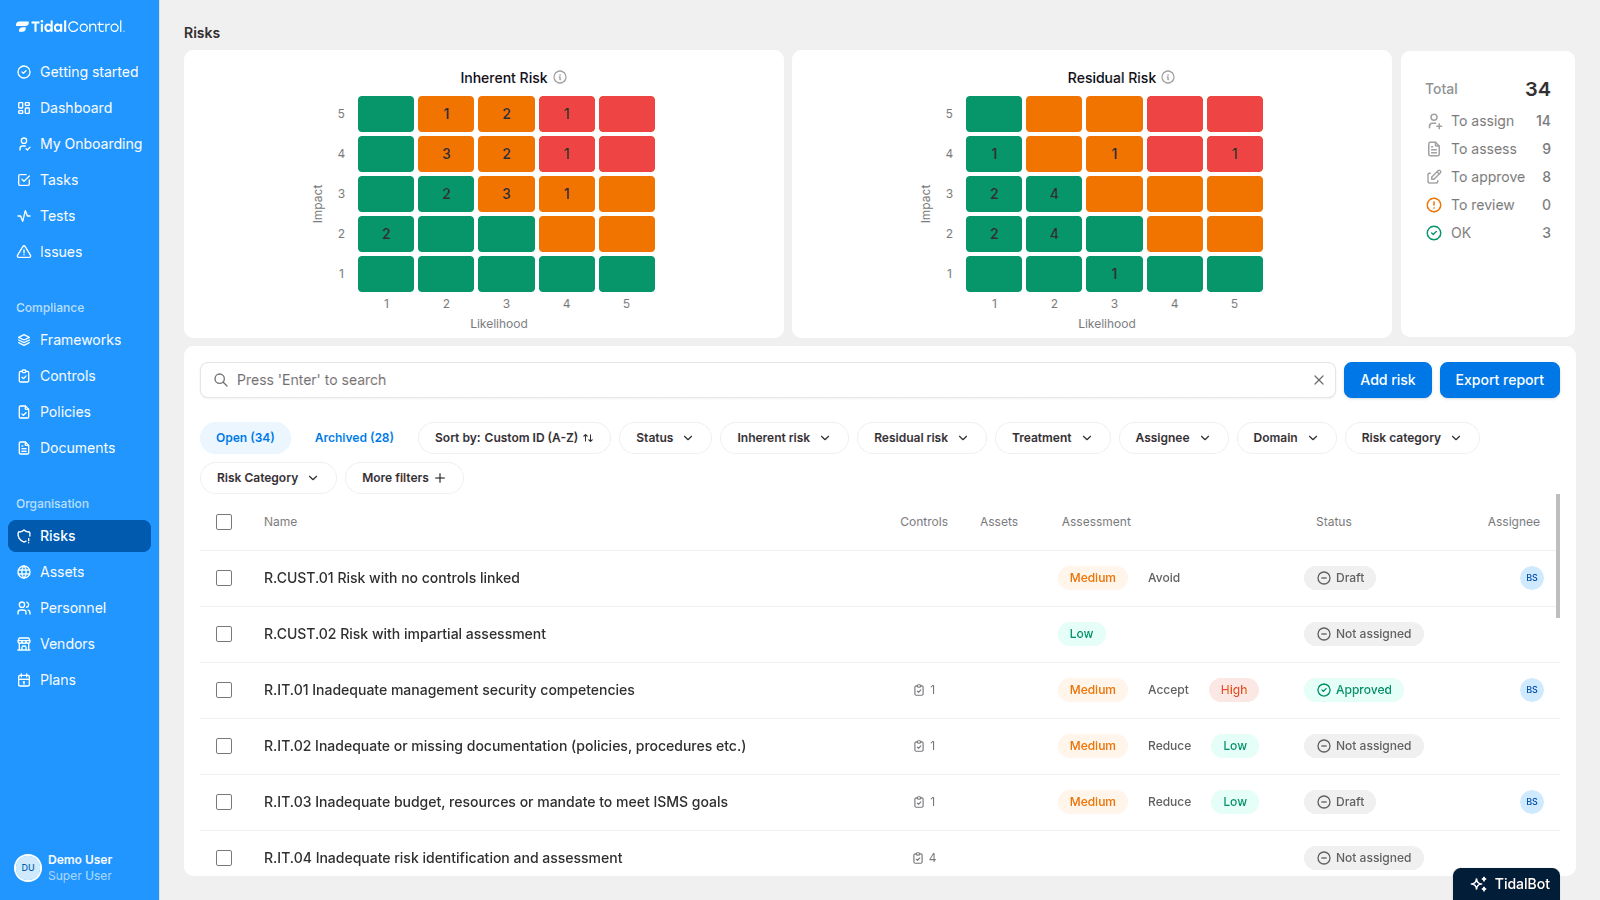
Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

Risk assessment in Tidal ControlRisk assessments that work

Issues management

Track and resolve issues - all in one place

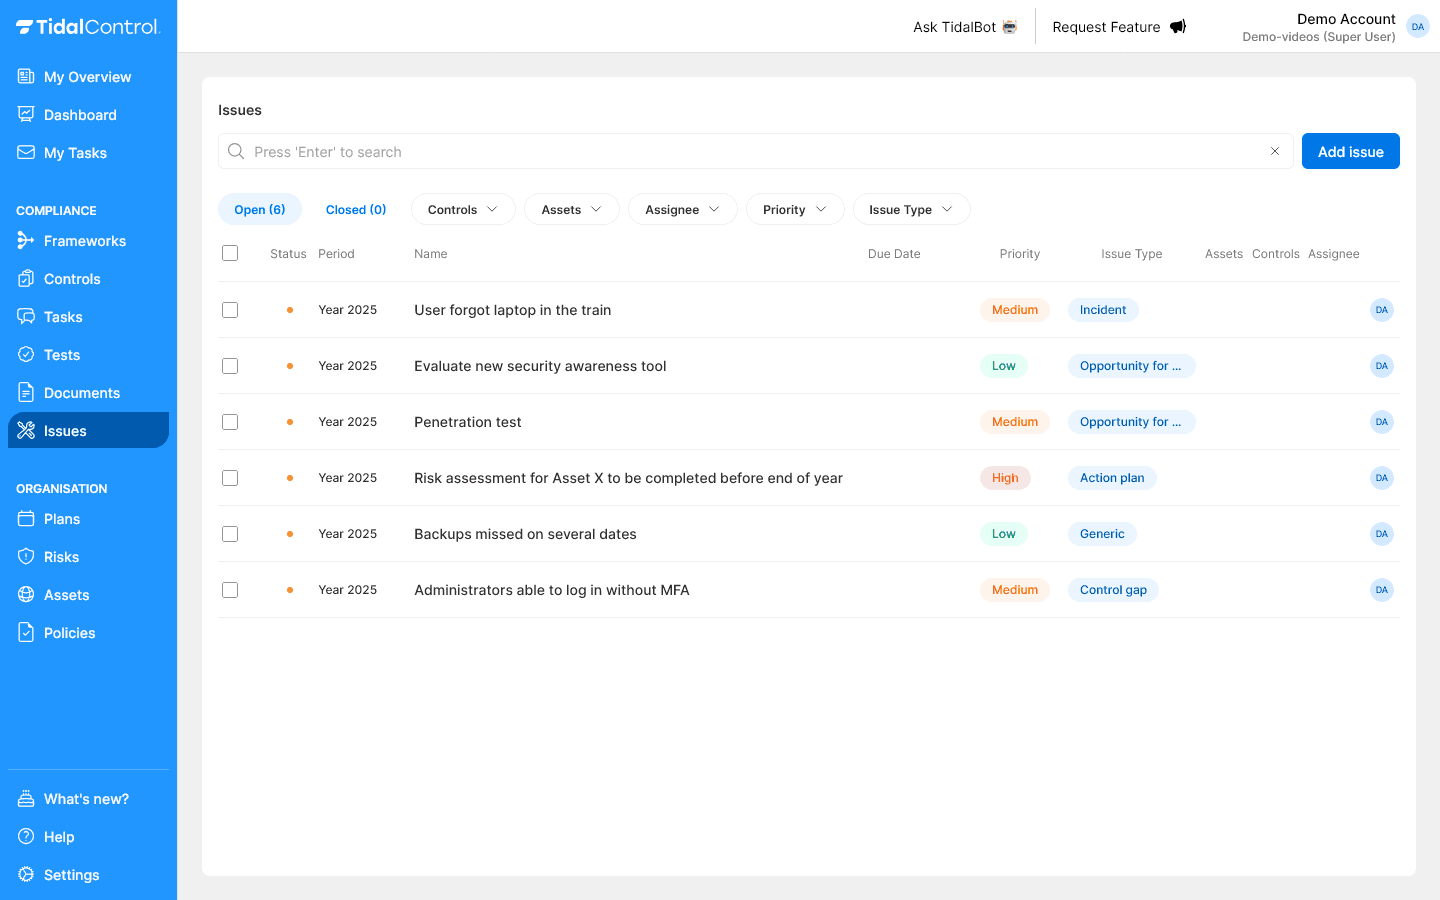
Simplify issue management with a centralised system that handles everything from audit findings to improvement opportunities. Keep your team aligned and ensure nothing gets missed with clear ownership, priorities, and automated tracking.

Issues management in Tidal ControlTrack and resolve issues - all in one place

Policy center

Policies without the hassle

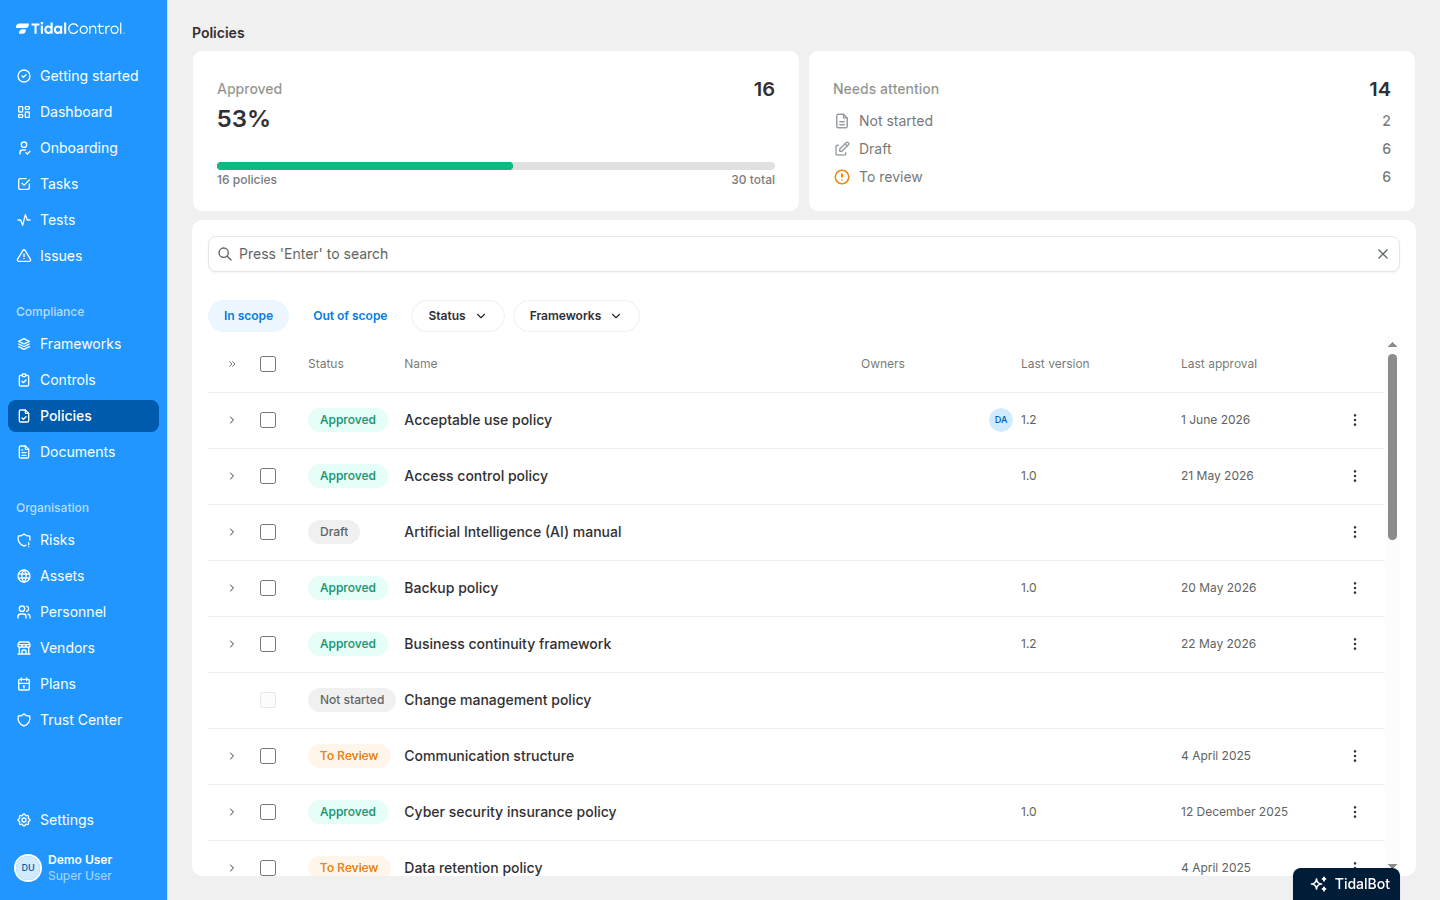
Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

Vendor management

Supplier risk assessment that actually works

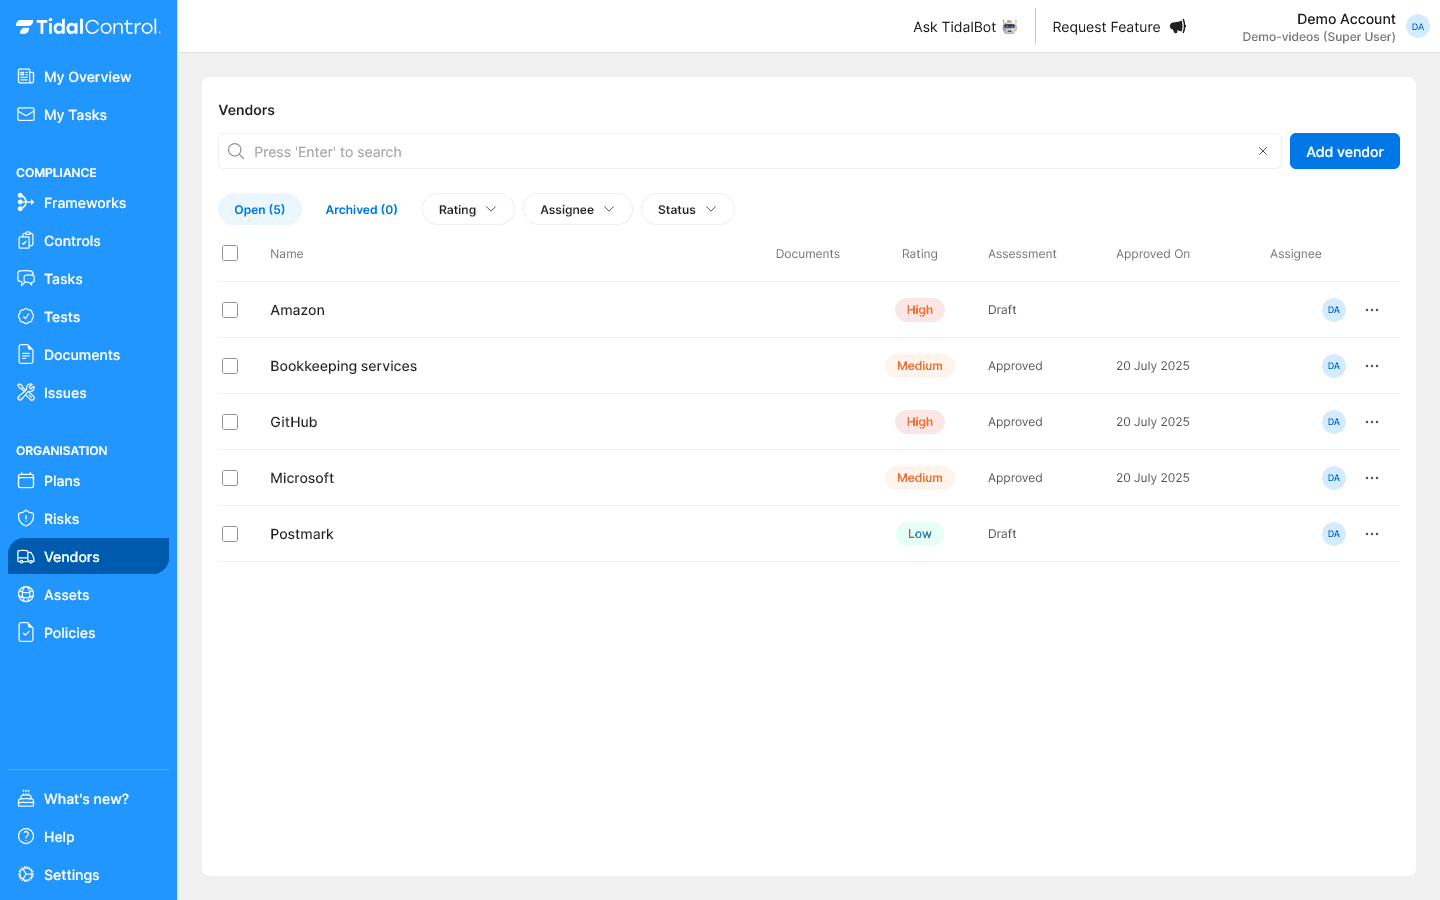
Transform supplier risk assessment from a time-consuming task into an automated process that helps your business grow. Add vendors in seconds with our vendor database that automatically fills in all important details, from privacy policies to SOC2 reports. Our intelligent system then automatically assesses risks and helps you make the right decisions.

Vendor management in Tidal ControlSupplier risk assessment that actually works

Personnel & onboarding

Employee compliance without the spreadsheet

The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

Integrations

Automation makes life more fun!

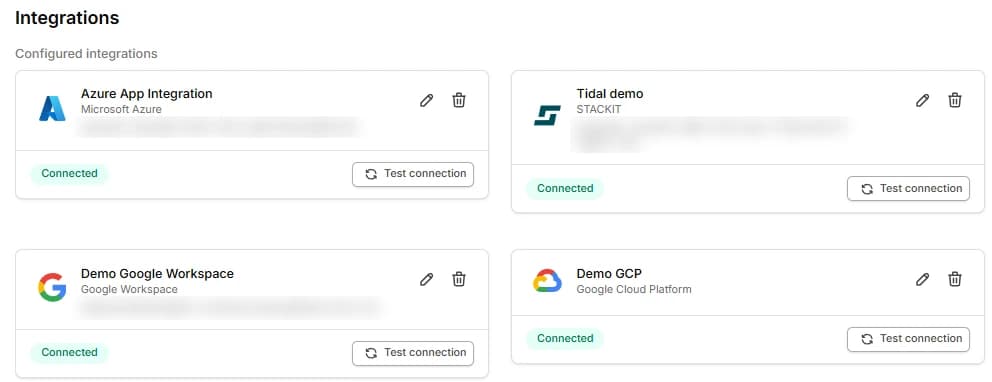
Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • Baselines

    Manual

    A spreadsheet with hundreds of rows

    With Tidal

    Pre-mapped per baseline with owners

  • Tailoring

    Manual

    Decisions spread across documents

    With Tidal

    Recorded and approved per control

  • Collecting evidence

    Manual

    Manual for every assessment

    With Tidal

    Automatically from your tools

  • Findings

    Manual

    An action list in a separate sheet

    With Tidal

    Followed to closure

  • NIST SP 800-53 and ISO 27001

    Manual

    Two projects side by side

    With Tidal

    One set of controls, evidence once

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

See all success stories

Integrate with your existing tools

NIST SP 800-53 software and assessments

NIST SP 800-53 is large: hundreds of controls in twenty families, with a different selection per baseline. In a spreadsheet you quickly lose track of which controls apply, which you tailored and why.

NIST SP 800-53 software sets up the baseline for you, records tailoring per control and links every control to an owner and evidence.

At an assessment the evidence is ready, and afterwards you see which controls need attention.

Frequently asked questions

NIST SP 800-53 is a catalogue of security and privacy controls for federal information systems. It's mandatory for US federal agencies and contractors but increasingly adopted by organisations seeking detailed, recognised security controls.

Control baselines (Low, Moderate, High) are determined by FIPS 199 categorisation based on potential impact of security breaches. Our platform helps you categorise your systems and implement appropriate baseline controls efficiently.
Our platform supports NIST 800-53 Revision 5, the current version. If you're transitioning from Rev 4, we provide mapping and migration support to help you update your implementation to current requirements.

Yes, FedRAMP baselines are based on NIST 800-53 with additional requirements. Our platform supports FedRAMP implementation, helping cloud service providers meet authorisation requirements for federal cloud deployments.

Our platform supports control tailoring as described in NIST 800-53, allowing you to customise baselines based on specific requirements and risk assessments. You can document tailoring decisions and maintain appropriate approval evidence.
Our platform maintains evidence for security control assessors, including control implementations, test results, continuous monitoring data, and plan of actions and milestones (POA&Ms). This streamlines assessment and authorisation processes significantly.