The CIS Controls, implemented step by step and measurable

Eighteen prioritised measures against the attacks that happen most often. Tidal Control sets them up for you per Implementation Group, collects evidence automatically from your tools and shows which safeguards are still open.

  • 18 controls, 153 safeguards
  • Per Implementation Group
  • Together with ISO 27001
  • Built in the EU
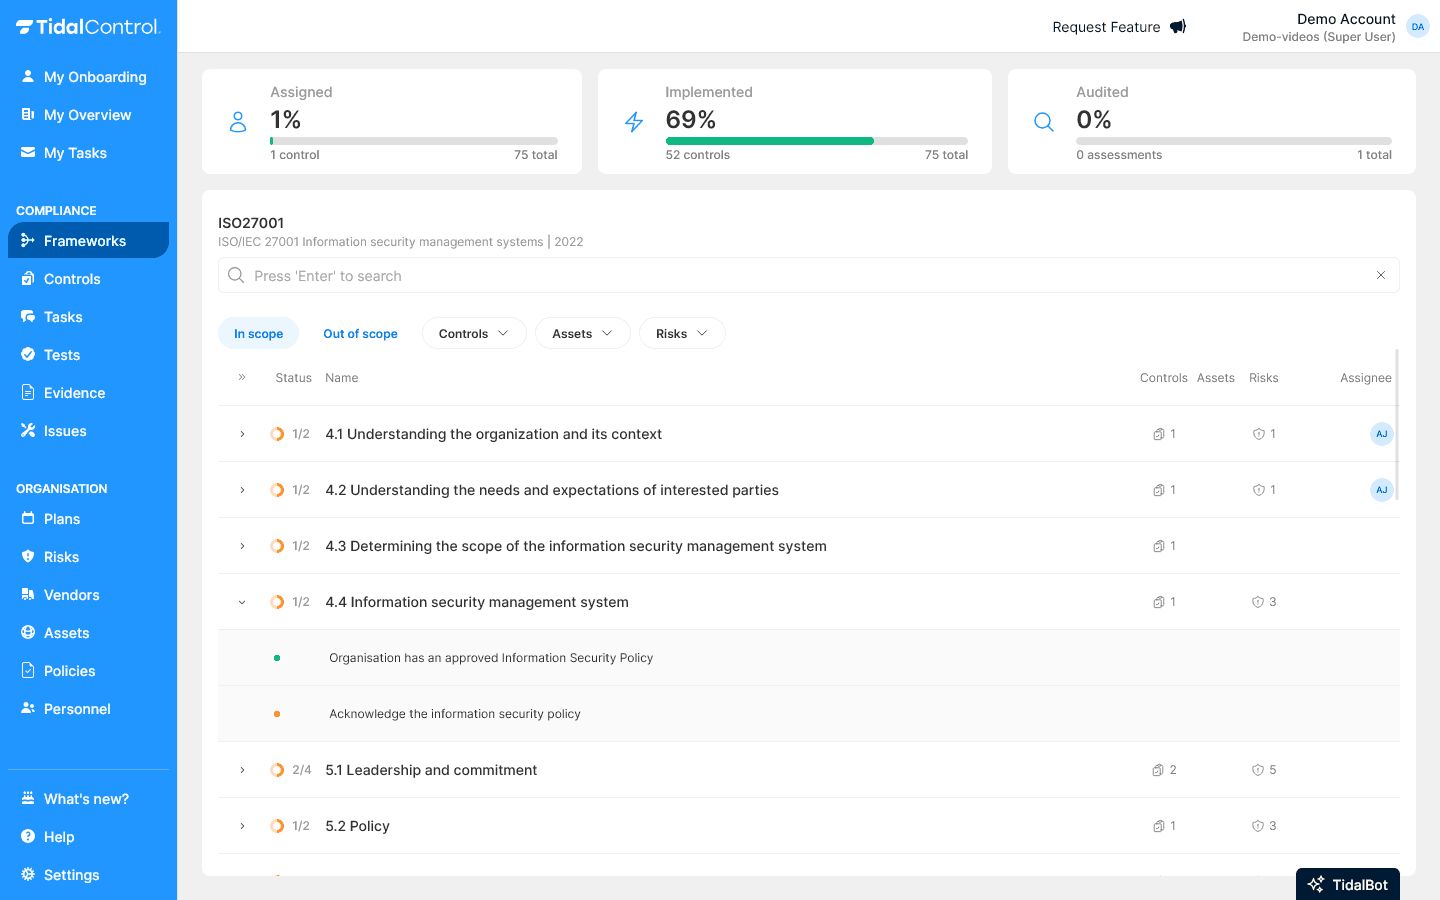
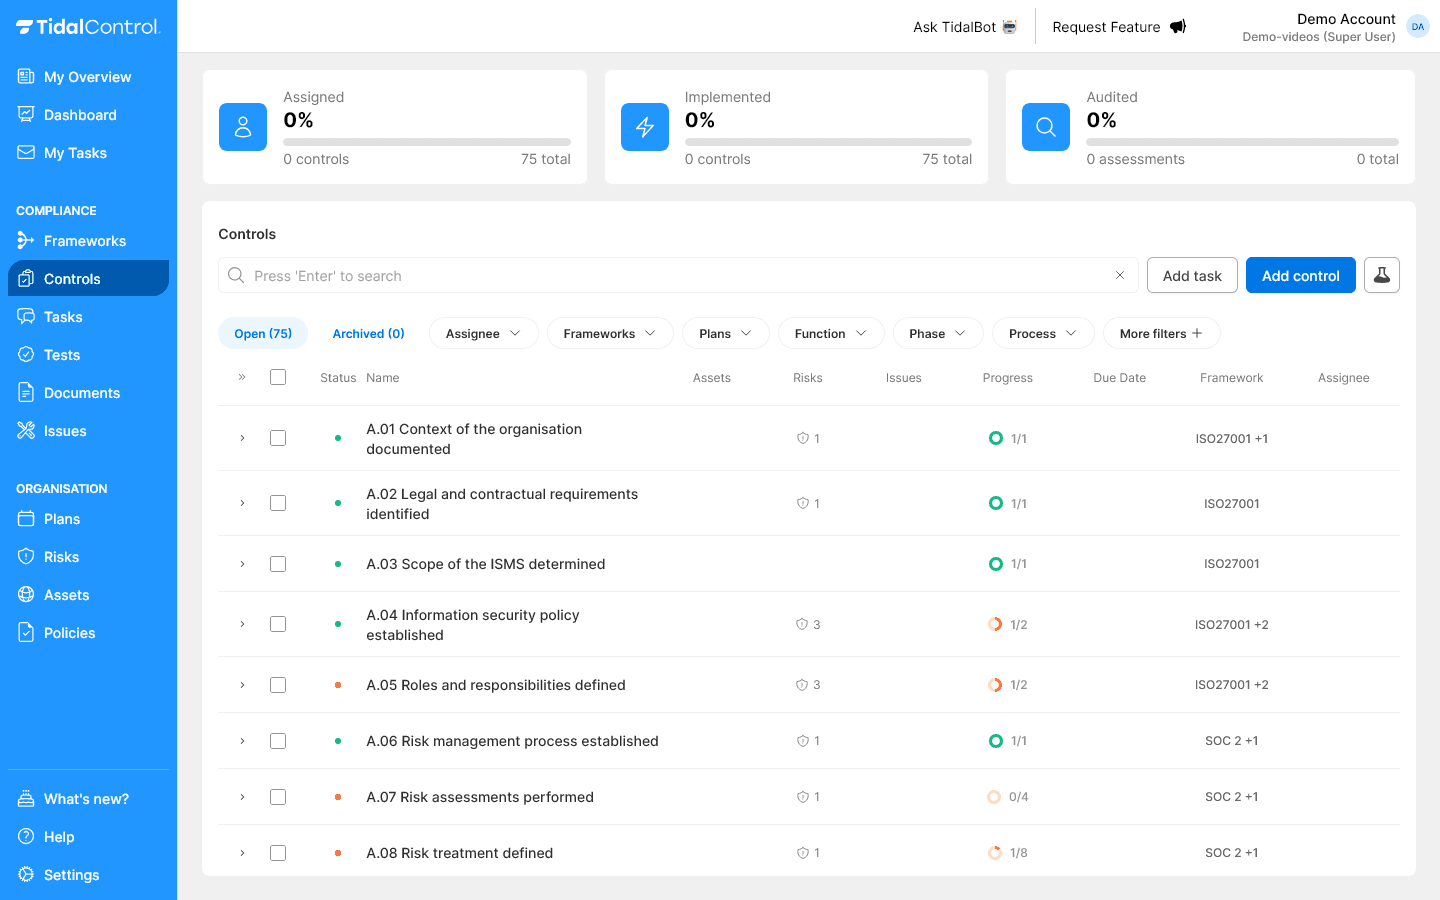
The CIS Controls overview in Tidal Control with the status of safeguards and evidence

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From inventory to measurable resilience

The CIS Controls have no certificate. The goal is demonstrably lower risk, in the order that pays off most. Tidal shows what is expected of your team at each step.

  1. Step 1

    Implementation Group

    Decide which group fits your size and risk: IG1, IG2 or IG3.

  2. Step 2

    Inventory

    Hardware, software and data mapped, the base for everything that follows.

  3. Step 3

    IG1

    The safeguards for essential cyber hygiene in place.

  4. Step 4

    IG2 and IG3

    Extending to the safeguards that belong to your group.

  5. Step 5

    Measure and demonstrate

    Status and evidence for each safeguard, ready for customers and auditors.

  6. After that

    Keep it up

    Safeguards monitored continuously, and a sparring partner for new threats.

How Tidal helps with the 18 CIS Controls

CIS Controls v8 consists of 18 controls with 153 safeguards in total. Tidal groups them into six and sets them up for you, with an owner, policy and evidence for each safeguard.

controls
18controls
safeguards
153safeguards

CIS Controls v8

  • 1, 2

    Inventory

    An overview of all devices and software in your environment.

  • 3, 4

    Data and configuration

    Data protected and systems configured securely.

  • 5, 6

    Accounts and access

    Accounts managed, privileges limited and MFA where it counts.

  • 7, 10, 11

    Vulnerabilities and malware

    Patching, keeping malware out and being able to recover data.

  • 8, 9, 12, 13

    Logging and network

    Keeping logs, securing email and browsers, monitoring the network.

  • 14-18

    People, suppliers and incidents

    Awareness, suppliers, applications, incident response and penetration testing.

The CIS Controls in brief

The CIS Controls are a set of 18 prioritised security measures from the Center for Internet Security, based on the attacks seen most often in practice. They are split into three Implementation Groups: IG1 is essential cyber hygiene for every organisation, IG2 and IG3 build on it. There is no certificate; you use them to prioritise your security and make it measurable.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • A clear order: what pays off most comes first
  • Protection against the most common attacks
  • Measurable progress for the board and customers
  • A practical base for ISO 27001 and NIS2
  • Less chance of incidents and outages

How you work on the CIS Controls in Tidal

From inventory to incident response: every safeguard in one place.

Controls management

Control management that works your way

Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

Controls management in Tidal ControlControl management that works your way
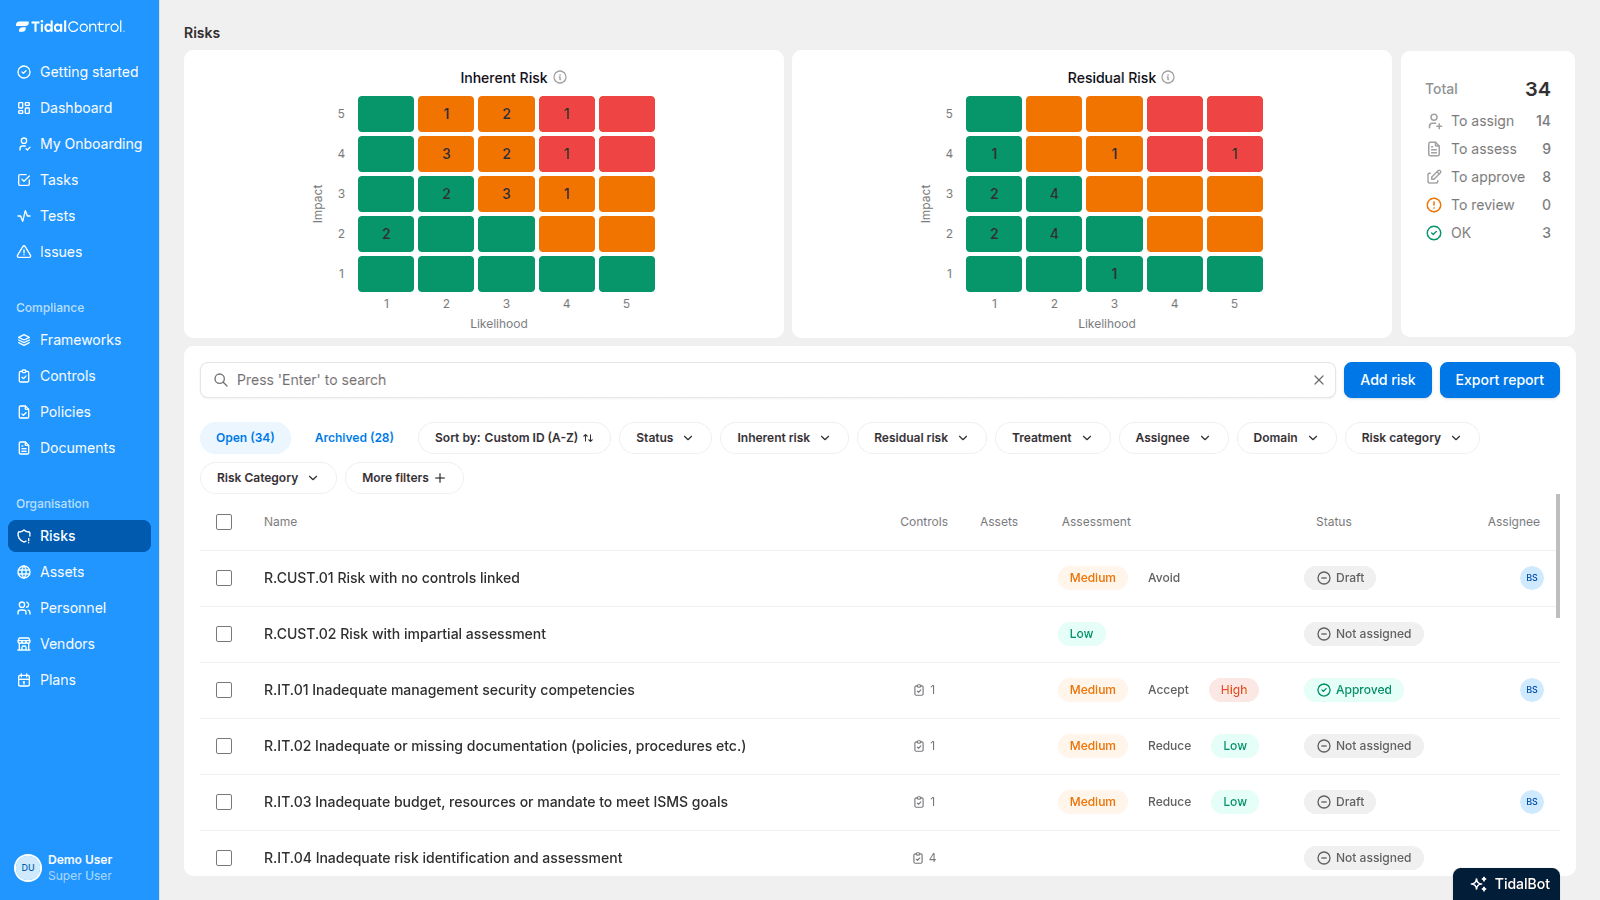
Risk assessment

Risk assessments that work

Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

Risk assessment in Tidal ControlRisk assessments that work

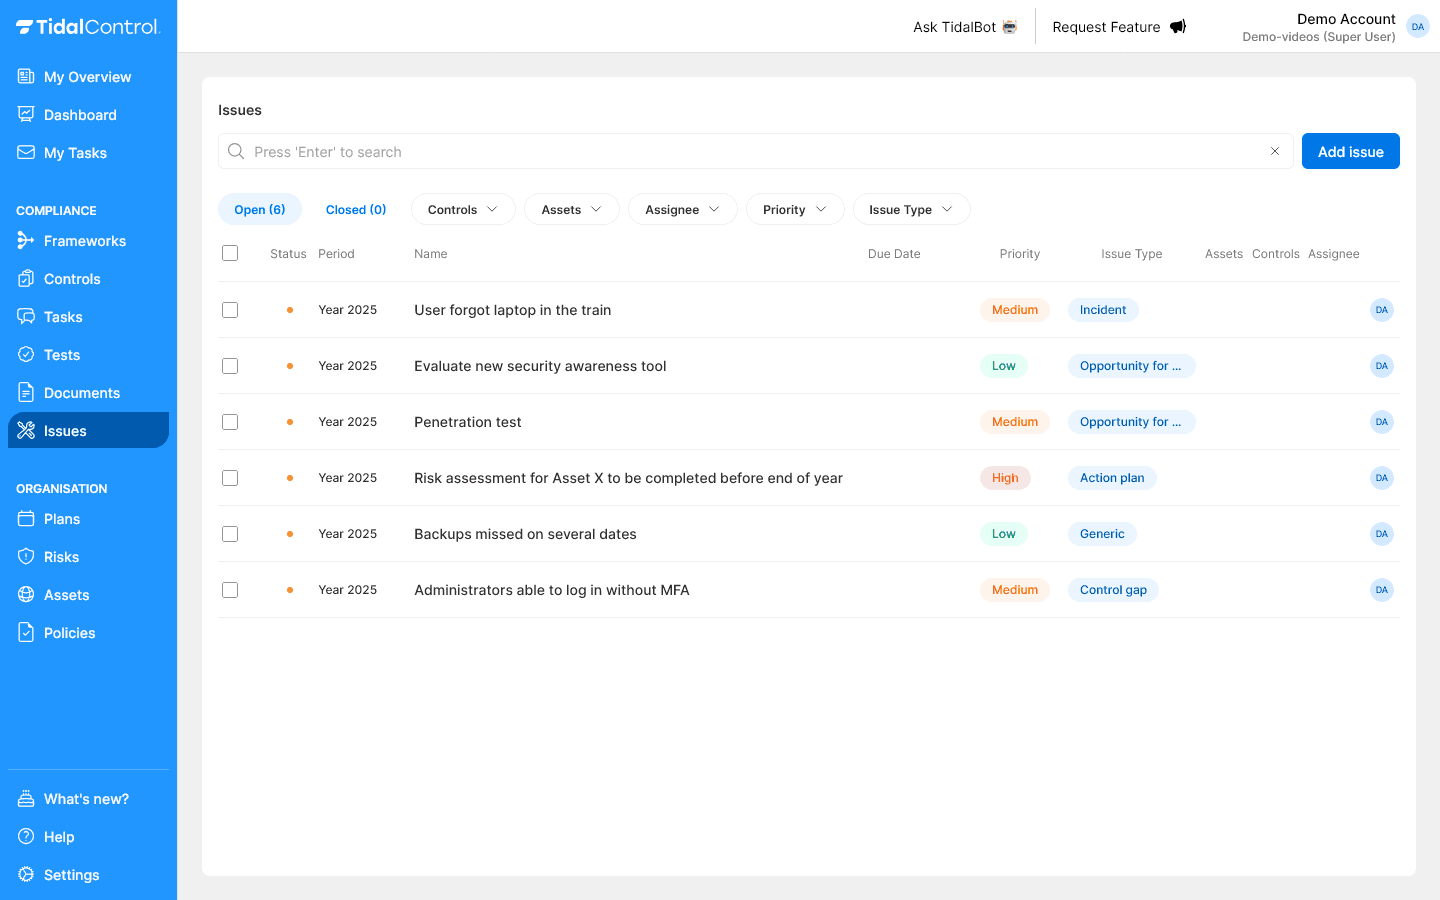
Issues management

Track and resolve issues - all in one place

Simplify issue management with a centralised system that handles everything from audit findings to improvement opportunities. Keep your team aligned and ensure nothing gets missed with clear ownership, priorities, and automated tracking.

Issues management in Tidal ControlTrack and resolve issues - all in one place

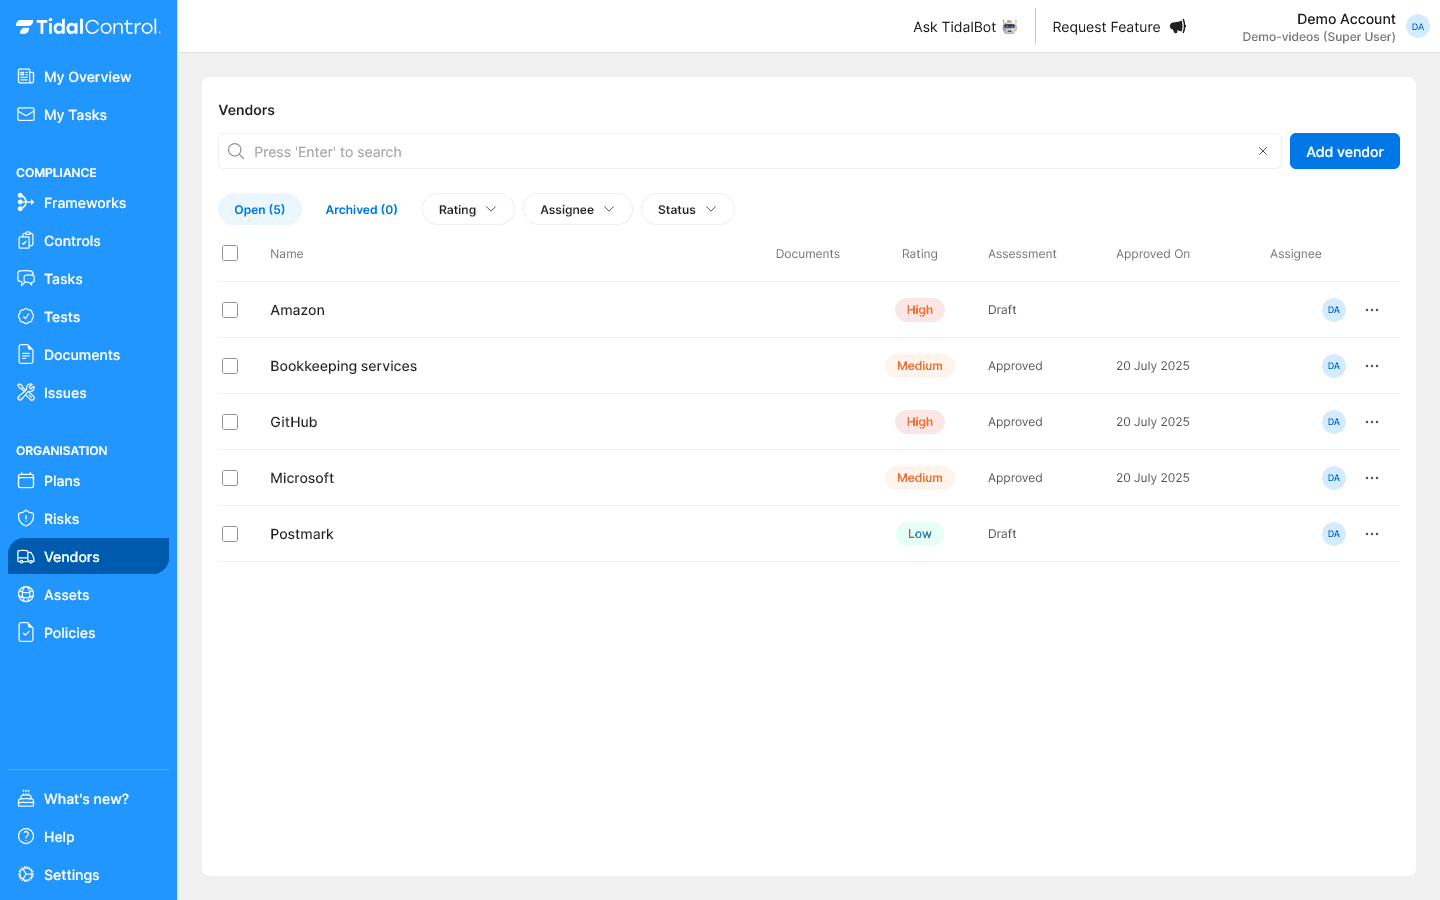
Vendor management

Supplier risk assessment that actually works

Transform supplier risk assessment from a time-consuming task into an automated process that helps your business grow. Add vendors in seconds with our vendor database that automatically fills in all important details, from privacy policies to SOC2 reports. Our intelligent system then automatically assesses risks and helps you make the right decisions.

Vendor management in Tidal ControlSupplier risk assessment that actually works

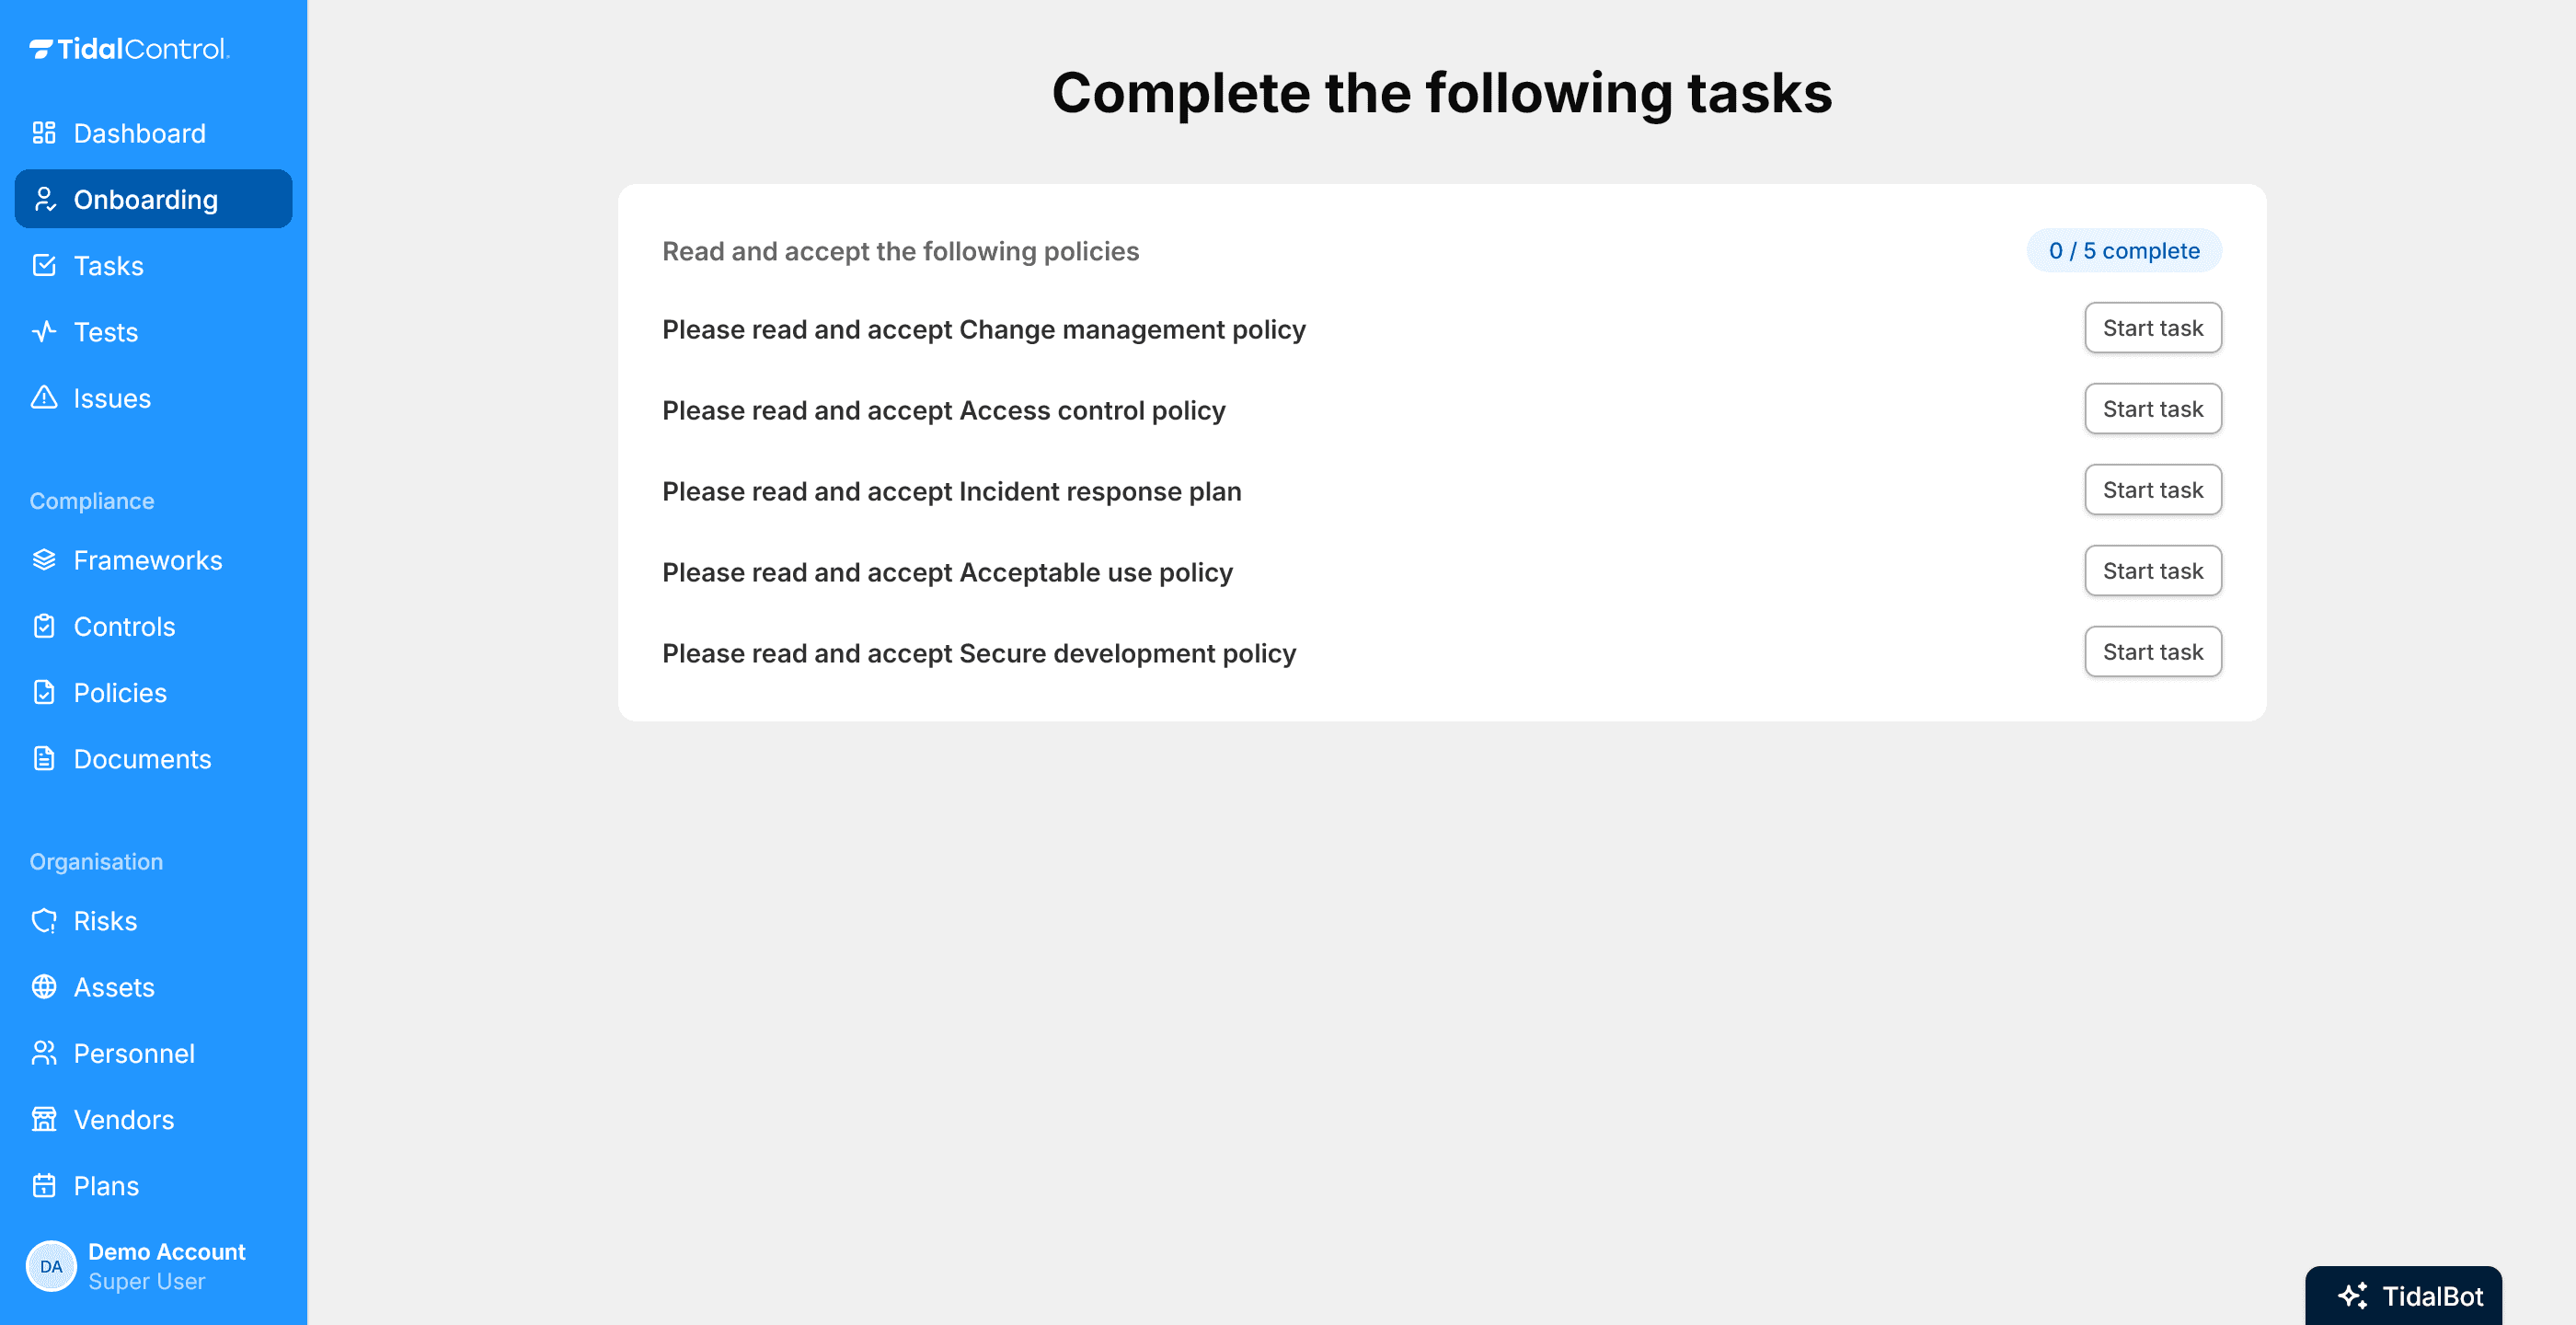
Personnel & onboarding

Employee compliance without the spreadsheet

The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

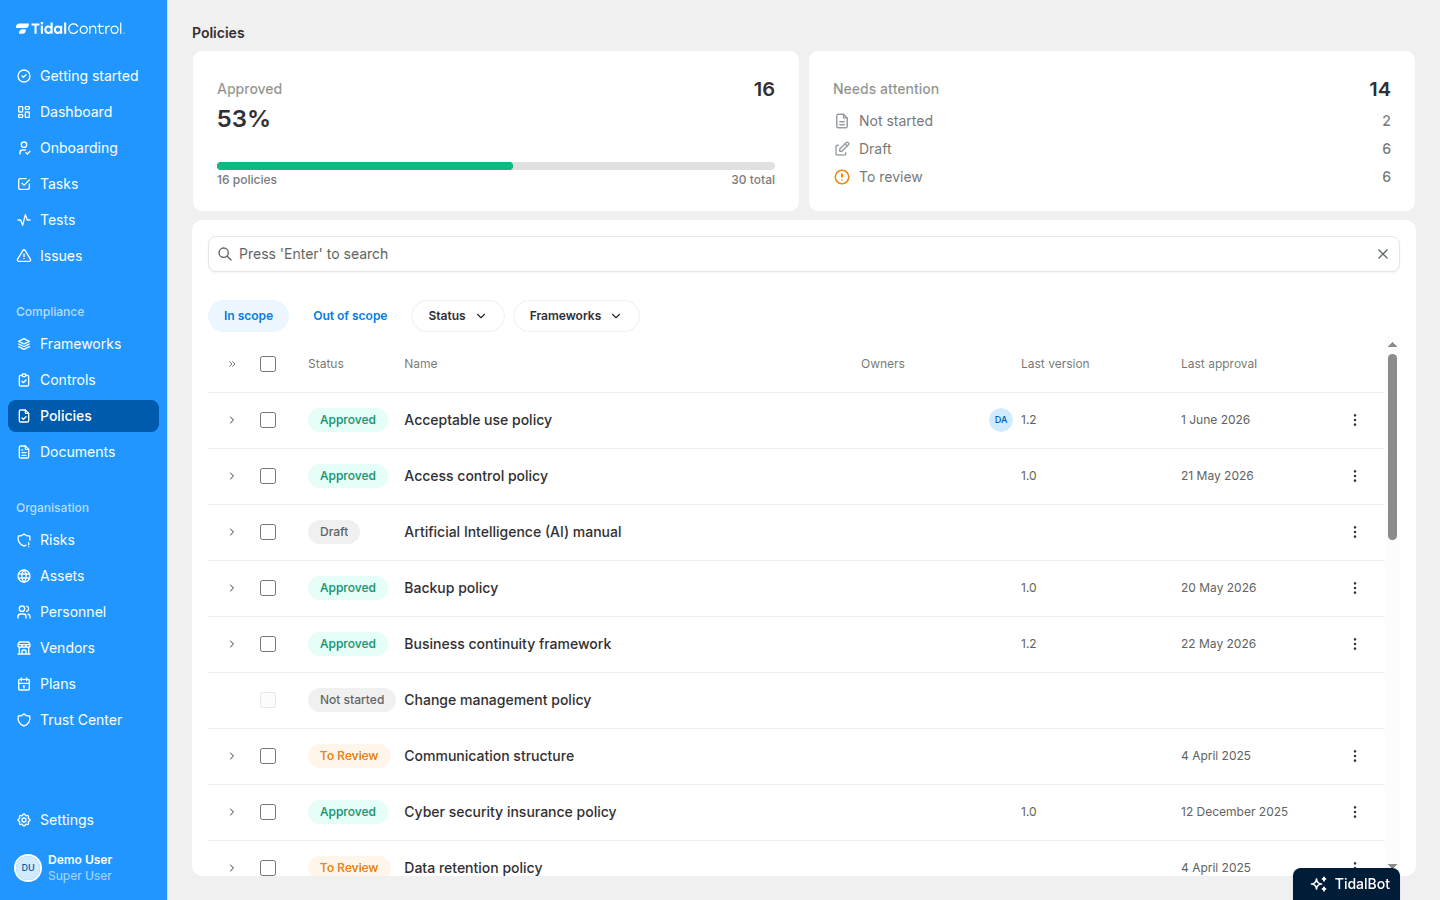
Policy center

Policies without the hassle

Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

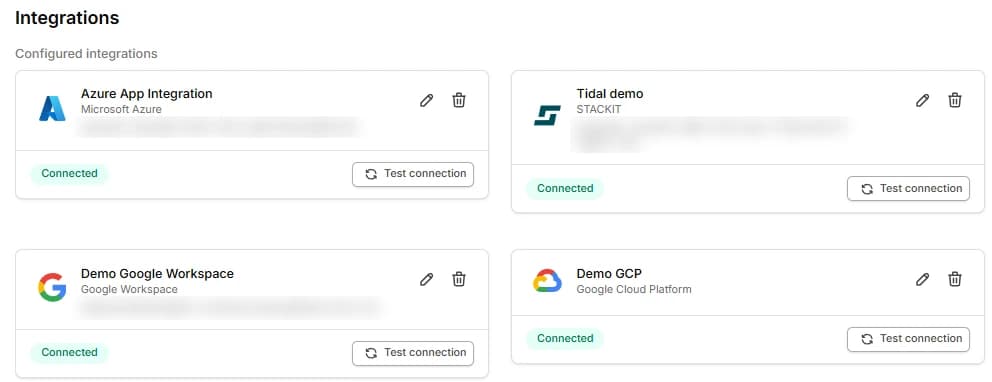
Integrations

Automation makes life more fun!

Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • Safeguards

    Manual
    A spreadsheet with 153 rows

    With Tidal

    Pre-mapped per Implementation Group

  • Collecting evidence

    Manual

    Manual per safeguard

    With Tidal

    Automatically from your tools

  • Measuring progress

    Manual

    An estimate each time

    With Tidal

    Status per safeguard, always current

  • CIS and ISO 27001

    Manual

    Two projects side by side

    With Tidal

    One set of measures, evidence once

  • Keeping it up

    Manual

    Lapses after the project

    With Tidal

    Continuous monitoring

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

See all success stories

Integrate with your existing tools

CIS Controls software and implementation

The strength of the CIS Controls is the order: first the safeguards that help against most attacks. But with 153 safeguards a spreadsheet quickly loses track of what is in place, who owns it and whether it still works.

CIS Controls software sets up the safeguards per Implementation Group, links them to your systems and collects evidence automatically from your tools. You see the status per control, and where something has slipped.

That makes progress visible to the board and customers, instead of a one-off estimate.

Frequently asked questions

CIS Controls are a prioritised set of 18 cybersecurity best practices developed by security experts. They protect against the most common cyber attacks and are recognised globally as an effective security framework. Implementation helps you build practical, measurable security improvements.

Implementation Groups (IG1, IG2, IG3) correspond to organisation size and resources. IG1 is for small organisations with limited resources, IG2 for medium organisations, and IG3 for large organisations with mature security programmes. Our platform helps you select the appropriate level.

No. The CIS Controls are a set of recommendations, not a certifiable standard. You use them to prioritise your security and make it measurable. If you want a certificate customers recognise, combine them with ISO 27001.

Our platform automatically collects evidence for many CIS safeguards from your cloud providers, identity systems, and development tools. This reduces manual work while ensuring continuous monitoring of security controls and providing audit-ready evidence.

Yes, CIS Controls map to many regulatory frameworks including ISO 27001, NIST CSF, and others. Implementing CIS Controls provides a solid security foundation that supports multiple compliance requirements simultaneously.

Our platform continuously monitors your CIS safeguards, alerts you to gaps or changes, and schedules regular assessments. Automated evidence collection ensures you maintain security controls with minimal ongoing effort while demonstrating sustained implementation.