ISO 27701 certification for your privacy management system

The international standard for privacy management. Tidal Control sets up your privacy management system for your role as controller, processor or both, links it to the GDPR and prepares you for the audit by the certification body.

  • For controller and processor
  • Linked to the GDPR
  • Together with ISO 27001
  • Built in the EU
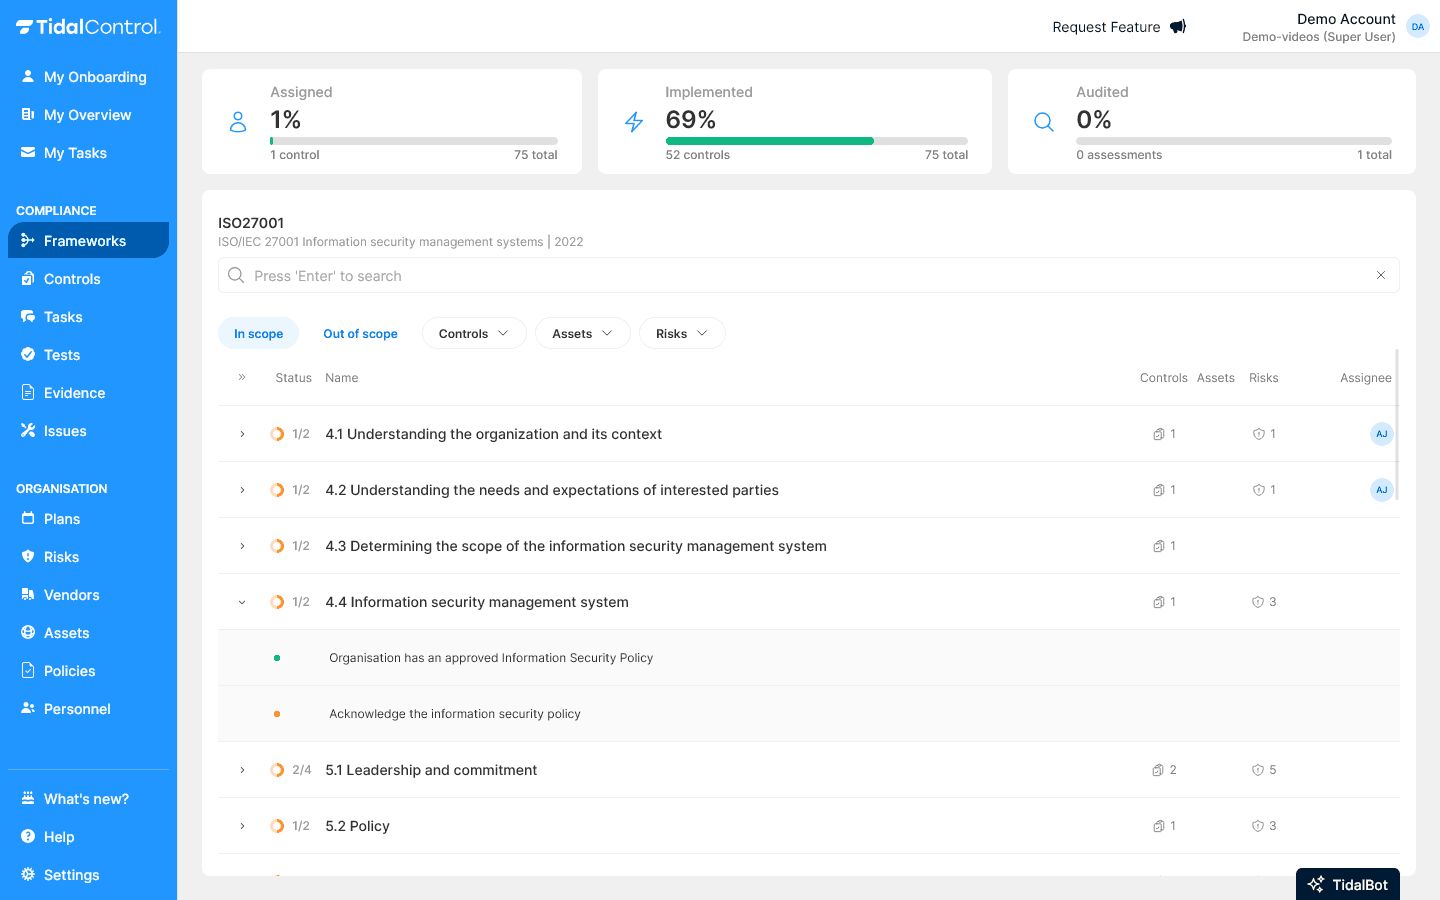
The ISO 27701 overview in Tidal Control with the status of controls and evidence

These companies run their compliance on Tidal Control

  • LiveDrop logo
  • Datenna logo
  • CByte logo
  • Infradock logo
  • PoA logo
  • Floryn logo
  • ElasticScale logo
  • DebtCo logo
  • BrainStax logo
  • EnableNow logo
  • Woningnet logo
  • Nedscaper logo
  • Aivory logo
  • Fleetport logo
  • Promptwatch logo
  • Amsterdam logo

From baseline to ISO 27701 certificate

How long it takes depends on what is already in place, such as an ISMS or a GDPR programme. Tidal shows what is expected of your team at each phase, and it does not stop at the certificate.

  1. Step 1

    Baseline

    Scope, your role per processing activity and a gap analysis against ISO 27701.

  2. Step 2

    Implementation

    Privacy policy, controls, record and evidence recorded.

  3. Step 3

    Internal audit

    Self-assessment and management review.

  4. Step 4

    Stage 1 audit

    Documentation review by the certification body.

  5. Step 5

    Stage 2 and certificate

    Implementation audit and your ISO 27701 certificate.

  6. After that

    Audits and sparring

    Your annual audits prepared, and a sparring partner for new processing.

How Tidal helps with the ISO 27701 controls

ISO 27701 describes a privacy management system with separate controls for controllers and processors. Tidal sets them up for you, with an owner, policy and evidence for each control.

roles: controller and processor
2roles: controller and processor
audits passed, 100% pass rate
50+audits passed, 100% pass rate

ISO 27701 in six blocks

  • Controller

    Lawful basis and purpose

    A purpose and lawful basis recorded for every processing activity.

  • Controller

    Data subject rights

    Requests for access, rectification or erasure handled on time.

  • Controller

    Privacy by design

    Privacy built into systems and processes, with as little data as possible.

  • Processor

    Customer instructions

    Processing only as the controller instructs.

  • Processor

    Subprocessors

    Parties you bring in, known to and agreed with your customer.

  • Both

    Transfers

    Recording when data leaves the EU and on what basis.

ISO 27701 in brief

ISO 27701 is the international standard for a privacy information management system (PIMS). In the 2019 edition it was an extension of ISO 27001; since the 2025 revision it is a standalone standard. It helps you demonstrate the GDPR, with controls for both controllers and processors. An accredited certification body checks that the system works.

Dennis van de WielMax HovensMartijn Sprengers
Reviewed by Dennis, Max and MartijnFounders of Tidal Control, 45 years of combined experience in IT auditing and compliance
  • A certificate for your privacy programme
  • Evidence for GDPR accountability
  • Faster answers in supplier assessments
  • Less chance of data breaches and fines
  • One system together with ISO 27001

How you work on ISO 27701 in Tidal

From privacy risks to processors: your privacy management system in one place.

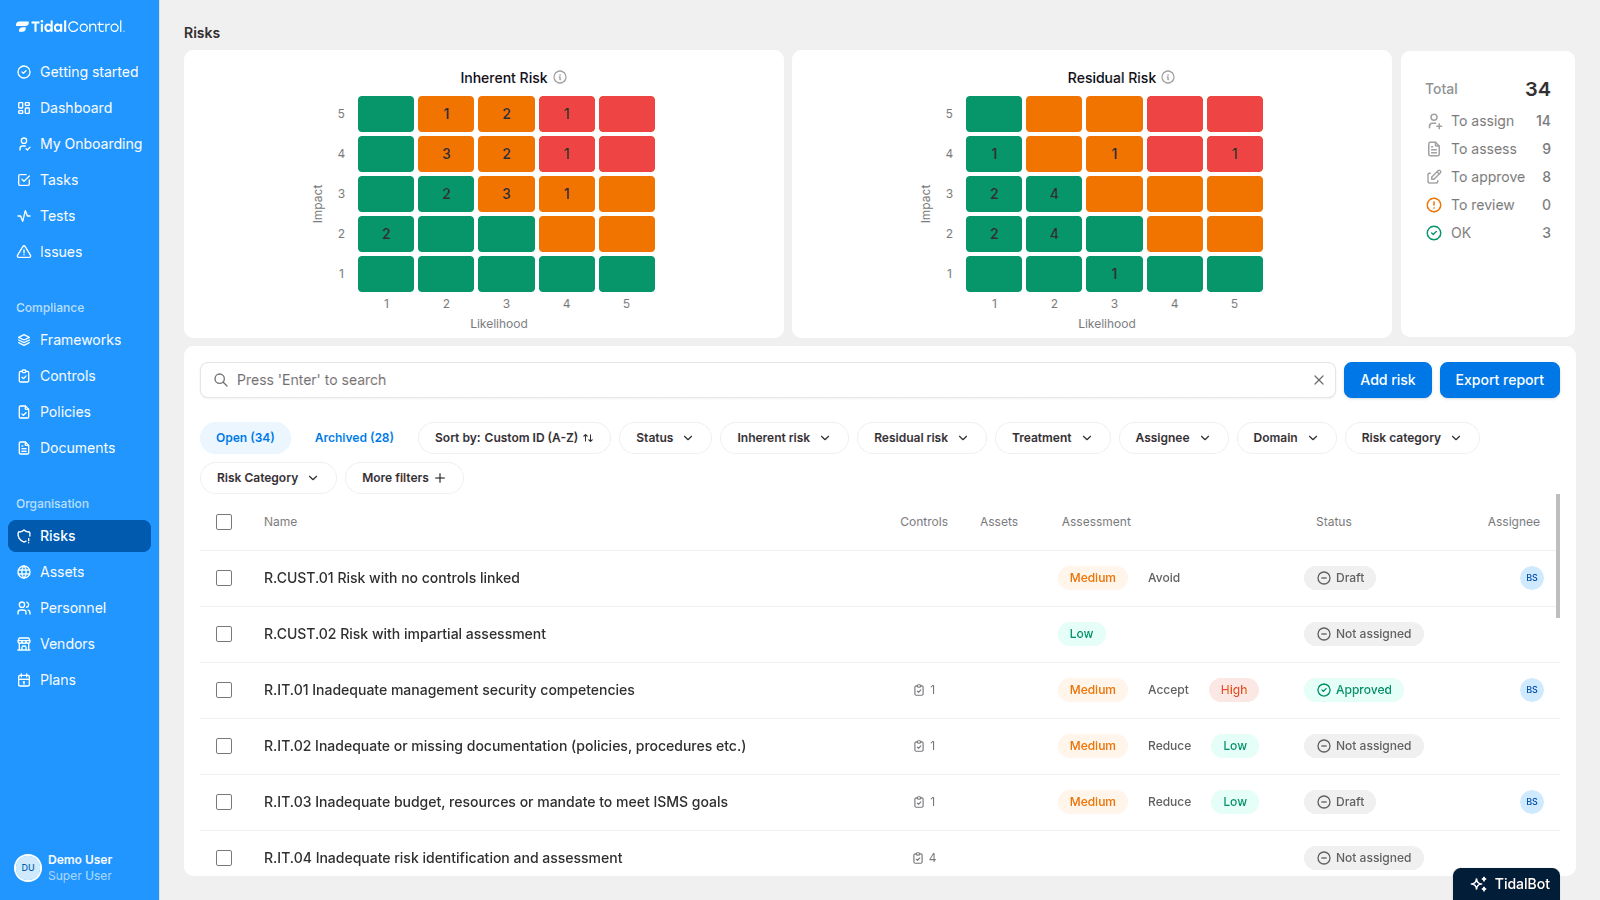
Risk assessment

Risk assessments that work

Turn risk assessment from a time-consuming task into a guided process that helps your business grow. Our AI-powered platform learns from your company's context to help assess and manage risks - even if you're new to the process.

Risk assessment in Tidal ControlRisk assessments that work
Policy center

Policies without the hassle

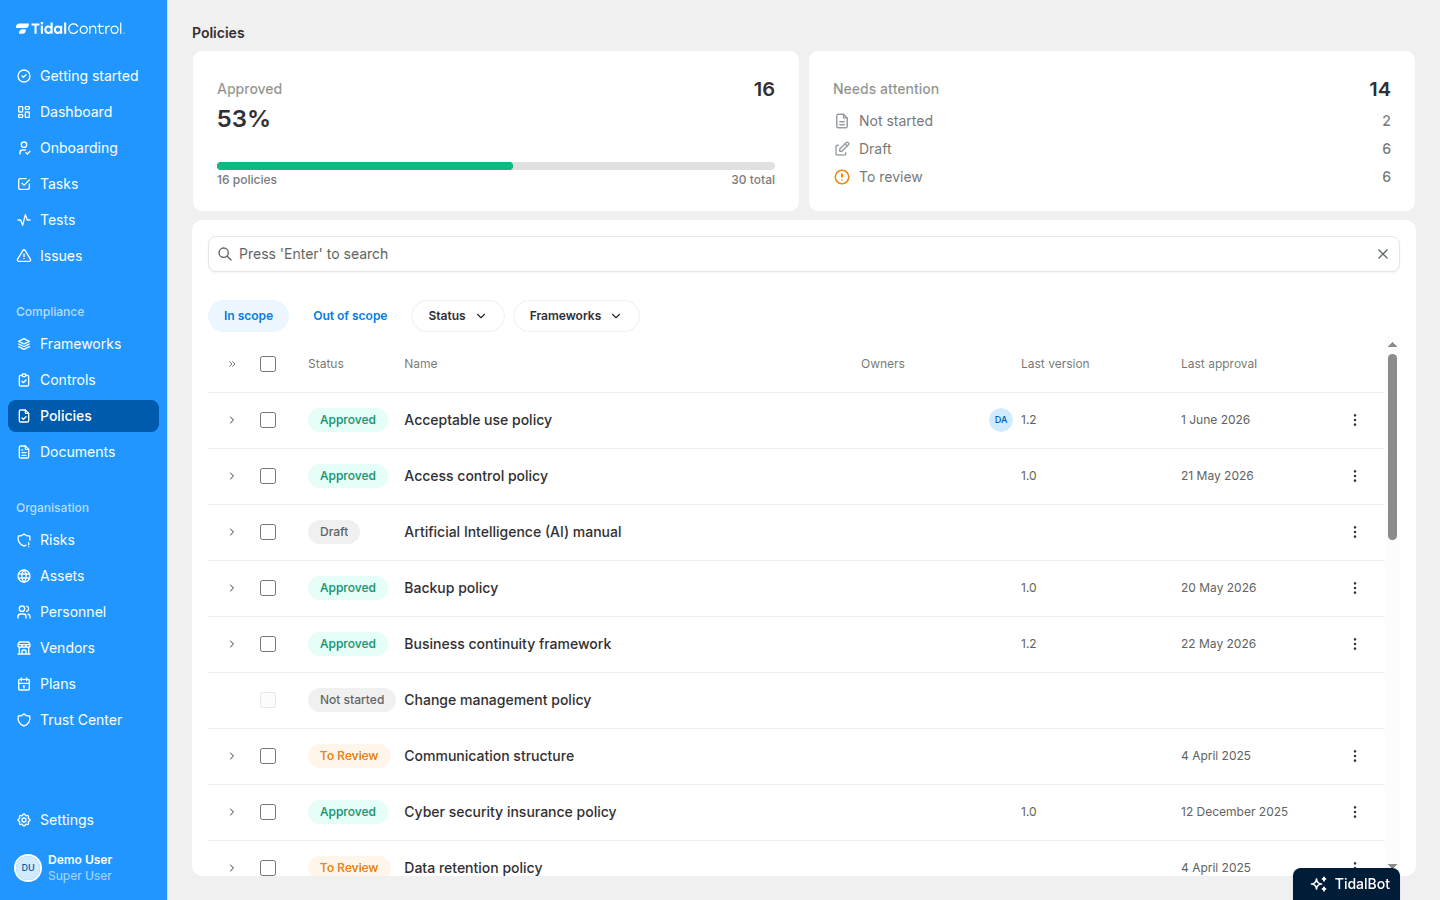
Turn policy management from a complex, time-consuming task into an automated process that grows with your business. Start with our pre-written policies designed for modern companies, or import your existing documents - either way, you'll benefit from smart automation that keeps everything on track.

Policy center in Tidal ControlPolicies without the hassle

Vendor management

Processors and subprocessors in view

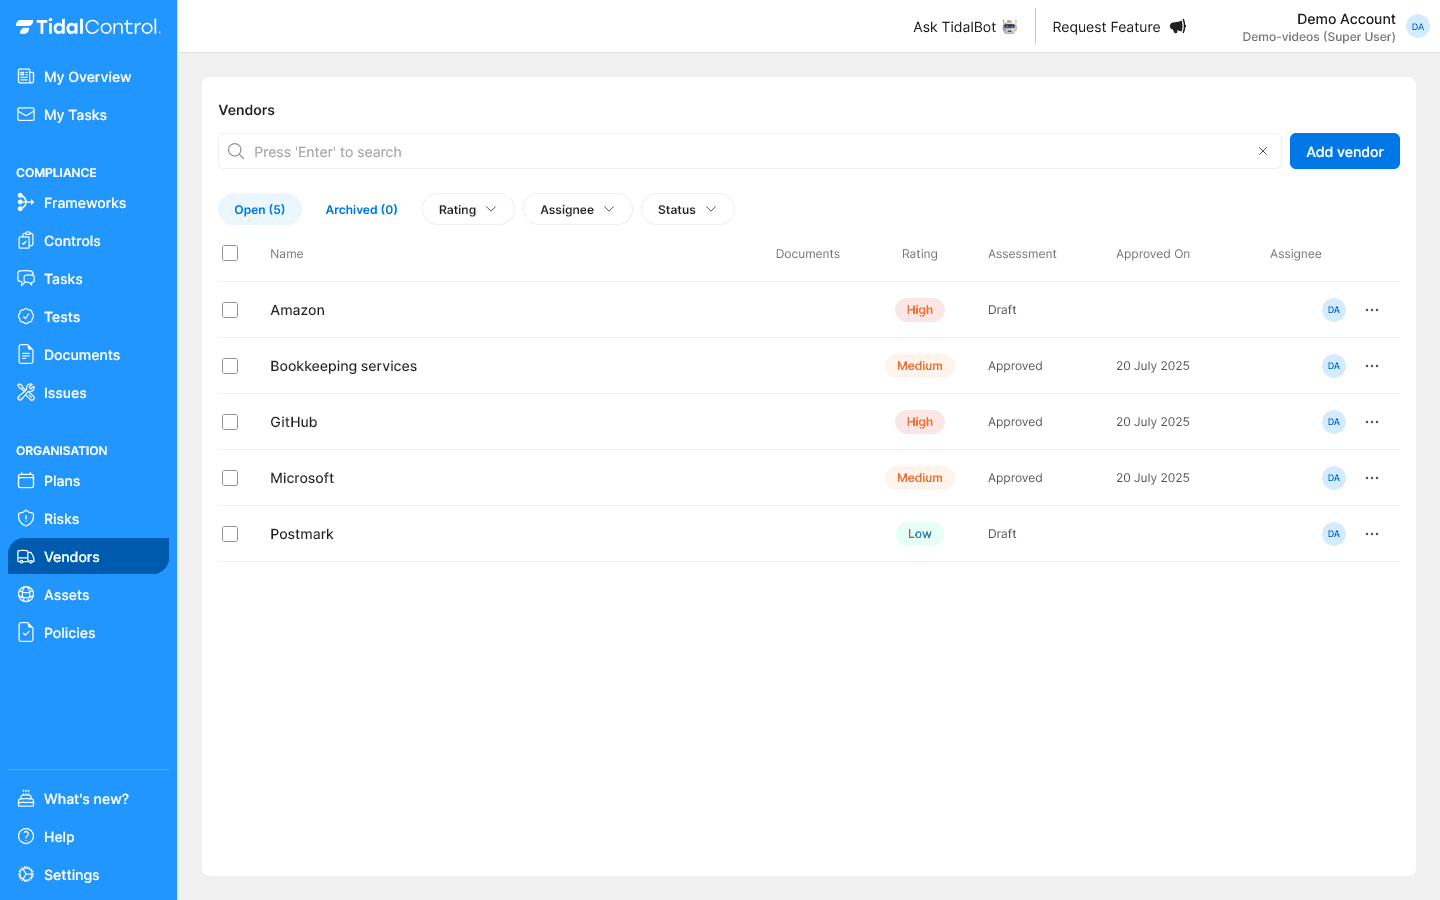
Record for each party which personal data it processes, under which agreements and in which country, with a date to review it again.

Vendor management in Tidal ControlProcessors and subprocessors in view

Issues management

Track and resolve issues - all in one place

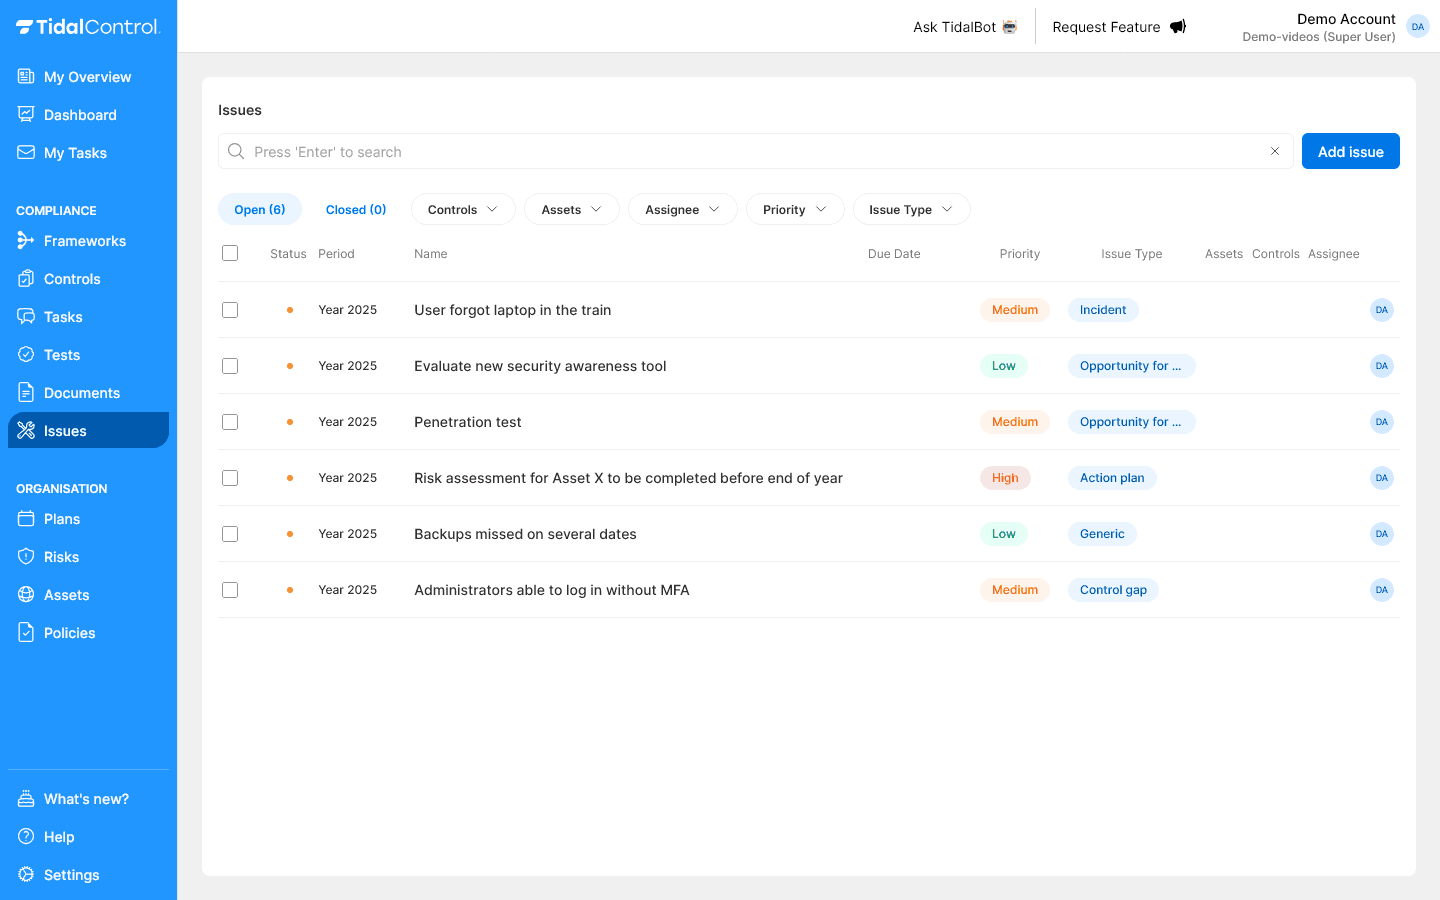
Simplify issue management with a centralised system that handles everything from audit findings to improvement opportunities. Keep your team aligned and ensure nothing gets missed with clear ownership, priorities, and automated tracking.

Issues management in Tidal ControlTrack and resolve issues - all in one place

Controls management

Control management that works your way

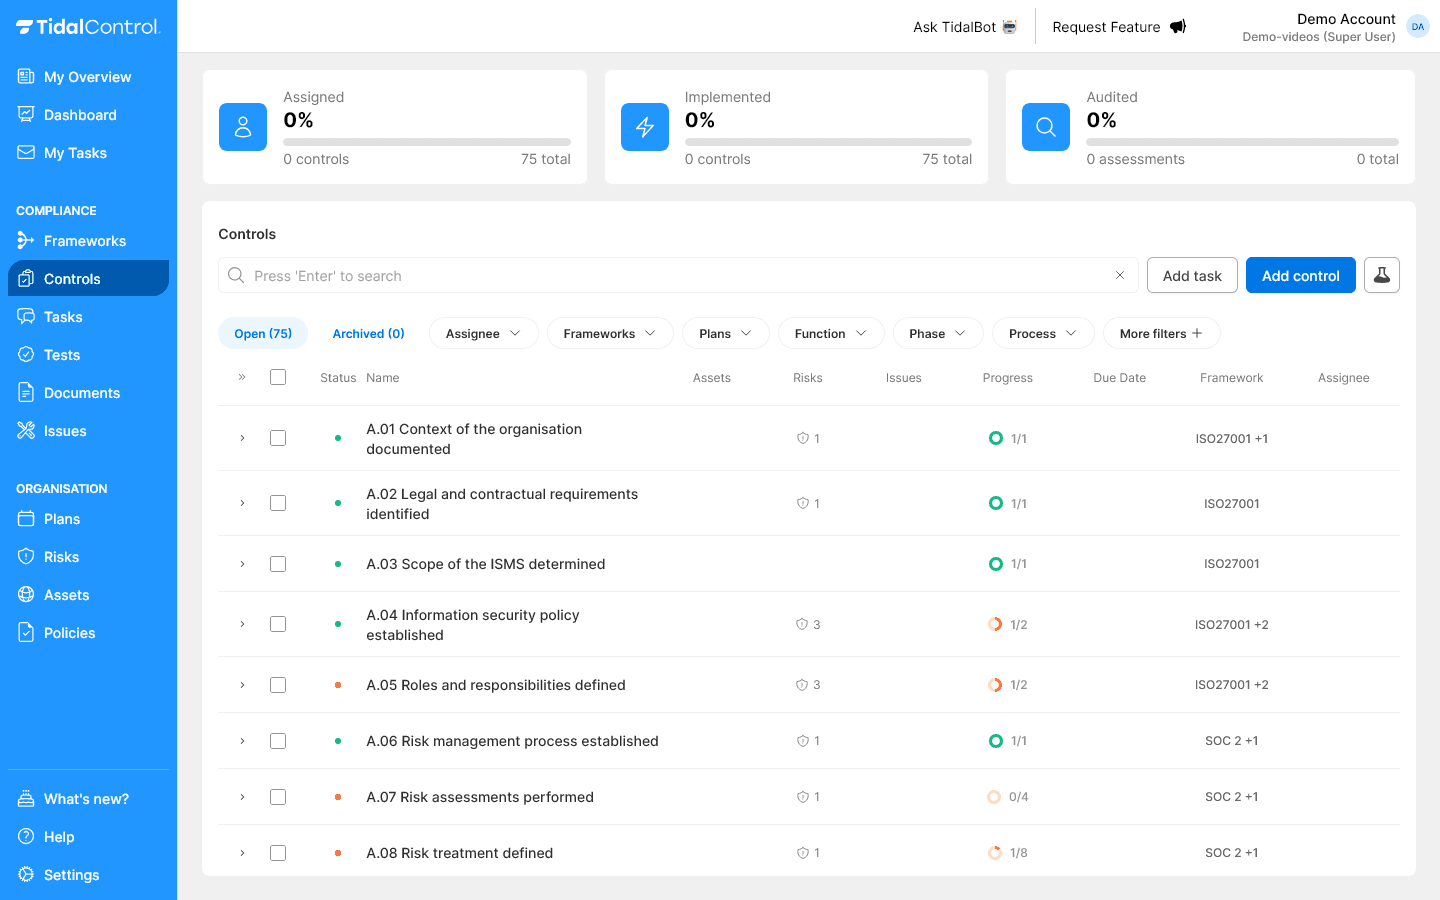
Simplify control management with flexible, automation-ready tools that adapt to your needs. Start with our control library or build your own - either way, you'll get powerful automation, clear ownership, and real-time insights.

Controls management in Tidal ControlControl management that works your way

Personnel & onboarding

Employee compliance without the spreadsheet

The Personnel module turns employee compliance (onboarding, policy acknowledgements, role assignments) into a self-service flow for your team. No more chasing email confirmations or maintaining a separate spreadsheet of who has accepted which policy.

Personnel & onboarding in Tidal ControlEmployee compliance without the spreadsheet

Integrations

Automation makes life more fun!

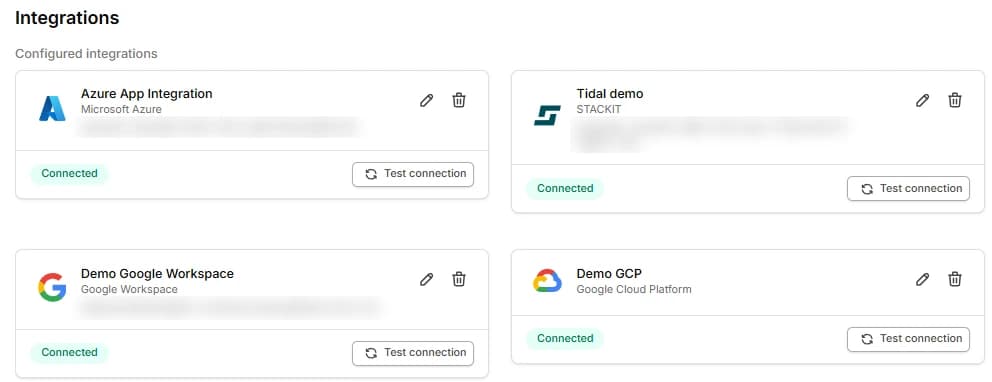
Our integrations collect and evaluate evidence for you, saving you the time of preparing system reports and screenshots every time you need to run a control test.

Integrations in Tidal ControlAutomation makes life more fun!

Manual vs. with Tidal Control
  • Privacy controls

    Manual
    Separate documents per GDPR duty

    With Tidal

    Pre-mapped per role with owners

  • Processors

    Manual

    Processing agreements in a folder

    With Tidal

    Recorded per party with reassessment

  • Data subject requests

    Manual

    Worked out each time

    With Tidal

    A procedure with owner and evidence

  • ISO 27701 and ISO 27001

    Manual

    Two systems side by side

    With Tidal

    One system, evidence once

  • Audit preparation

    Manual

    Weeks of scrambling before the audit

    With Tidal

    Always audit-ready

Testimonials

What our customers say

With a single click, one Tidal test checks dozens of disks for encryption. Doing that manually would take a lot of time.

Profile picture of Chiel Bos
Chiel Bos
COO·CBYTE
CBYTE logo

See all success stories

Integrate with your existing tools

ISO 27701 software and certification

A privacy programme has many separate parts: a record, lawful bases, DPIAs, processing agreements, procedures for requests and breaches. Without a link between them it goes stale quickly and nobody knows what is in place.

ISO 27701 software brings those parts together in one management system, with owners, review dates and evidence. You see per role which controls apply and whether they work.

Privacy is then not a collection of documents but a system you can have audited.

Frequently asked questions

ISO 27701 sets out the requirements for a Privacy Information Management System (PIMS). In the 2019 edition it was an extension to ISO 27001; the 2025 revision made it a standalone standard with the same harmonised structure as ISO 27001 and ISO 42001, so the two integrate cleanly without one depending on the other.

Not since the 2025 revision, which removed ISO 27001 as a prerequisite. If you hold a certificate against the 2019 edition, check the transition deadline your certification body applies. Most organisations still run both, and our platform helps you implement them in an integrated manner, reducing duplication and maximising efficiency.

ISO 27701 provides structured controls that address GDPR requirements, helping demonstrate accountability and appropriate technical and organisational measures. While not GDPR-specific, it's recognised by supervisory authorities as evidence of systematic privacy management.

Yes, our platform includes controls for both data controller and data processor roles. We help you implement appropriate measures based on your specific data processing activities and relationships.

Yes, ISO 27701 certification demonstrates privacy maturity to customers and partners. It's increasingly requested in vendor assessments, particularly for organisations processing personal data on behalf of others.

Our platform continuously monitors privacy controls, tracks data processing activities, and maintains required documentation. You'll receive alerts for actions needed, helping you maintain both privacy compliance and certification efficiently.